

In the recent era, hackers are constantly evolving and using their techniques to execute new attack vectors to target users from different sectors across the globe, as reported by the security researchers at Cyble.
The spyware campaign that currently uncovered mainly targeting the Indian military personnel, and since January 2021 this campaign has been active.
The cybersecurity experts of Cyble along with 360 Core Security Lab have recently detected the PJobRAT spyware in dating and instant messaging apps. Not only that even, the analysts have also claimed that the spyware samples disguised themselves as Android dating apps.
Since December 2019 the recent version of PJobRAT spyware has been around, as reported by the researchers at 360 Core Security Lab.
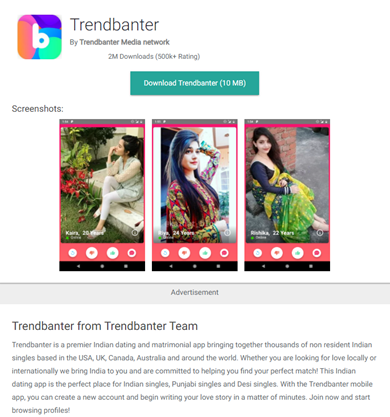
While during their investigation they detected that for Non-resident Indians this recent variant is disguising as a famous dating app known as “Trendbanter,” and mimicking the instant messaging app, Signal as well.
Data collected by PJobRAT via fake apps
- Contacts
- SMSes
- GPS data
Other apps used
In some cases, the researchers have identified that it also imitate other apps as well, and here they are mentioned below:-
- HangOn
- SignalLite
- Rita
- Ponam
Moreover, through different medium and third-party app stores, the threat actors accomplish their distribution goals in which they distribute all these spyware.
While the experts have asserted that to hide in the app list, it imitates WhatsApp or any genuine-looking app. But, the most bizarre thing is that it doesn’t even match the icon shown in the app store with the installed one.
Types of Documents it Exfiltrates
The types of documents that it able to exfiltrate from the infected device are mentioned below:-
- .doc
- .docx
- .xls
- .xlsx
- .ppt
- .pptx
The complete list of abilities of PJobRAT spyware is mentioned below:-
- Upload address book
- Upload SMS
- Upload audio files
- Upload video file
- Upload image file
- Upload a list of installed apps
- Upload a list of external storage files
- Upload WiFi and GPS information
- Upload geographic location
- Update phone number
- Recording via the mic or camera
- Upload WhatsApp contacts and messages
In terms of its code, the spyware remains the same, and not only that even it also interacts with the same infrastructure as well.
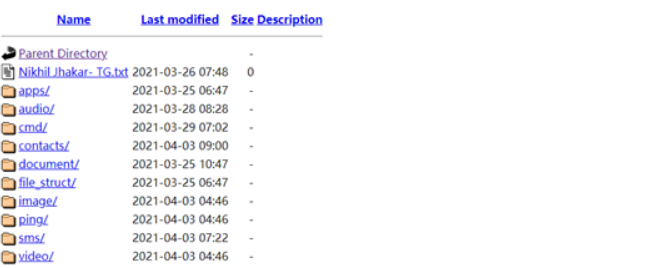
But, the analysts have affirmed that the threat actors behind this spyware are not so sophisticated, since their private servers are publicly accessible in which they hold the exfiltrated data.
The security researchers at 360 Core Security Lab has concluded that the threat actors behind PJobRAT spyware could be Chinese or Pakistani hackers, and that’s why their primary goal was to spy on Indian military personnel.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.







