

PC games are quite famous and they are being played by a number of people all over the world, but as per the report the PC games have led to a massive rise in threats that had targetted PC gamers.
Threat actors are targeting the PC gamers because the pandemic and lockdown have given major popularity to the games, nowadays every people play PC games and mostly the youngsters.
Recently, the security researchers of the Kaspersky security lab have announced that this month they have detected a number of malware and undesired software pretending as popular PC games. And as per their reports, the threat actors have transcended 5.8 million from Q3 2020 to Q2 2021.
However, after detecting the attack, the experts of Kaspersky has started investigating it, soon they came to know that these attacks were pretending to be the 24 most popular PC games.
Moreover, the experts have found 2.48 million detections all over the world, when pandemic-related lockdowns hit in Q2 2020. After the detection, they compared the attack rate with the previous year and noted that there is a 66% increase in the attack.
The number of attacks in this year is 636,904 attacks, which is slightly less as compared to the previous year. While the security analysts have claimed that this situation is quite crucial, and the mobile initially reflected that of the PC world with a 185 percent surge people were being attacked by malicious software posing as games.
But, among the 24 PC titles, Kaspersky has initially listed, the top five games with a tremendous amount of disguise malware, and here they are:-
- Minecraft
- The Sims 4
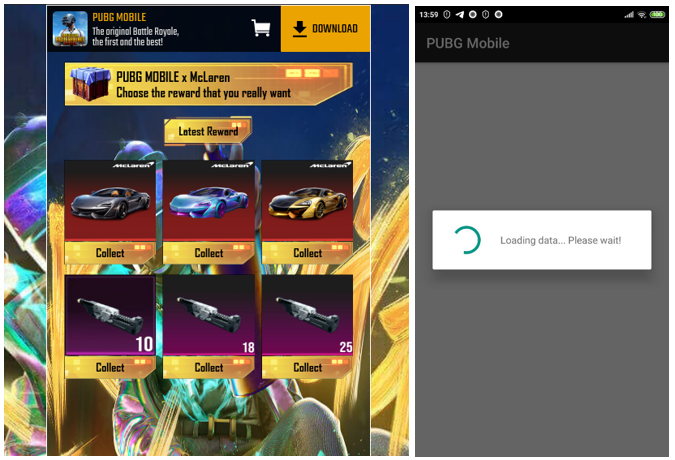
- PUBG
- Fortnite
- Grand Theft Auto V (GTA V)
Kaspersky experts’ recommendations
The cybersecurity analysts have suggested some recommendations, that is to be followed to keep the gamers safe:-
- Always use a strong password and a unique one for each and every account.
- Always download your apps from official stores such as the Apple App Store, Google Play, or Amazon Appstore.
- Try to avoid downloads of pirated software and other illegal content.
- Follow a reliable security solution as it will provide great help especially if it won’t slow down your computer while you play.
- Always use a robust security solution to defend you from malicious software and its effects on mobile devices.
Apart from this, they have concluded that they are trying their best to identify every key detail and tracking each incident. Since, in these type of events, the threat actors use Trojan-Stealers, crypto-miner, and Trojan bankers to steal valuable data.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.







