

CosmicStrand is a new and sophisticated UEFI firmware rootkit that has been attributed to an unknown Chinese-speaking hacker.
In a study conducted by Kaspersky Lab, researchers came up with the name CosmicStrand for this attack.
Earlier, however, malware analysts at Qihoo360 discovered a variant of the threat known as Spy Shadow Trojan that was similar to the latest one.
In the case of the target machines, it is unclear how the hacker infected the firmware images with this UEFI firmware rootkit.
It has been discovered, however, that the malware has been found on computers with motherboards from the following brands:-
- ASUS
- Gigabyte
UEFI Rootkit
The UEFI is software that is installed as part of the operating system on a computer that acts as a bridge between the operating system and the firmware in the hardware firmware that runs the operating system.
Before any operating system or security software can be loaded into a computer, UEFI code has to run first in order to boot up that computer.
In addition to the difficulty of detecting malware inserted in the UEFI firmware image, it also has remarkable endurance as well. It might be possible to remove it from your computer, but in that case, you will need to either reinstall the operating system or replace the storage drive since it is generally not possible to do so.
To accomplish the task, hooks must be set up in the OS loader to modify it. Thereafter, the entire execution flow will be controlled by the hooks.
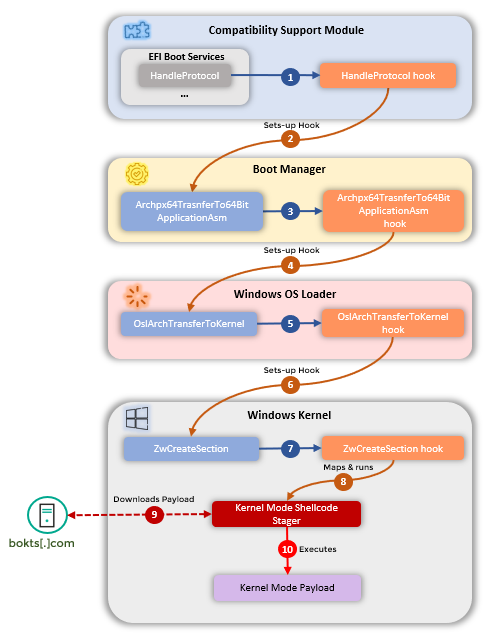
According to the report, In order for the shellcode to be launched, it has to be loaded from the command and control server from which the payload will be downloaded.
A modified CSMCORE DXE driver was included in the compromised firmware images, which enabled legacy booting processes to be used.
After MoonBounce, the second strain of UEFI rootkit is CosmicStrand, which is a mere 96.84KB file, that was discovered this year.
Targets
A malware infection was detected on a victim’s computer by antivirus software in China after a victim reported that their computer had created a new account without them knowing it.
A number of systems that have been identified as being infected and had not been linked to any organizations or industries have been found to belong to private individuals in the following countries:-
- China
- Iran
- Vietnam
- Russia
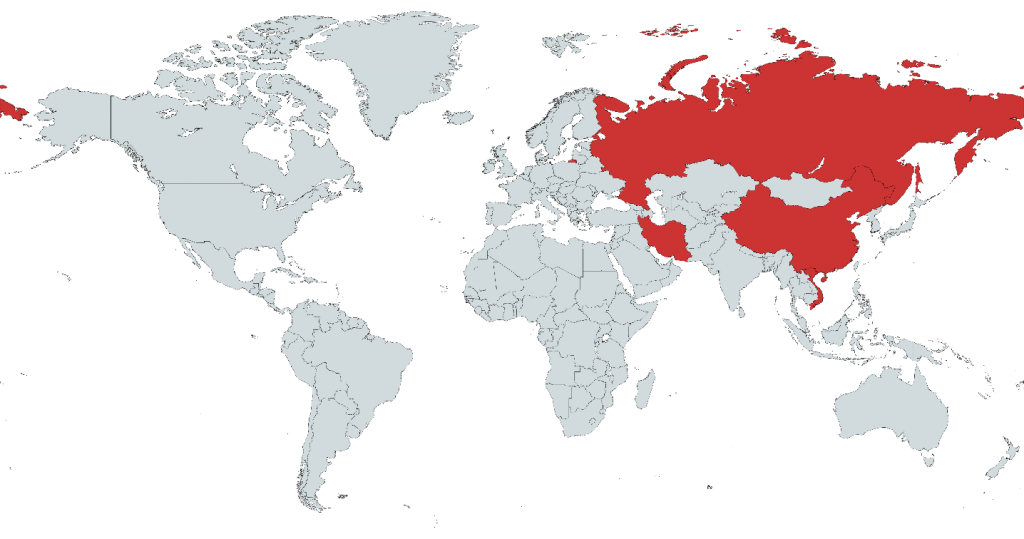
Since the end of 2016, the CosmicStrand UEFI firmware rootkit has been used in operations for years, with the rootkit capable of persisting on the computer for the rest of its life.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity updates.







%20(1).png?fit=728,380&ssl=1&description=CosmicStrand is a new and sophisticated UEFI firmware rootkit that has been attributed to an unknown Chinese-speaking hacker.)