

In the context of phishing attacks, a BazarCall style attack is a form of targeted phishing that uses a call-back methodology in order to trick the user.
For the first time, this emerged to be marketed in 2020/2021 as a tool of Ryuk which was later rebranded under the name Conti. The tool has been ascertained to be an effective and adaptable tool for an entire line of criminals and has proven to be useful.
Increasingly, callback phishing tactics are used by scammers to trick their victims in order to gain access to their personal information. And not only that even the current threat landscape has been completely transformed by callback phishing tactics.
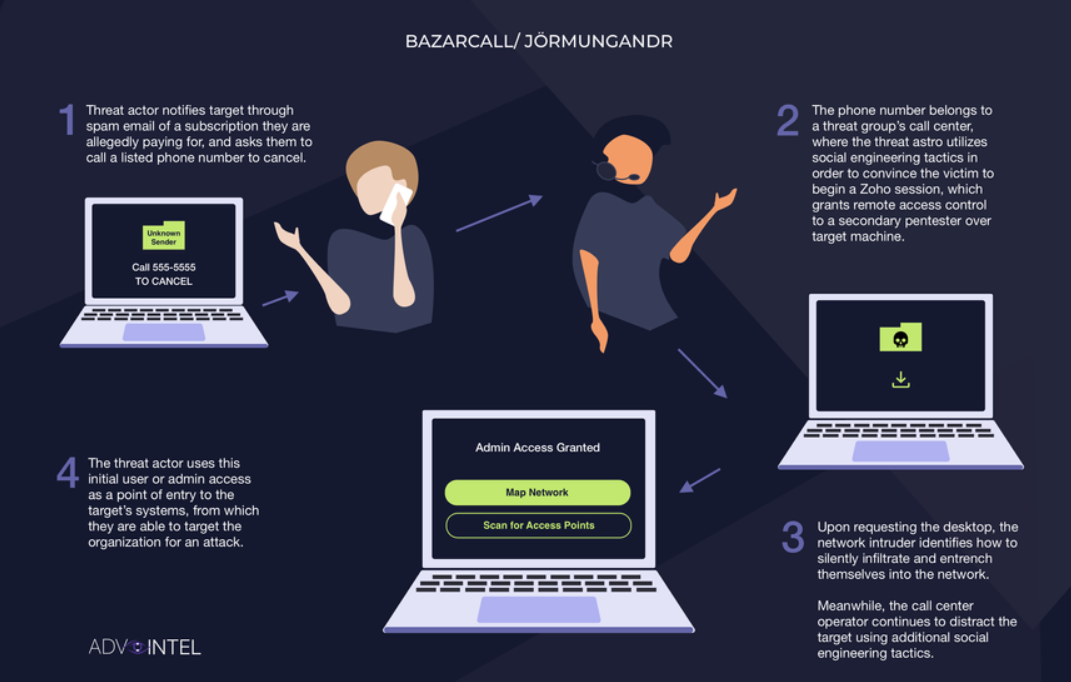
According to the report, So far, three threat groups that are autonomous have devised their own targeted phishing tactics, and here they are mentioned below:-
- Silent Ransom
- Quantum
- Roy/Zeon
Technical Analysis
Essentially, call-back phishing has revolutionized the way ransomware has been targeting its victims again, since the operations resurgence and the post-Conti era.
A widespread change in the approach to ransomware deployment was possible due to the use of callback phishing as a tactic. The uniqueness and effectiveness of the approach can be attributed to the following factors:-
- Before an attack campaign begins, the victim or victim industry is selected using a targeted selective approach instead of an automated botnet infection.
- The phishing campaign is tailored to the victims/industry instead of generic Emotet spam.
- To increase the risk for the targeted victim, weaponize/maximize risk frameworks are developed instead of chaotic extortion strategies.
- There is no repetition of strategies in the campaign, but constant change is made to the content to make sure that it is relevant for the audience.
- It is evident that the main focus is now shifting from data encryption to data exfiltration, rather than the traditional focus on data encryption.
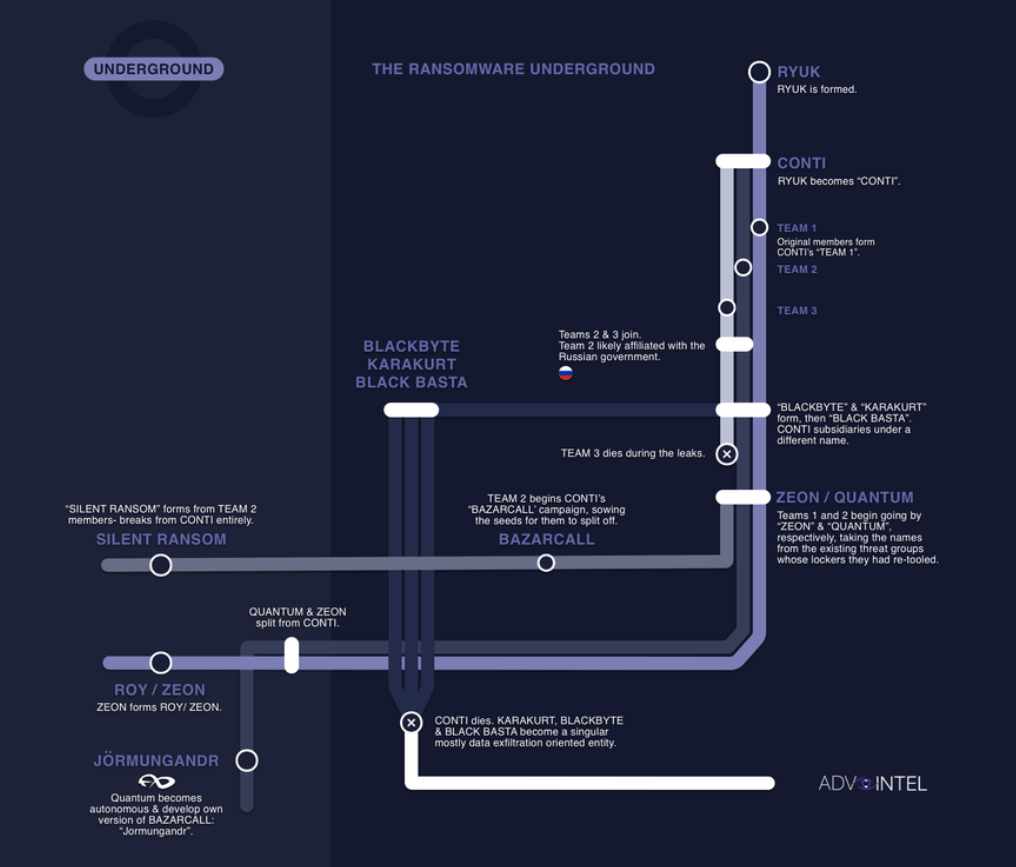
As part of Conti’s organizational tradition, callback phishing is embedded and has been used as an attack vector for some time. Between December 2021 and February 2022, Conti’s operational crisis began, and during February-March 2022, it was conceptualized and implemented.
Victimology
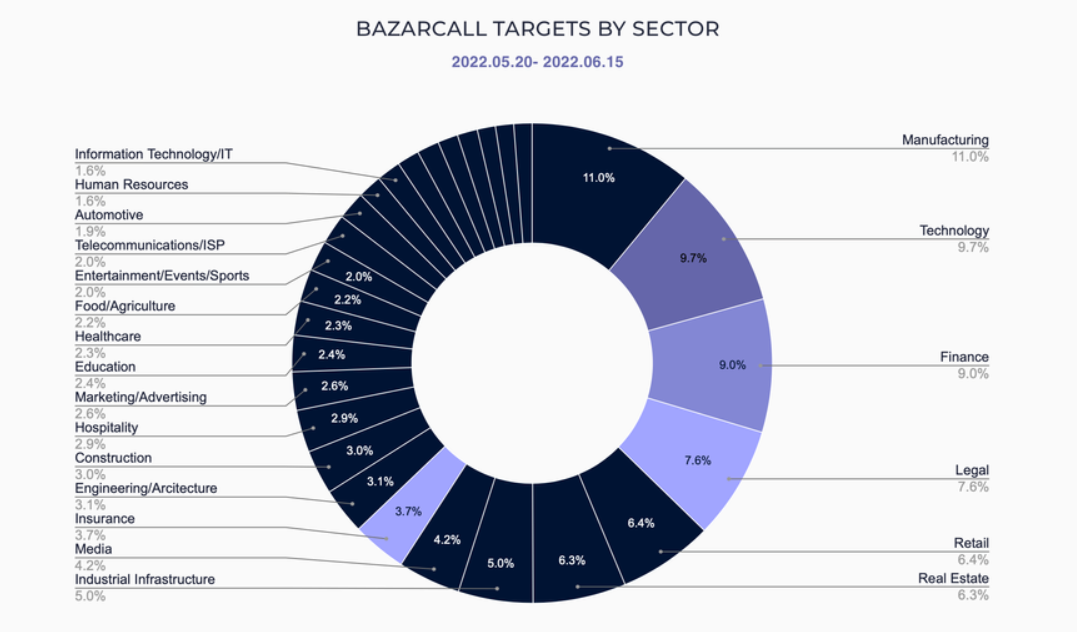
A major shift has been observed in ransomware’s victimology as a result of callback phishing campaigns. Avaddon (such as a group that was active before the advent of the Bazar), is a good example of the change in sectors targeted in comparison to pre-Bazar groups.
These targeted campaigns have significantly increased the number of attacks on the following sectors as a result of their targeted nature:-
- Finance
- Technology
- Legal
- Insurance
In almost all internal manuals that were distributed between ex-Conti members, these four sectors were listed as priority industries.
There is a likelihood that this trend will continue. It has become more evident to threat actors that weaponized social engineering tactics have considerable potential.
The scope and complexity of these phishing operations are only likely to increase as time goes on, so it is predicted that they will only grow.
Sponsored: Rise of Remote Workers: A Checklist for Securing Your Network – Download Free White paper







