

If you are a gamer and looking for cheats and cracks for games then you should be aware that YouTube has become a target for malicious video tutorials that target people looking for cheats on YouTube.
For the purpose of spreading the malicious package even further, the threat actors are advertising these fraudulent tutorials with fake cheats and cracks for popular video games.
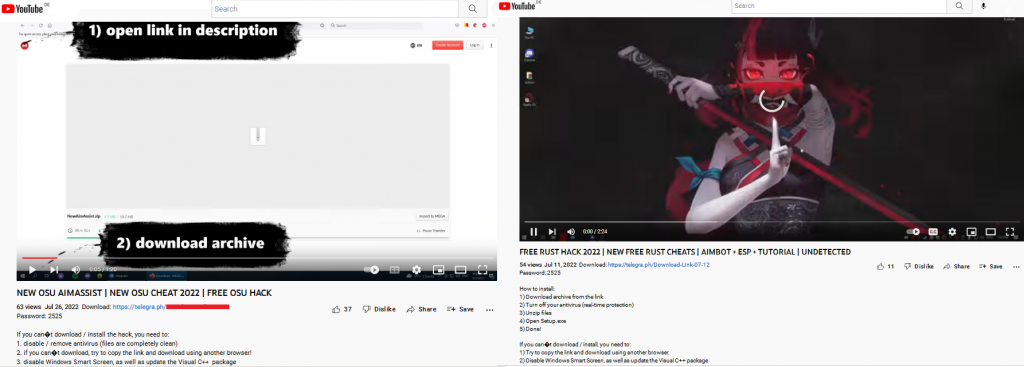
Popular Games Targets
There have been YouTube videos promoting a bundle of self-replicating malware targeted at fans playing the following video games:-
- APB Reloaded
- CrossFire
- DayZ
- Dying Light 2
- F1® 22
- Farming Simulator
- Farthest Frontier
- FIFA 22
- Final Fantasy XIV
- Forza
- Lego Star Wars
- Osu!
- Point Blank
- Project Zomboid
- Rust
- Sniper Elite
- Spider-Man
- Stray
- Thymesia
- VRChat
- Walken
Links to fake cheats and cracks are embedded in these malicious video tutorials. However, the target actually installs the self-spreading malware bundle that disguises itself as cracks and cheats.
Technical Analysis
A team of researchers at the Kaspersky security lab discovered recently an archive containing a bunch of malware that was stored in RAR format. This includes one of the most heavily distributed information stealers on the market today, RedLine, which is presently the most prolific.
Various information that can be stolen by RedLine from a victim’s web browser, includes:-
- Cookies
- Account passwords
- Credit/Debit card details
- Access instant messenger conversations
- Compromise cryptocurrency wallets
Along with several malicious files, the RAR archive also contains a miner that utilizes the graphics card of the victim to mine cryptocurrency.
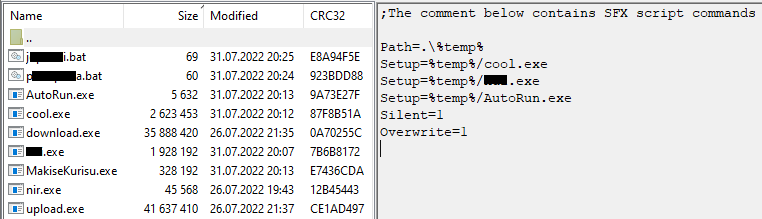
The following three executable files are run immediately after the file has been unpacked:-
- cool.exe
- ***.exe
- AutoRun.exe
As mentioned above, the first product in this category is the RedLine stealer. The second one is a miner, which comes as no surprise, because gamers are the main target audience for the threat actors.
Nirsoft’s NirCmd utility, nir.exe, is present in the bundle, and due to this, the victim will be unable to see any windows in the interface, and no taskbar icons will be generated in the taskbar when this program is launched.
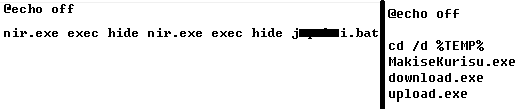
Three malicious executables are contained in the RAR package. These executables are:-
- MakiseKurisu.exe
- download.exe
- upload.exe
These files are responsible for the execution of the bundle’s self-propagation. Meanwhile, the threat actor receives a notification that a new upload has been made.
In reality, if the channel owner isn’t an active member of YouTube, then it is unlikely that they’d be aware of the fact that they’re promoting malware on the platform.
Due to this aggressive distribution method, it is even more difficult for YouTube to do a thorough investigation and take down illicit videos.
SWG – Secure Web Filtering –Download Free E-book







