

Trail of Bits researcher Andreas Kellas recently disclosed a 22-Years-Old SQLite bug which has been tracked as “CVE-2022-35737.” The SQLite database library has been found to contain this vulnerability that has a high severity level.
In October 2000 several code changes were made which led to the occurrence of this high-severity vulnerability. Threat actors could exploit this flaw to crash and control programs if they succeeded in exploiting it.
While it has been confirmed that this severe SQLite Bug could be exploited on systems that are based on 64-bit architecture. However, the extent to which a program is exploitable depends on the way it is compiled.
Flaw Profile
- CVE ID: CVE-2022-35737
- CVSS score: 7.5
- Severity: High
- Current Description: SQLite 1.0.12 through 3.39.x before 3.39.2 sometimes allows an array-bounds overflow if billions of bytes are used in a string argument to a C API.
Technical Analysis
Using this issue SQLite Bug, an attacker could execute arbitrary code on the affected system as a result of exploiting the vulnerability. SQLite’s printf functions require attackers to pass large strings as inputs and the format string contains %Q, %q, or %w substitutions.
According to the report, The following are the affected versions as well as the version that has been fixed:-
- SQLite version 1.0.12 was affected by this flaw that was released on October 17, 2000.
- In SQLite version 3.39.2 the flaw was fixed and this version was released on July 21, 2022.
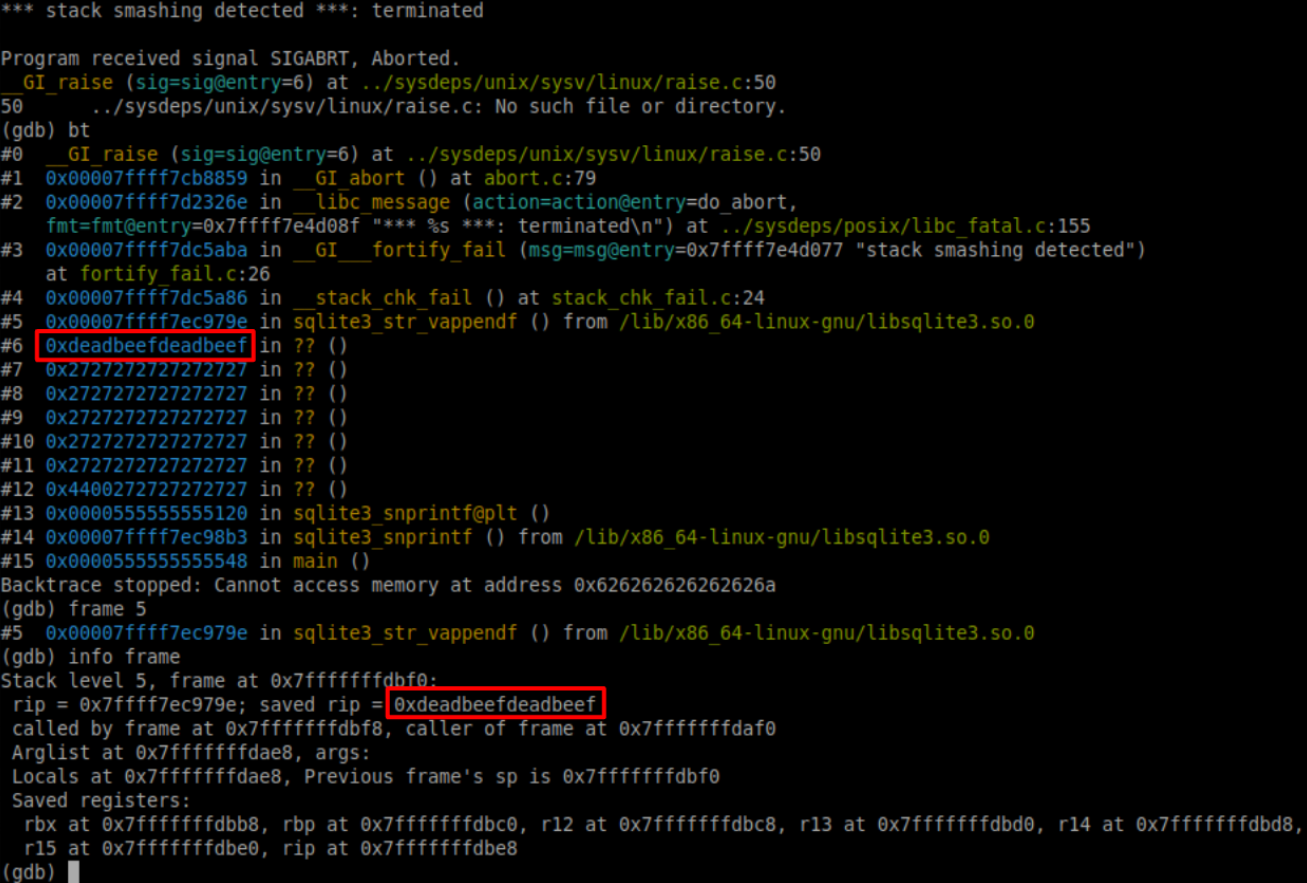
This severe vulnerability has been discovered in the way the string formatting is handled by a function that is known as “sqlite3_str_vappendf” and this function is called by printf.
When a library is compiled without stack canaries, the possibility of running arbitrary code is confirmed. But, the presence of stack canaries implies the execution of arbitrary code, whereas DDoS is always confirmed in all cases.
The SQLite database engine was developed in C and is widely used today. The following operating systems and web browsers include it by default:-
OS:
- Android
- iOS
- Windows
- macOS
Web Browsers:
- Google Chrome
- Mozilla Firefox
- Apple Safari
The SQLite printf function is not vulnerable to widespread attacks in all systems and applications that apply it. Besides being a very serious vulnerability, it is also an example of a scenario that was once considered to be unfeasible decades ago.
Managed DDoS Attack Protection for Applications – Download Free Guide







