

There was an extensive phishing campaign that took advantage of YouTube as a vehicle for promoting the download and installation of cracked software and free games.
In this campaign, attackers are abusing video tutorial that has the intention of tricking users into believing that the link provided in the video description is a link that will download the desired software and that they can install it by following the instructions provided in the video description.
During the investigation, Cyble experts discovered that several of the sites referred to in the video description were phishing websites.
Threat actors have created phishing pages that are aimed at increasing the odds of a successful infection.
Moreover, it is possible to calculate the success of this campaign based on how many views are being received by each of the videos that are posted in this campaign.
Campaigns Analysis
These malicious campaigns mainly target people who are interested in obtaining free software, such as games, programs, etc. in exchange for their email addresses.
In total there are four campaigns that were detected, and here they are:-
- Campaign 1
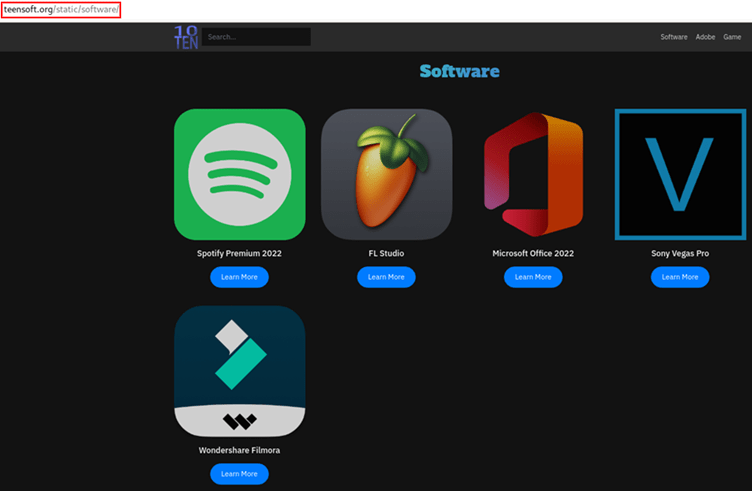
It was found that in campaign 1, there was a picture that indicates that a website hosted on the URL: hxxps://teensoft[.]org/, was used by the YouTube video campaign to distribute Info stealer.
- Campaign 2
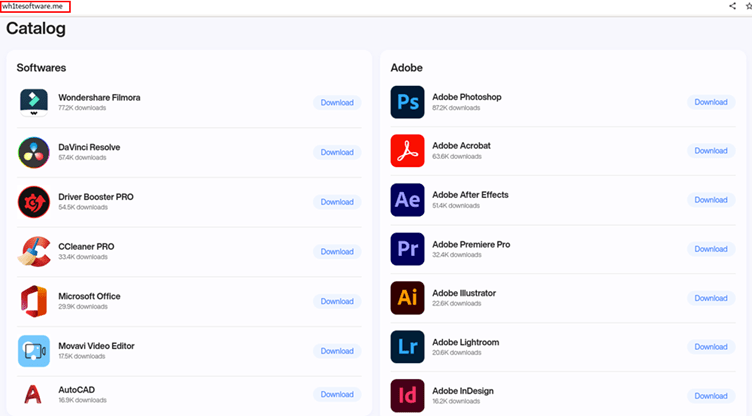
The website hosted on the URL: hxxps://wh1tesoftware[.]me/ is being used in campaign 2 to deliver stealer malware through malicious YouTube videos.
- Campaign 3
As part of the third campaign, the experts found that a YouTube video campaign was using a website hosted under the URL: http://hxxps://soft-exp[.]org/ to deliver malicious files to users who watched the video.
It aims to make people install-info stealers on their computers by presenting a variety of game apps, crack software, plugins, Roblox scripts, and cheats as lures
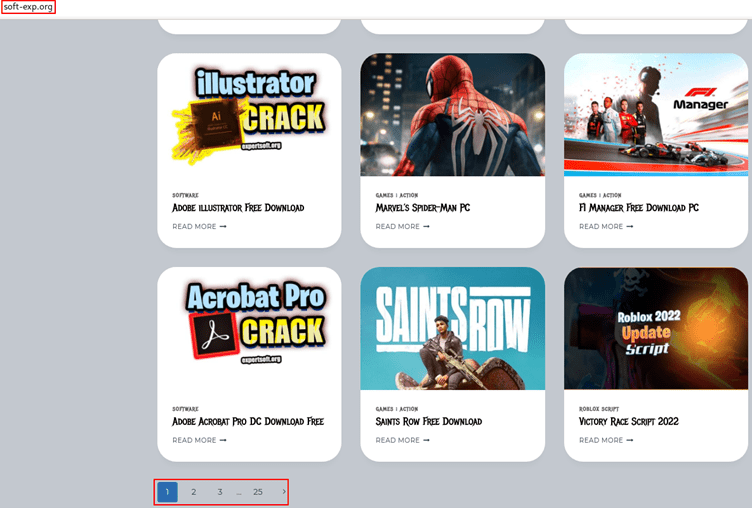
.
- Campaign 4
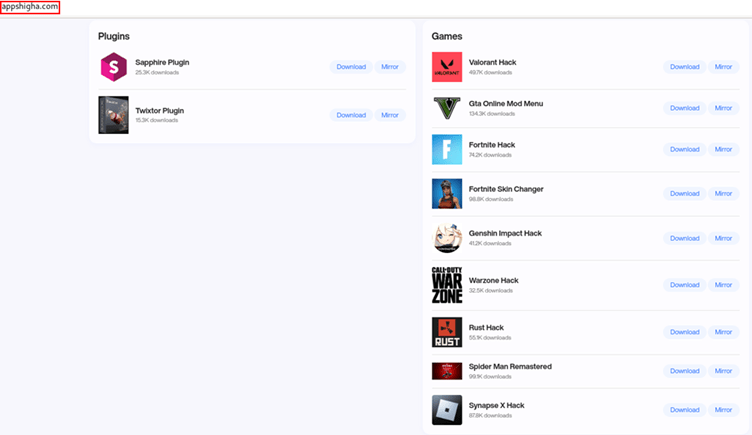
While the fourth campaign involved the use of a website hosted by the URL: hxxps://appshigha[.]com/, whose purpose was to deliver malicious software to the victim’s computer.
The website contains a wide range of free software, which includes:-
- Sapphire Plugin
- Twixtor Plugin
- Valorant Hack
- GTA Online Mod Menu
- Microsoft Office
- CCleaner PRO
- AutoCAD
Vidar Stealer
As of December 2018, this version of the Arkei info stealer was identified as the Vidar stealer. In online forums, there have been reports that threat actors have been able to purchase Vidar for $250.
However, there, the main motive is to steal the following key data and perform illicit activities:-
- Credit cards
- Usernames
- Passwords
- Files
- Taking screenshots
- Stealing wallets for cryptocurrencies (Bitcoin and Ethereum)
RecordBreaker Stealer
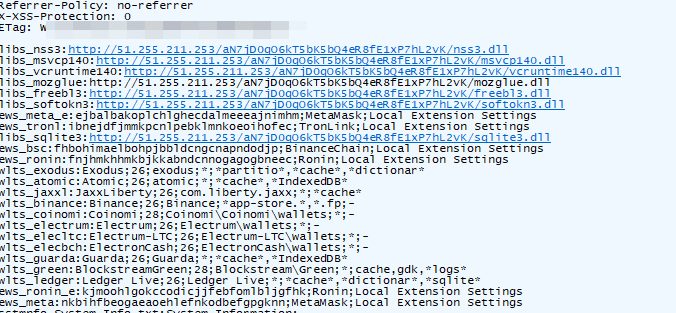
Since the beginning of 2019, several cybercrime forums have offered malware as a service based on the RecordBreaker stealer (aka Raccoon malware).
After one of the Raccoon Stealer’s senior developers died in the Ukraine-Russia war in March 2022, the group was disbanded. According to the configuration settings in the stealer, it is also possible for other malware payloads to be delivered by the stealer.
Recommendations
There is no doubt that threat actors are constantly improving their methods for delivering malicious programs. So, it’s strongly recommended to remain cautious and aware of such evolving TTPs to create the first line of defense against attackers.
While to do so, cybersecurity experts have recommended following the recommendations that they have provided. While we have mentioned all the recommendations below:-
- Make sure you do not download pirated software.
- Do not download anything thing from unreliable websites.
- Ensure that you update your passwords on a regular basis.
- Make sure you have a reputed anti-virus.
- Ensure that email attachments and links are authentic before opening them.
- Be sure to block URLs that could be used to spread malware.
- Data exfiltration by malware or threat actors can be prevented by monitoring the beacon at the network level.
- Implement Data Loss Prevention (DLP) solutions.
Managed DDoS Attack Protection for Applications – Download Free Guide







.webp?fit=728,380&ssl=1&description=There was an extensive phishing campaign that took advantage of YouTube as a vehicle for promoting the download and installation of cracked software and free games.)