

Security analysts at Area 1 Security have recently discovered a new sophisticated Office 365 phishing scam that is targeting the execs of the insurance and financial departments.
The threat actors are hunting down the employees of insurance and financial departments through this Office 365 phishing scam to collect their precious credentials and launch BEC attacks.
According to the reports, the attacks were ignited on last December and maintained till February; while most of the attacks that were executed through this time interval are mainly performed on the financial departments.
The threat actors have mainly targeted the C-suite executives through these sophisticated attacks so that they can work around the Office 365 defenses, and email security.
Apart from this, in this new sophisticated Office 365 phishing campaign, the threat actors have targeted about 40 of Area 1 Security’s clients over various industries.
Not-So-Secure “Office 365 Update”
Before being discovered by the security researchers at Area 1 Security, the very first credential harvesting campaign concerns emails that contain purported instructions on “how to apply an Office 365 security update.”

Hackers have used few simple tactics in the emails to lure the victims, as they have used the “Important Service Changes” note in the subject of the email, that comprised of sender display names with “no-reply” addresses to company-specific names, to make the email real.
Email with malicious attachment and “Apply Update” message
The phishing emails that are sent by the hackers to the victims are sent with full-pack details and attachments. As through these emails, the attacker simply lures the victims and convenience them into opening the malicious attachments sent by them; and all these attachments could be a PDF, HTML, or HTM file.
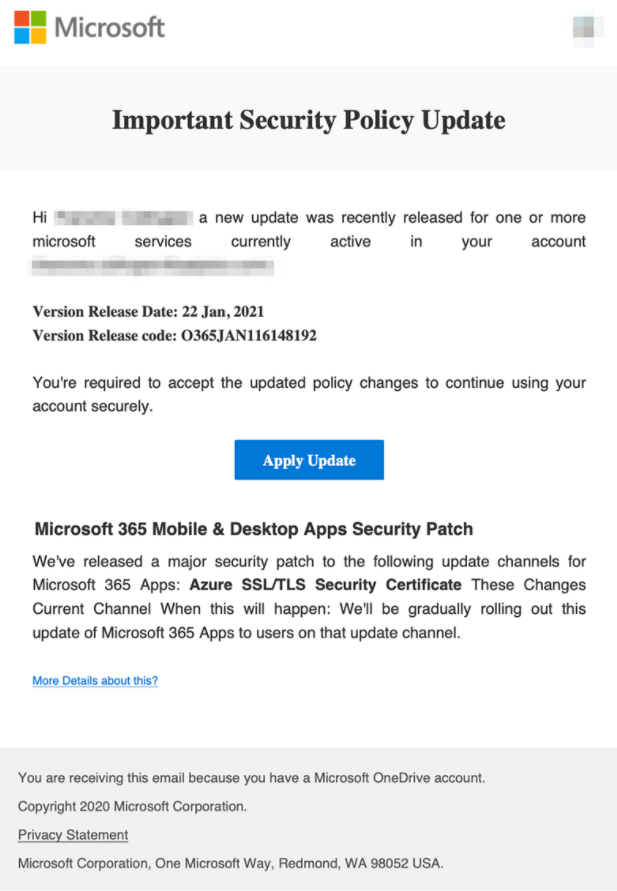
Here, the threat actors create the phishing emails in such a way, that any normal or moderate user will get confused. As they pack all these emails with the following details:-
- Target information
- Full name
- Email address
- Company logo
Microsoft is the Phishing Lure of Choice
Microsoft-related lures which include Office 365, and Teams in BEC attacks have now become a popular medium for the threat actors to administer different types of malicious activities.
The security analysis of the researchers has concluded recently that in 2020 more than 45% of phishing emails that were sent by the attackers were Microsoft-themed.
Now many of you might be thinking that why Office 365? Hackers generally get lured towards Office 365 simply due to its massive treasury of exploitable data.
Moreover, cybersecurity researchers have suggested users to confirm the authenticity of the email before clicking any link or downloading any attachment. While they have also recommended to avoid clicking on any external links from unknown sources.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity, and hacking news updates.







