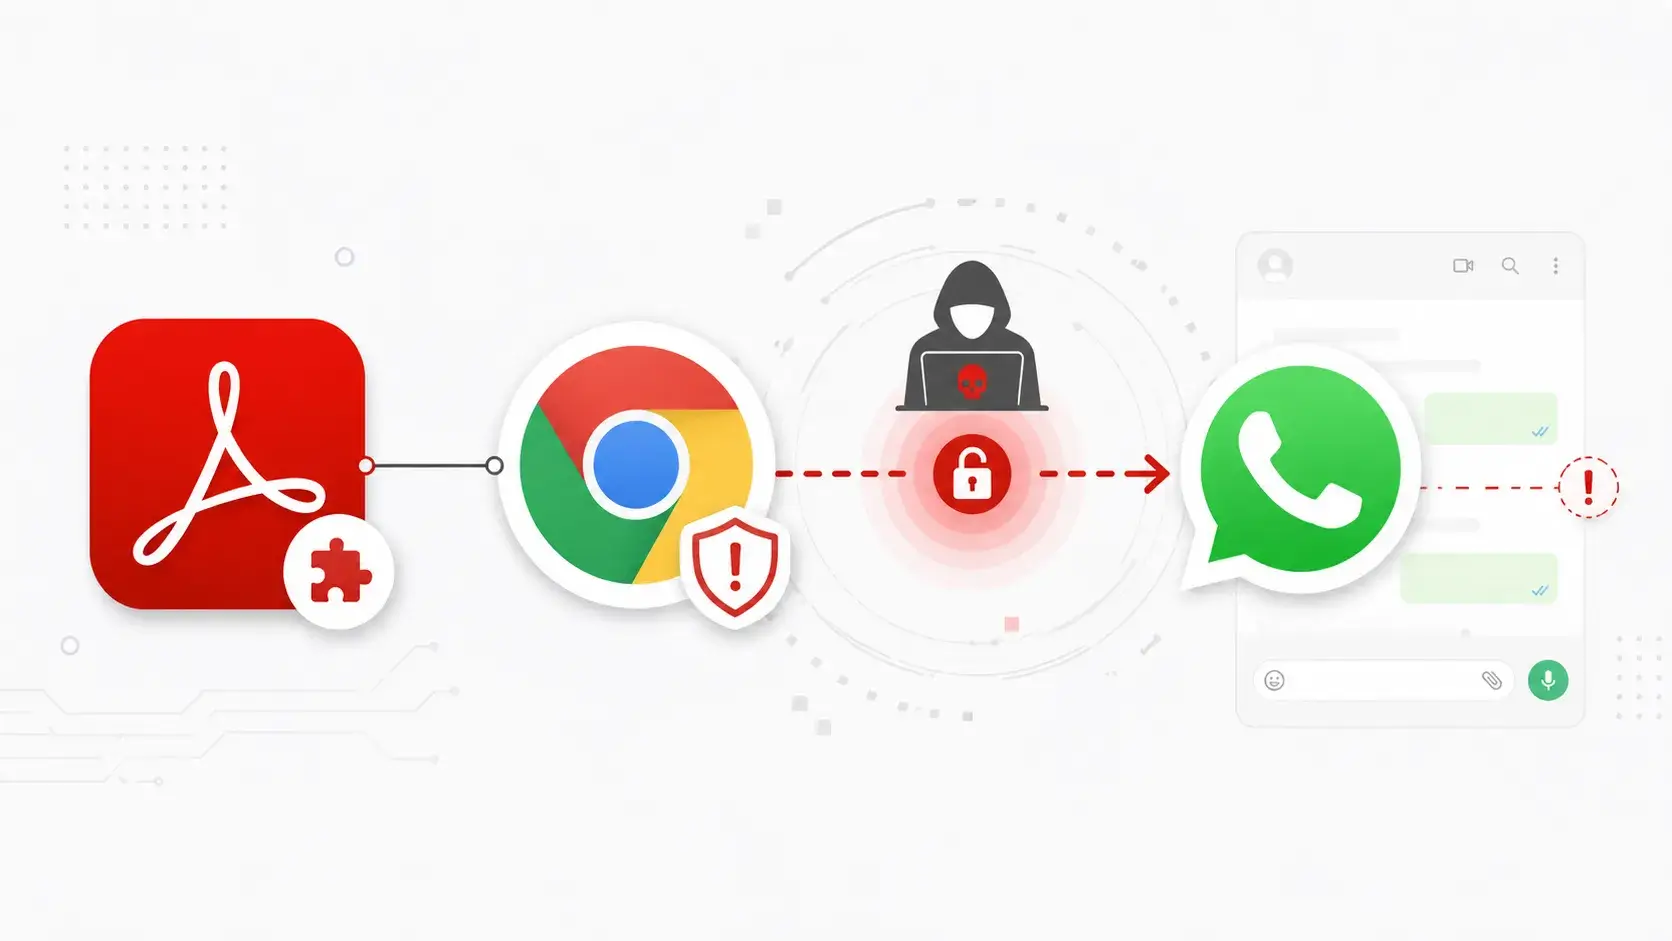

Guardio Labs has disclosed a critical vulnerability chain in the Adobe Acrobat Chrome extension that could allow a malicious website to hijack and exfiltrate rendered WhatsApp Web data from affected users.
This vulnerability is tracked as CVE-2026-48294 and has impacted Adobe Acrobat extension version 26.5.2. The extension is installed across approximately 329 million browsers.
Adobe has reportedly acknowledged the report, developed a fix, and released a patched version of the extension over one weekend following responsible disclosure.
Critical Adobe Acrobat Chrome Extension Flaw “HermeticReader”
The issue, dubbed “HermeticReader” by researchers, did not require malware, phishing credentials, an Adobe account, a WhatsApp vulnerability, or theft of session cookies.
Instead, an attacker could host a malicious static webpage and rely on a victim to simply visit it while signed into WhatsApp Web and using a vulnerable version of the Adobe Acrobat extension.

This vulnerability exploited Acrobat’s newly introduced WhatsApp Web integration, internally known as Hermes, which was designed to support PDF workflows within the messaging platform.
Guardio Labs discovered that several weak trust boundaries could be exploited to turn a webpage into a cross-origin mechanism for exfiltrating WhatsApp data.
First, the extension exposed web-accessible pages that accepted JSON data through URL query parameters. These pages operated with the extension’s trusted ‘chrome-extension://’ origin and relayed attacker-controlled fields to the extension service worker via chrome.runtime.sendMessage. Although one control field was overwritten during processing, much of the message content remained within the attacker’s control.
The service worker reportedly failed to validate the sender of inbound messages. This allowed untrusted websites to invoke storage operations, including arbitrary writes to the extension’s local storage.
Researchers used this capability to alter a developer feature-flag override value, enabling the dormant Hermes integration engine. Specifically, writing the `dc-cv-hermes` value into the `floodgate-add` feature-flag key activated WhatsApp-related functionality without any user interaction.
The next step required identifying the target WhatsApp Web tab. Guardio Labs found a weak hostname check that trusted domains beginning with strings like “www.google..”.
An attacker-controlled hostname resembling `www.google.attacker-domain.com` could satisfy this condition and trigger an Acrobat overlay flow.
This flow inadvertently exposed the attacker page’s Chrome tab ID through an injected extension iframe. Since Chrome tab IDs are allocated sequentially, the attacker could open WhatsApp Web in a new tab and predict its ID.
With the expected WhatsApp Web tab ID, attackers could send Hermes commands to Acrobat’s content script inside the WhatsApp page. The content script accepted a broad range of privileged DOM operations without authenticating the sender.
These commands included injecting HTML, manipulating arbitrary DOM elements, invoking methods on the window, accessing storage values, and relaying messages back to the extension service worker.
Although WhatsApp’s content security policy prevented straightforward script injection, researchers demonstrated a more subtle path for exfiltration.
The exploit injected an attacker-controlled form into WhatsApp Web, manipulated DOM nodes to move the live WhatsApp page body into a form option element, and submitted the form to an attacker-controlled server.
Because an option element without a value attribute submits its text content, the resulting POST request could include rendered WhatsApp Web text, such as chat lists, contact names, message previews, profile details, and visible conversations.
This vulnerability highlights the risks associated with browser extensions that bridge websites, privileged extension APIs, and third-party messaging platforms.
Guardio Labs noted that its AI-assisted research workflow expedited the discovery process by unpacking and analyzing hundreds of obfuscated JavaScript files, mapping service worker message flows, and identifying reachable attack paths in hours rather than weeks.
Users are urged to ensure that the Adobe Acrobat Chrome extension is updated to the latest version. Organizations should also review their browser extension inventories, prioritize rapid patching for extensions with broad site permissions, and consider limiting unmanaged extensions in enterprise environments.
ALERT: 20+ government sites delivered malware to businesses and citizens. See full attack research to check your own exposure.







