

Recently, the threat intelligence team Group-IB along with the attribution system has discovered a post that is quite unusual, as it has been found in numerous carding panels in the underground forums.
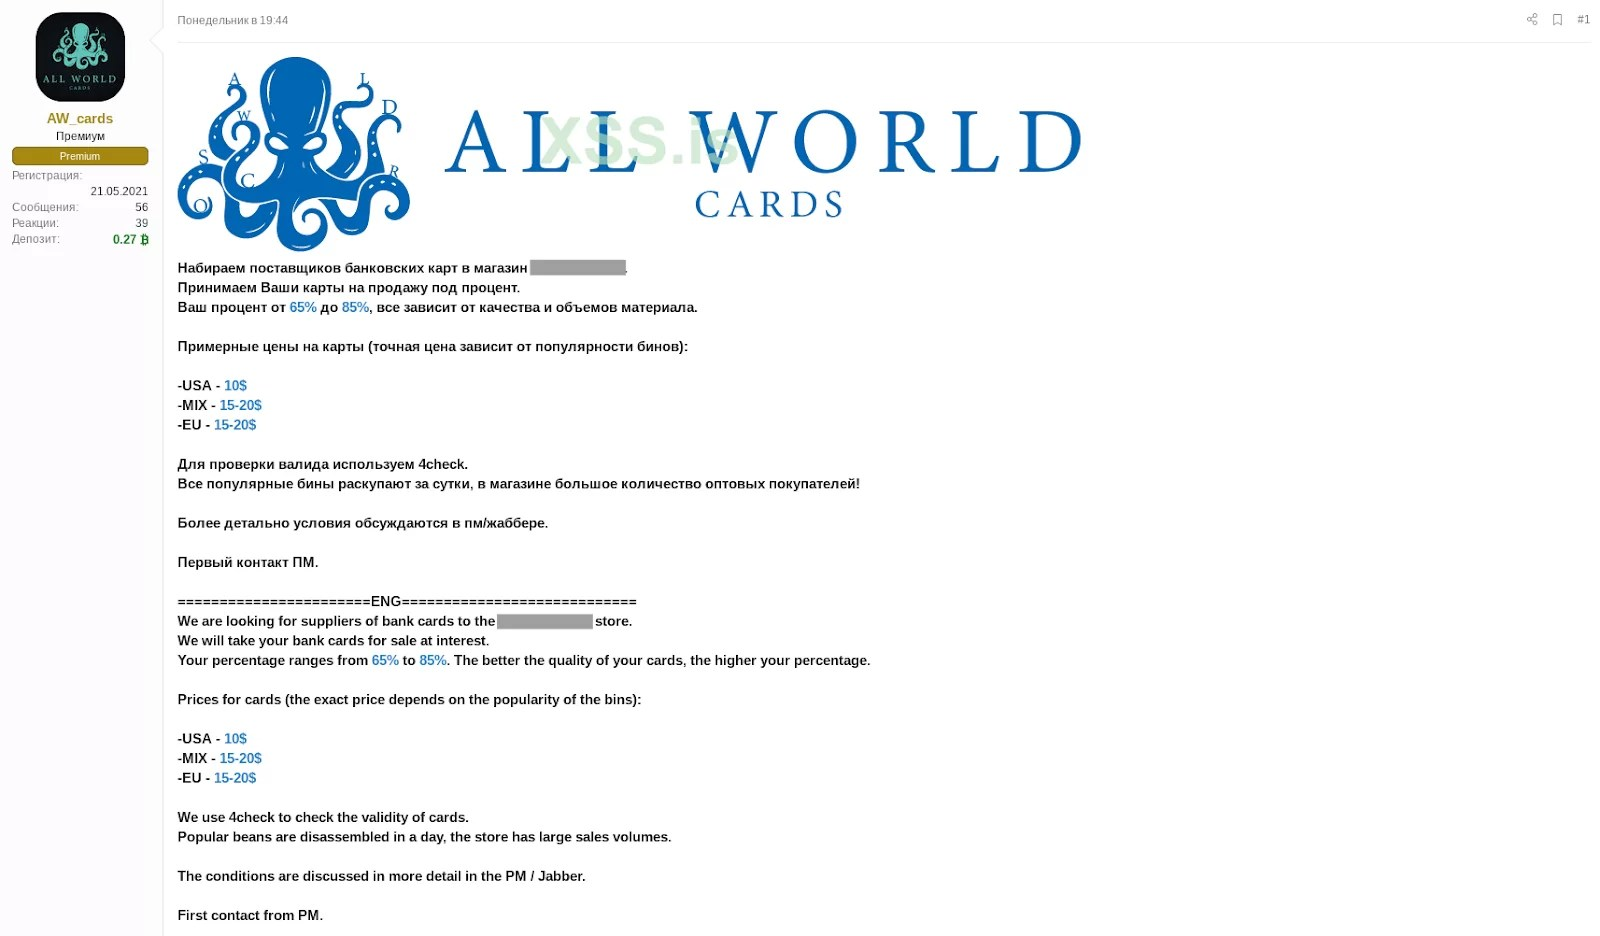
After investigating it thoroughly, the experts found a user named AW_cards, who has posted a link that directly opens up to a file that is having stolen payment records of 1 million bank cards.
According to the report, the file was available for free and it has data from nearly 1000 banks from 100 different countries. However, the analysts have detected that there are countries like Mexico, Australia, Brazil, The US, India, and many more.
Data Stolen
As we said above that the file has been detected by the experts of the Group-IB team and reporter to GBHackers, and they have revealed the types of data that has been compromised by the hackers:-
- Card number
- Expiration date
- CVV / CVC code
- Name of the cardholder
- Country
- State
- City
- The address
- Zipcode
- Phone numbers for some entries
All World Cards
The Group-IB, has gone through each and every detail of this finding, and they detected that the bank data that have been found were claimed to be of 2018-2019 data, but as per the experts, nearly 97% of the records in the database are still valid.
The most interesting part of the investigation of Group-IB is that they have detected 810 expired cards, and out of which 30 of them expired in June 2021, and the rest 780 expired in July 2021.
All World Cards was initially recorded on the forum by the ekxperts of the Group-IB team on May 31, 2021, and All World Cards is an experimental credit card data marketplace.
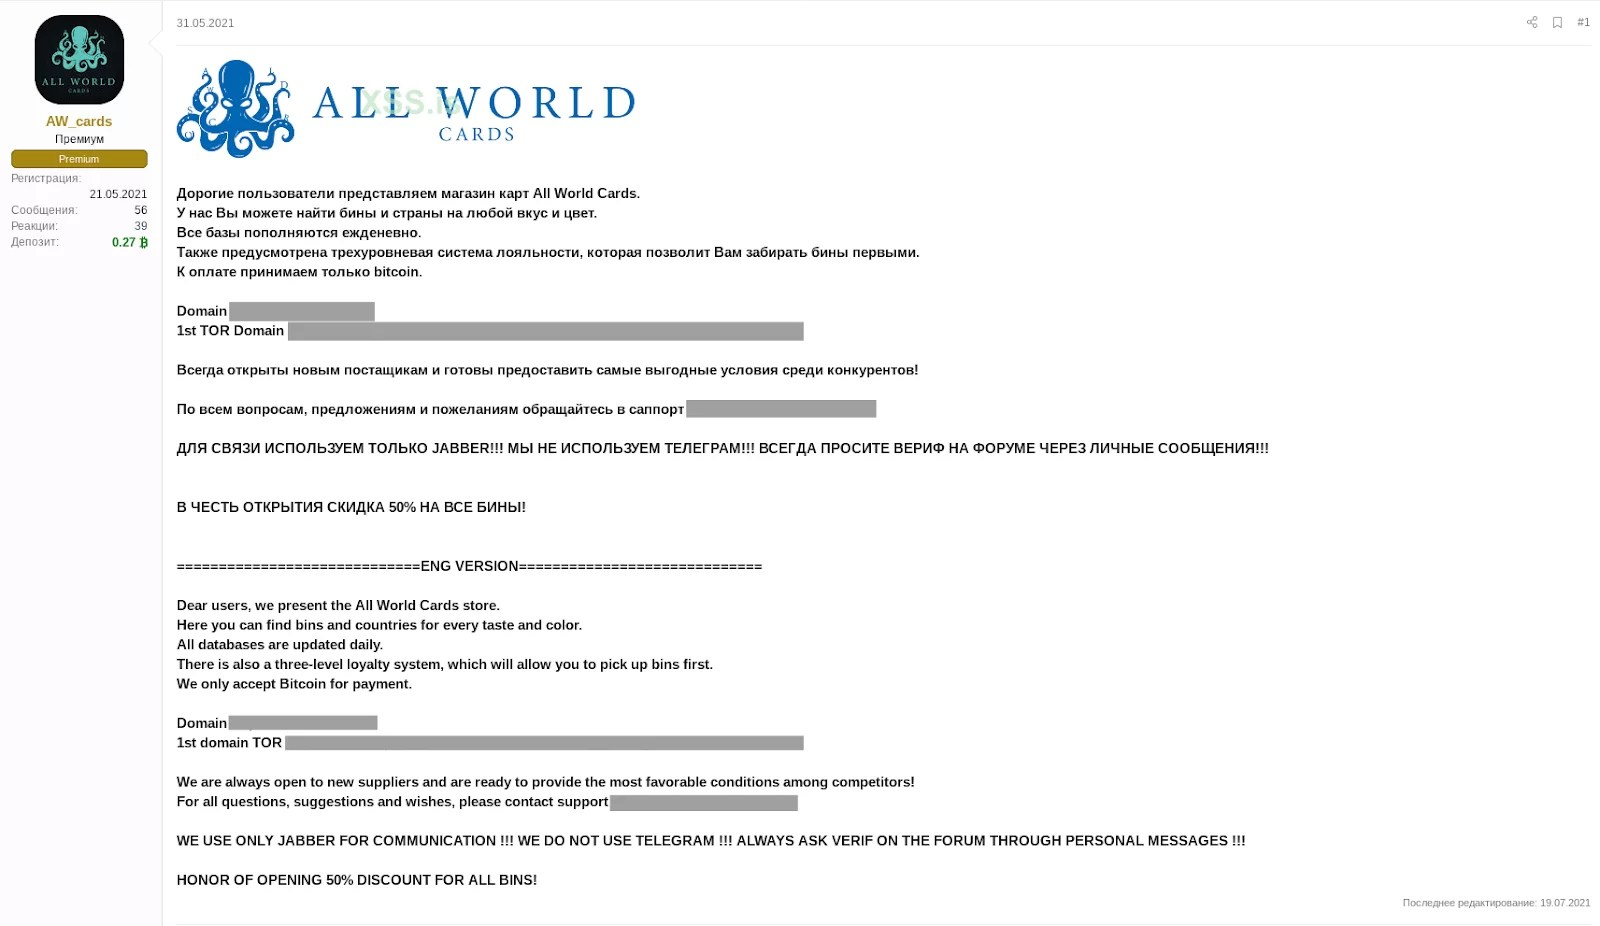
Apart from this, the cybersecurity researchers discovered 3.8 million bank cards that were on sale during their whole investigation, and nearly 2.6 million of them are prepared for the purchase.
While the analysts of team Group-IB have also detected that the owners of the card shop were engaged on various forums that are utilizing two nicknames that are “AW_cards” and “AW_support.”
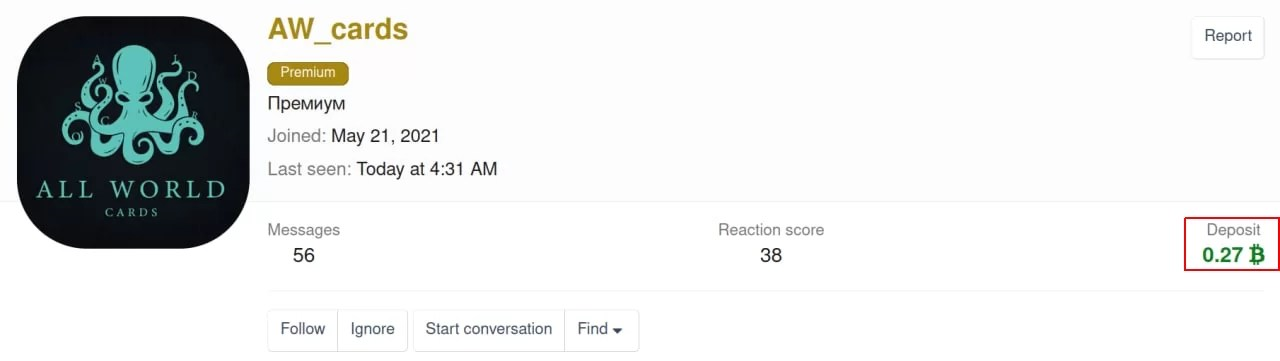
The experts have claimed that the owners of the shop were active for 2 months, and nearly 400 messages were posted from both accounts.
According to the analysts of Group-IB, this case is quite unusual, as hackers are using new methods, and they have a total of 1 million cards allowed for free.
However, this marketplace has come up with a new name and the actions of the owners of the card shop were the same who have developed new policies and sophisticated tactics.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.







