
An active phishing campaign that weaponizes a legitimate NinjaOne Remote Monitoring and Management (RMM) agent to gain persistent remote access to Brazilian organizations.
Rather than relying on bespoke malware, the operators exploit familiar business workflows and Portuguese-language social engineering to trick finance, procurement, accounting and administrative staff into installing a digitally signed NinjaOne agent that connects to attacker-controlled infrastructure.
This undocumented abuse of a mainstream RMM highlights a worrying trend: adversaries increasingly leverage trusted enterprise tooling to minimize detection and maximize operational freedom.
The campaign begins with carefully crafted phishing emails that route victims through Googleusercontent redirection chains into Portuguese-language landing pages.
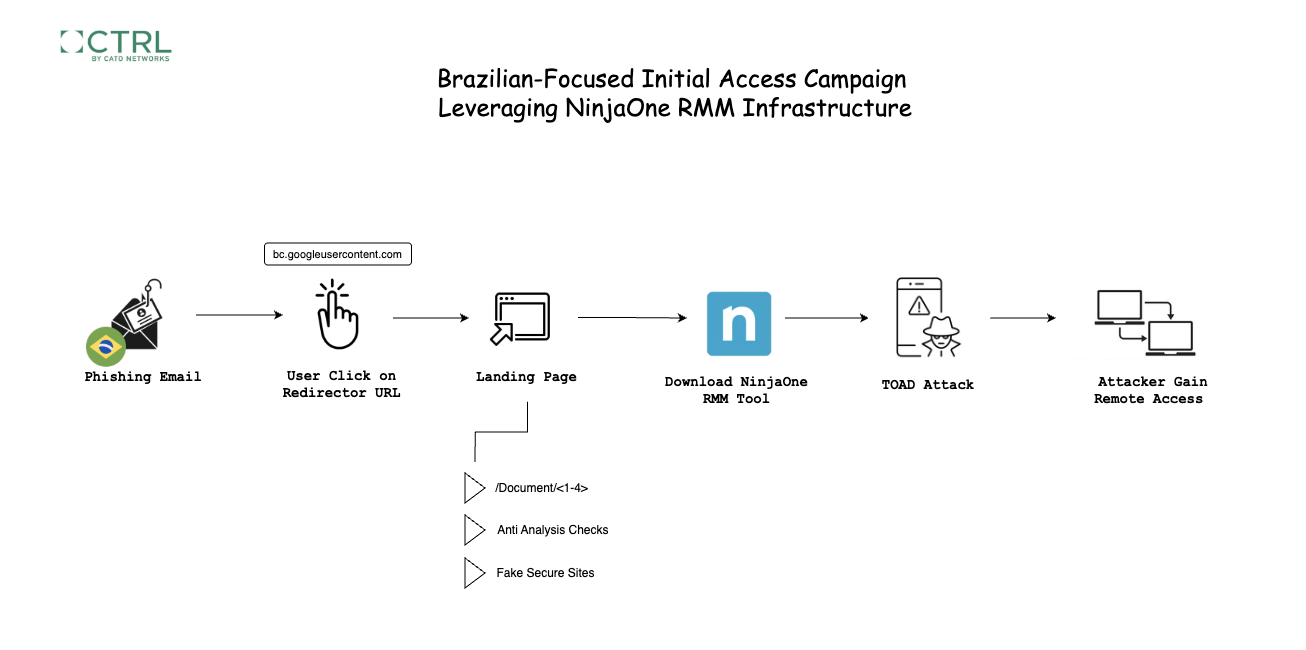
Those portals impersonate recognizable Brazilian processes SEFAZ-related fiscal documents, complaint-management sites styled after Reclame Aqui, and secure document-delivery services using localized language such as “Documento Fiscal”, “Download Seguro” and “Verificação de Segurança” to build confidence.
Cato CTRL researchers recently identified an undocumented, active phishing campaign targeting Brazilian organizations with fake business-document lures.
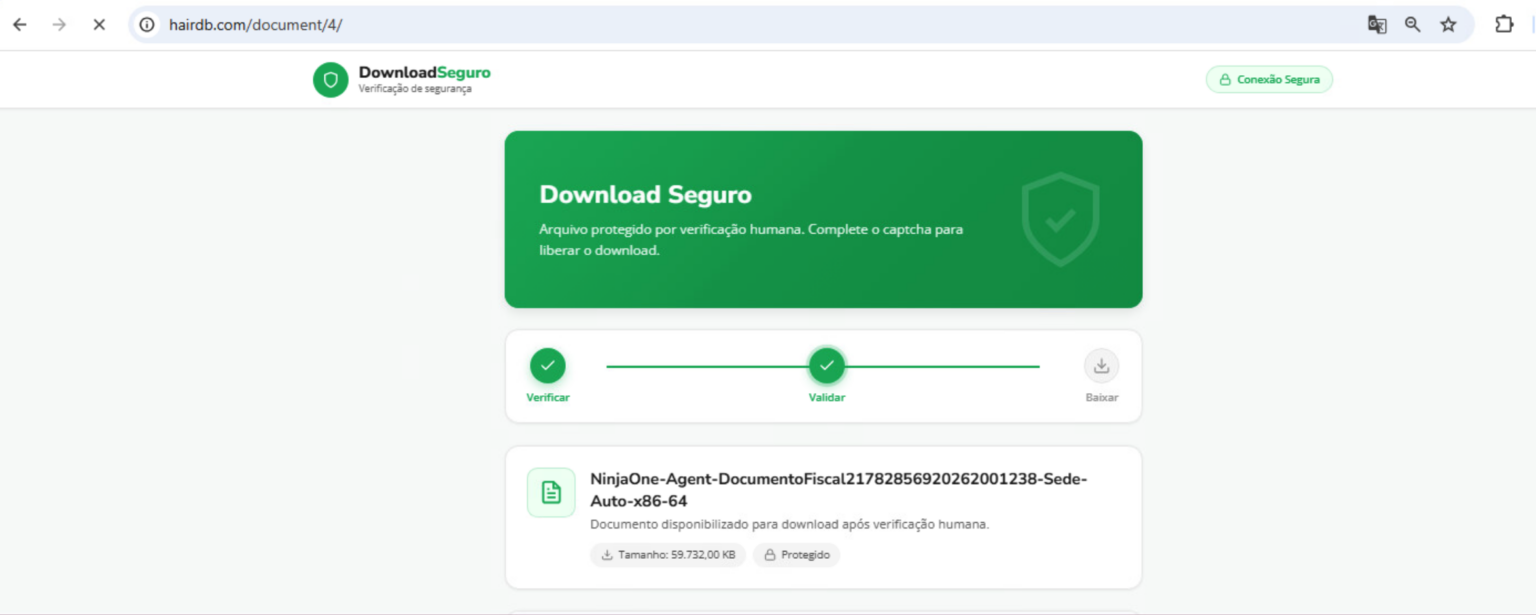
After a mock verification flow, victims click a download button that, instead of returning a document, delivers a legitimate NinjaOne installer configured to register with attacker-controlled management endpoints.
Hackers Abuse NinjaOne RMM Agent
Filenames bolster the ruse by embedding fiscal document identifiers and site context, for example: NinjaOne-Agent-DocumentoFiscal21782856920262001238-Sede-Auto-x86-64.
Technical controls in the phishing infrastructure demonstrate clear operational maturity. The operators employ geofencing to gate payload delivery to Brazilian IP ranges, browser fingerprinting to detect automation frameworks and sandboxes (Selenium, Puppeteer, Playwright, WebDriver artifacts, PhantomJS), and behavior checks mouse movement, scrolling and touch events to validate human presence.
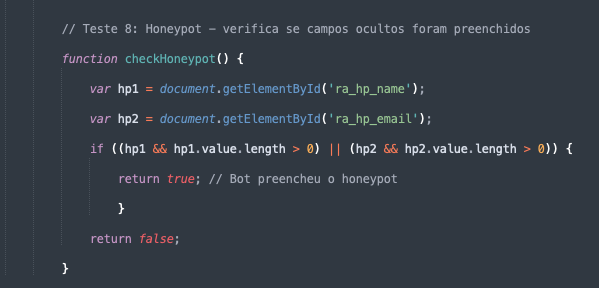
Honeypot fields and developer comments in JavaScript reveal deliberate anti-analysis intent; one Portuguese comment translates to “The bot filled the honeypot.”
Cloudflare fronting further obscures backend hosts, while a simple download mechanism (?download=1) shows social engineering was prioritized over complex payload-delivery logic. These protections reduce researcher exposure and prolong infrastructure lifespan.
Abusing NinjaOne is particularly consequential because the platform’s legitimate administrative features map directly onto attacker objectives.
As an enterprise-grade RMM, NinjaOne supports endpoint monitoring, remote shell access, file transfer, software deployment, patching and automation capabilities that, when controlled by an adversary, provide reconnaissance, persistent remote access, tooling deployment and lateral-movement opportunities inside victim networks.
The campaign aligns with broader advisories from CISA, NSA and MS-ISAC warning of malicious RMM misuse.
Cato CTRL’s analysis focused on a victim in the chemicals and advanced materials sector, but the lure template is broadly applicable across sectors handling fiscal documents and supplier communications.
Infrastructure pivots uncovered through operational artifacts most notably a reused Earth-themed wallpaper expanded visibility into related domains, illustrating how trivial reused assets can reveal large portions of an attacker ecosystem.
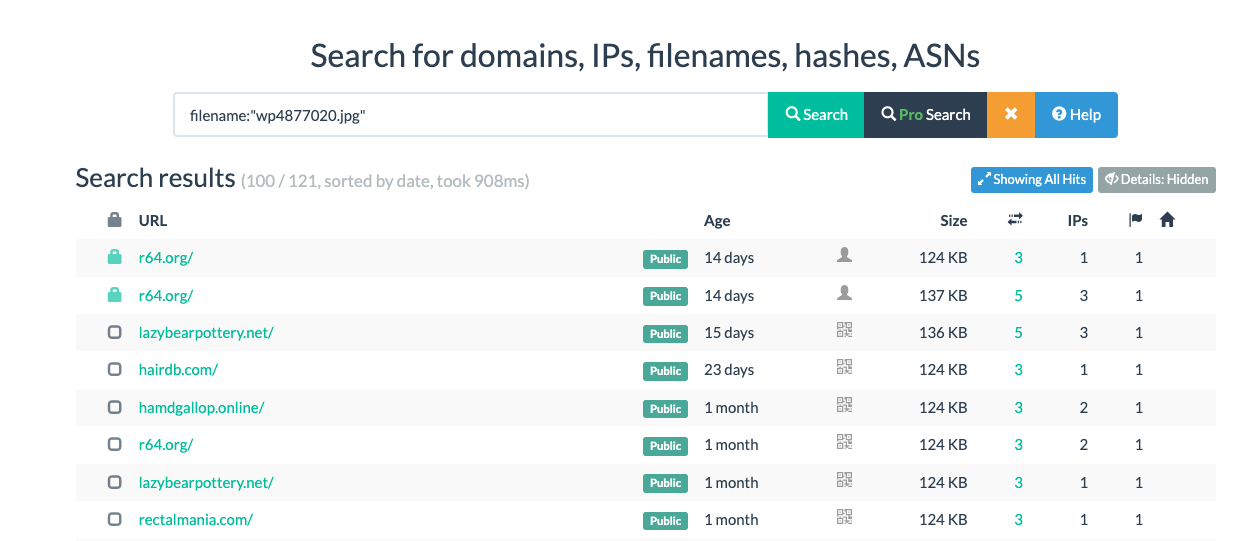
Investigators also found overlaps with infrastructure previously linked to Venon RAT activity in Brazil, though attribution remains tentative and would require additional evidence.
At the time of the report (June 3, 2026), portions of the phishing infrastructure remained accessible despite responsible disclosure. Organizations should treat unexpected document-download prompts with suspicion, verify distribution channels directly, and enforce robust endpoint controls and allowlisting for RMM installations.
Additionally, consult vendor guidance and the joint CISA/NSA/MS-ISAC advisory on malicious use of RMM platforms for defensive recommendations.
Indicators of Compromise
Domains
r64[.]org
hairdb[.]com
lazybearpottery[.]net
rectalmania[.]com
sefaz[.]services
reclameaqui[.]services
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


 agent to gain persistent remote access to Brazilian organizations.)