

The cybersecurity company Check Point of Israel has spotted a new malware and named it Electron Bot. This malware has the ability to control different social media accounts that are specifically being distributed via Microsoft’s official app store.
The most important fact is that the malware is being distributed in the form of trojanized gaming apps. However, this malware is quite serious as it has been affecting more than 5000 windows machines in the following countries:-
- Bermuda
- Bulgaria
- Russia
- Spain
- Sweden
Infection Chain
The infection chain of this malware is quite similar to most of the other malware campaigns, as it also starts with the installation process.
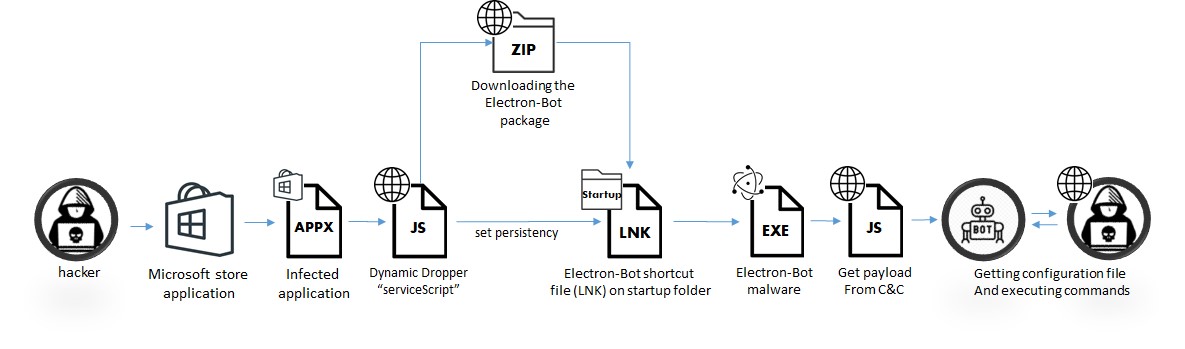
In this, the malware installs the infected application that has been downloaded from the Microsoft Store. And later the Javascript dropper is loaded dynamically from the threat actors’ server, and all this happens when the user launches the game.
Once the installation is done, the threat actors execute different actions that also include downloading and installing the malware so that they can eventually gain persistency on the startup folder.
The Campaign
The malware campaigns initially started when the user downloads the infected application from the Microsoft Store.
However, we can take the example of the game “Temple Endless Runner 2,” which was published on September 6, 2021. The game is created with Electron so most of the files in the folder are linked with the Electron framework.
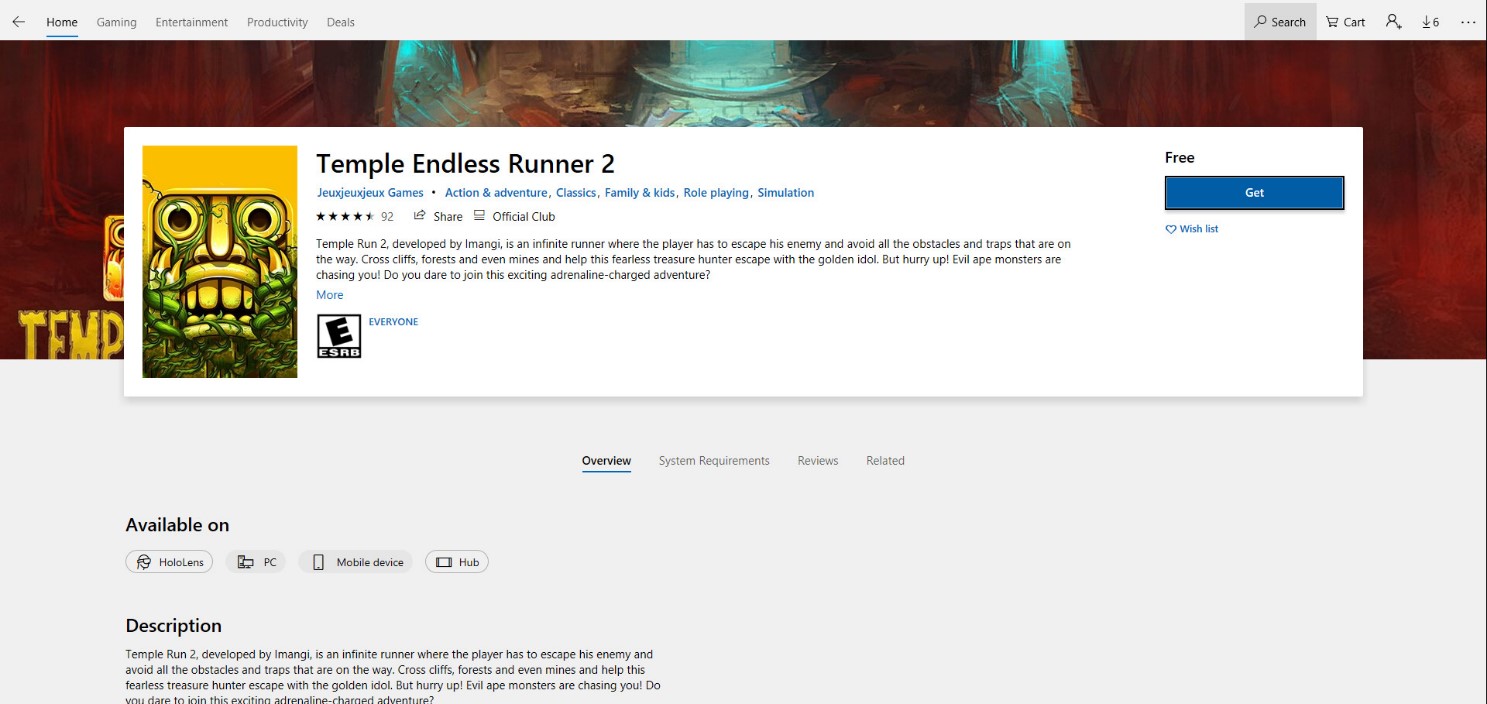
Whenever the user downloads the game the application package file (APPX) gets installed in the following directory:-
“C:\programfiles\windowsapps\16925JeuxjeuxjeuxGames.TempleRun2TakeTheIdolIfYouD_1.1.0.0_x64__66k318ytnjhfe \app”
Main capabilities Electron bot
Here we have mentioned all the main capabilities of the Electron bot below:-
- SEO poisoning
- Ad Clicker
- Promote social media accounts
- Promote online products
- Fraud
Recommendations
The security analysts have suggested some safety tips, and not only this but CPR has also passed on these safety tips too, that’s why we have mentioned all of them below:-
- Try to avoid downloading an application with a small number of reviews.
- Search for applications with good, consistent, and reliable reviews.
- Always pay attention to questionable application naming that’s not similar to the original name.
Electron Bot has nearly attacked 5000 victims all over the world, and it initially infects machines whenever the users try to download any certain apps from the official Microsoft Store platform.
That’s why it’s very important to stay alert so that one can help themselves to stop getting attacked by this kind of malware. And always try to follow the safety tips that we have mentioned above.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.






