

Threat actors actively exploit a new high-severity vulnerability, CVE-2025-0108, in Palo Alto Networks’ PAN-OS.
This exploit allows attackers to bypass authentication, execute certain PHP scripts, and potentially gain unauthorized access to affected systems.
With the widespread use of PAN-OS in enterprise environments, the vulnerability poses a significant security risk to organizations globally.
Active Exploitation in Progress
GreyNoise has identified real-world exploitation attempts targeting this flaw.
The CVE-2025-0108 vulnerability enables unauthenticated attackers to interact with PAN-OS firewalls, bypassing standard authentication protocols and compromising secure networks.
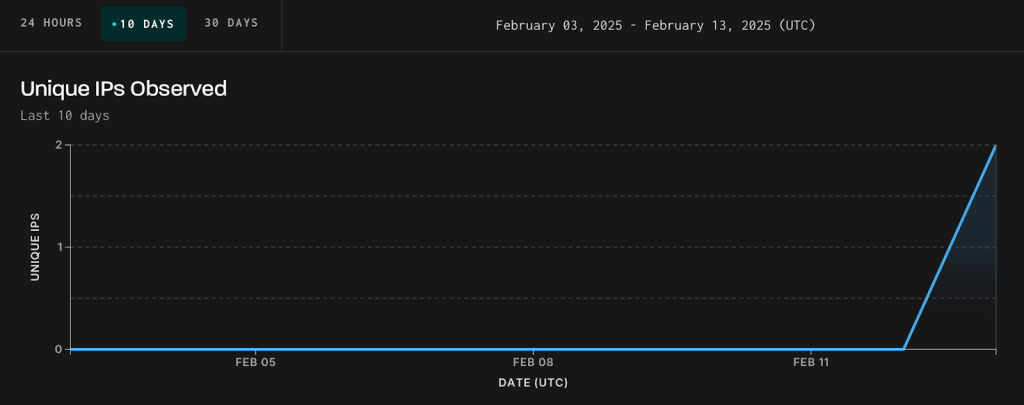
This capability could lead to unauthorized access, data breaches, or further infiltration of critical systems.
Because PAN-OS firewalls are often a frontline defense mechanism for enterprise networks, these exploitation attempts are particularly alarming.
GreyNoise has advised organizations to assume that unpatched devices are being actively targeted in the wild, emphasizing the urgency of taking immediate remediation actions.
Cybersecurity experts warn that the public nature of this vulnerability and the rapid pace of exploitation creates a ticking time bomb for unprotected systems, as adversaries look to take advantage of the security gap before patches are fully deployed.
Organizations must act swiftly to secure their networks and minimize the risks associated with CVE-2025-0108.
GreyNoise is closely monitoring the progression of this threat and will provide updates as the situation evolves.
Organizations are encouraged to utilize real-time intelligence tools to track exploitation patterns and strengthen their defenses.
This incident underscores the critical importance of maintaining up-to-date security protocols for enterprise systems.
Failure to act promptly could expose organizations to significant financial, operational, and reputational damage.
The cybersecurity community must remain vigilant as attackers continue to exploit newly discovered vulnerabilities.
Investigate Real-World Malicious Links & Phishing Attacks With Threat Intelligence Lookup - Try for Free






