

Indian Security researcher found a critical Zero-day vulnerability in “Sign in with Apple” let hackers take over the third-party application accounts by just having their Email ID.
Very Similar to OAuth 2.0, Apple’s “sign in with Apple” helping the user to sign in to their third-party apps and websites faster using their Apple ID without filling out forms, verifying email addresses.
This feature is using million of Apple users to sign in their Third-party apps such as Dropbox, Spotify, Airbnb, Giphy, and the bug considering as “Critical” as it could have allowed full account takeover by the remote attackers.
Bhavuk Jain , Security Researcher from India reported this critical vulnerability to Apple said: “Successfully exploitation of the bug could have resulted in a full account takeover of user accounts on that third party application irrespective of a victim having a valid Apple ID or not.”
The Account Take Over Zero day
Jain explained that Apple using JWT (JSON Web Token) that generated from Apple Server to securely authenticate the user with an Email ID and allow users to log in to the 3rd party app.
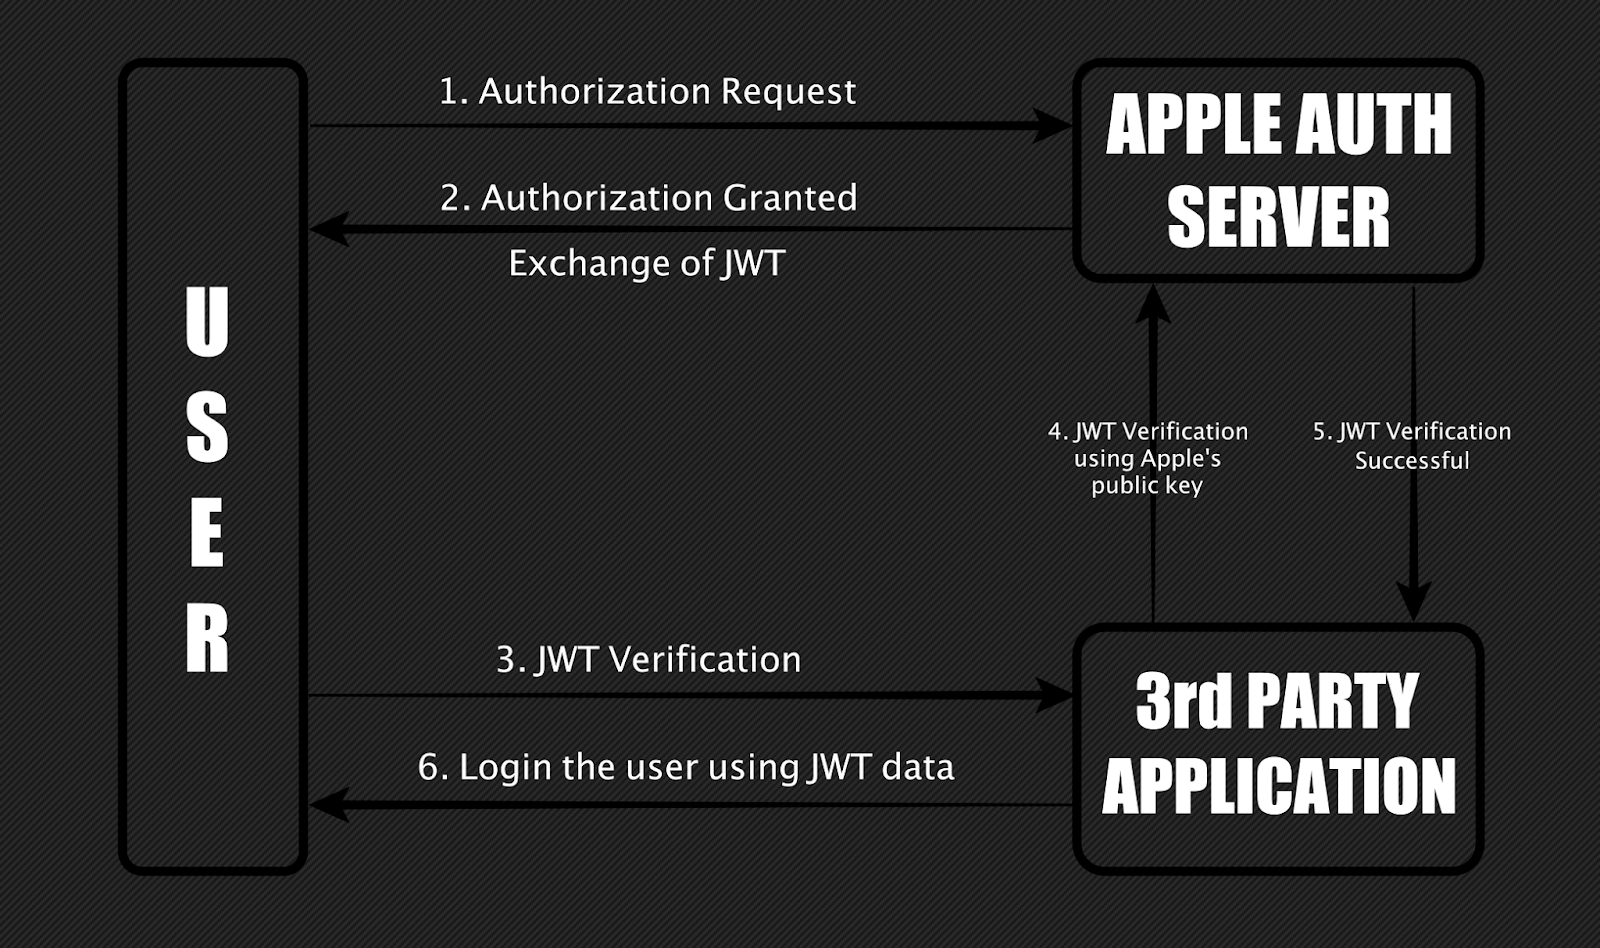
But due to the improper validation, the zero-day bug let attackers request JWTs for any Email ID from Apple and the email ID is verified as valid when the signature of these tokens was verified using Apple’s public key.
It leads an attacker to forge the JWTs to link with any Email ID and gain access to the victim’s 3rd party account.
“I found I could request JWTs for any Email ID from Apple and when the signature of these tokens was verified using Apple’s public key, they showed as valid. This means an attacker could forge a JWT by linking any Email ID to it and gaining access to the victim’s account.” Jain Explained in Blog post.
Jain also confirmed that the bug can also be exploited by the user’s account who decides to hide the Email ID, since Apple generates its own user-specific Apple relay Email ID.
Apple also rewarded $100,000 bounty under Apple security bounty for ethically reporting the critical vulnerability.
Apple security Team confirmed that bug wasn’t exploited after an investigation of their server logs and the bug has been fixed.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.







