

The U.S. Department of Justice has charged 54 individuals in a massive ATM hacking conspiracy that allegedly stole millions of dollars to fund Tren de Aragua (TdA), a designated Foreign Terrorist Organization. U.S. Attorney Lesley A.
Woods announced the indictments returned by a federal grand jury in Nebraska, marking one of the largest crackdowns on “ATM jackpotting” operations in U.S. history.
A December 9, 2025, indictment charges 22 defendants with conspiracy to provide material support to terrorists, bank fraud, bank burglary, computer fraud, and money laundering.
The charges allege that TdA used jackpotting techniques to drain millions from ATMs nationwide, transferring proceeds among members to conceal the illegal funds.
Among those charged is Jimena Romina Araya Navarro, an alleged TdA leader and Venezuelan entertainer previously sanctioned by the U.S. Treasury’s Office of Foreign Assets Control.
Araya Navarro reportedly helped the notorious TdA head, Hector Rusthenford Guerrero Flores, escape from Venezuelan prison in 2012 and has been photographed at social events with the crime boss.
A related October 21, 2025, indictment charges 32 additional individuals with 56 counts, including bank fraud, bank burglary, and computer damage. If convicted, defendants face between 20 and 335 years in prison.
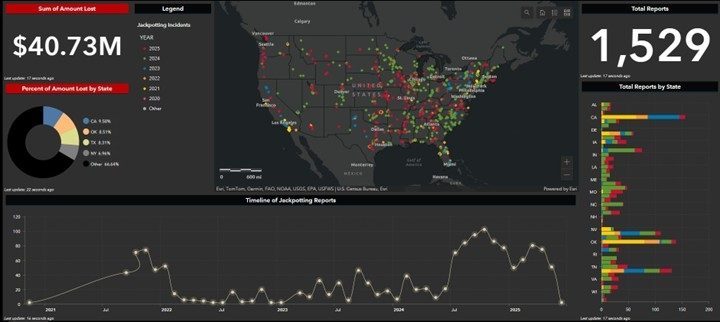
The Ploutus Malware Operation
According to Justice Gov Notification, the conspiracy deployed Ploutus malware, a sophisticated tool designed to hack ATMs and force unauthorized cash dispensing.
Members traveled in groups to conduct reconnaissance on targeted banks and credit unions, noting security features before breaking into ATM hoods.
They installed malware by removing hard drives, replacing them with infected ones, or using external devices like thumb drives.
The Ploutus malware issued unauthorized commands to ATM cash dispensing modules while deleting evidence to avoid detection.
After successful withdrawals, conspiracy members split the proceeds in predetermined portions.
TdA originated as a Venezuelan prison gang in the mid-2000s and has expanded throughout the Western Hemisphere.
The organization engages in drug trafficking, firearms trafficking, kidnapping, robbery, and violent crimes to enforce its operations.
Acting Assistant Attorney General Matthew R. Galeotti emphasized that the Criminal Division “will not tolerate networks of thieves who breach the security of our financial system” to fund terrorism.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.







