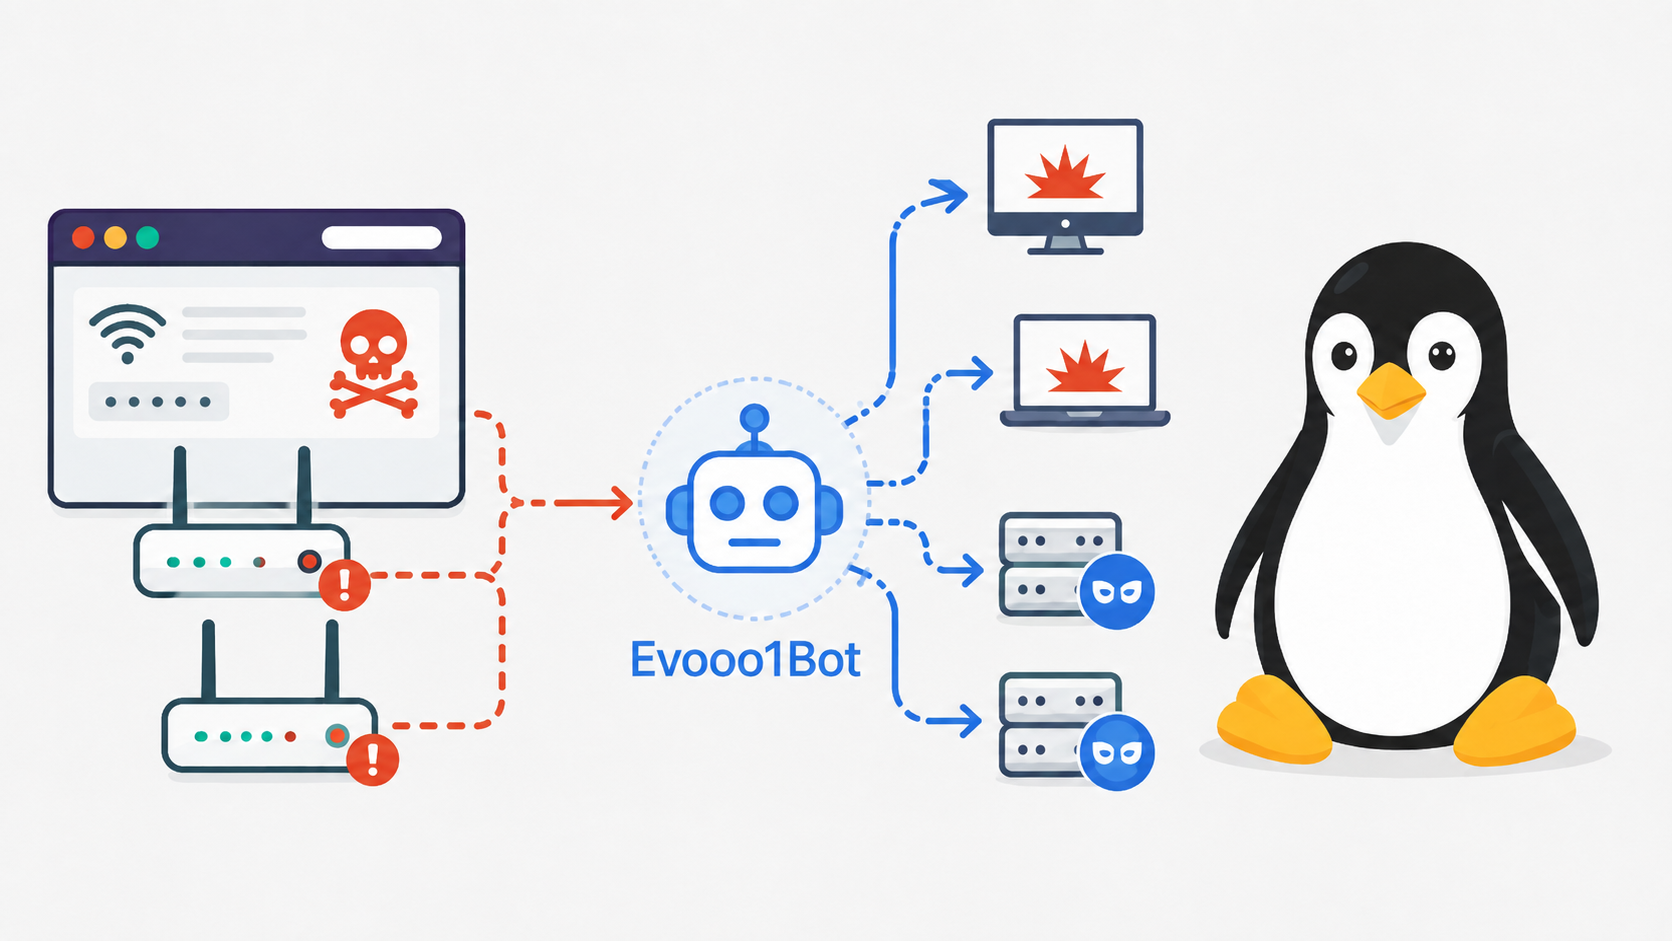

A newly identified Linux botnet dubbed Evooo1Bot is targeting vulnerable internet-facing routers, edge appliances, cameras, and enterprise systems, combining Mirai-derived DDoS capabilities with proxy relaying, credential theft, SSH brute forcing, and exploit-driven propagation.
FortiGuard Labs observed activity beginning in July 2026, with operators using a modular toolset that elevates compromised devices from disposable DDoS nodes to reusable infrastructure for anonymous traffic forwarding and potential network pivoting.
The malware uses encrypted command-and-control communications, layered string protection, anti-analysis checks, a 28-command remote administration interface, file-transfer support, interactive shell access, a credential sniffer, and integrated vulnerability exploitation.
The campaign was identified through IPS telemetry tracking exploitation attempts against a broad set of edge devices.
Observed attacks targeted flaws in Alcatel OmniPCX Enterprise, NETGEAR routers, Tenda routers, Mitsubishi Electric ME-RTU systems, Telesquare devices, and several D-Link products.
The payload chain consistently referenced the loader at 91.92.40[.]118/wget.sh, which selects and executes an architecture-matched payload from 12 available binary variants.
It uses wget, BusyBox wget, curl, or TFTP as fallback delivery mechanisms, then clears Bash history after execution.
Campaign labels embedded in download commands, including -s mitsu and rep.alcatel, suggest the operator measures infection success by vulnerability and target family.

That operational detail indicates an active, data-driven effort to tune exploitation rather than indiscriminate scanning alone.
FortiGuard Labs named the family after the hardcoded string “evooo1” present across its binaries. Although its DDoS engine retains the structural traits of the publicly leaked Mirai source code, Evooo1Bot substantially expands that foundation.
Linux botnet dubbed Evooo1Bot
The malware also includes a separate HTTP-based exploit dispatcher covering targets such as Hikvision cameras, Zyxel firewalls, TP-Link Archer routers, D-Link NAS devices, Atlassian Confluence, WSO2 products, PHP-CGI, and Kubernetes ingress-nginx.
The AES and ChaCha20 keys are not stored directly in the binary. Each key is split into two 32-byte constants embedded in .data and combined at runtime via XOR.
Fortinet noted that some embedded exploit entries contain implementation flaws and are not exploitable as shipped.

Evooo1Bot’s most consequential capability is its SOCKS5 relay. In direct mode, it opens a proxy listener, typically on TCP port 1080.
In reverse mode, the infected host establishes encrypted outbound sessions to an operator-controlled relay server, separating control traffic from individual proxy sessions.

This design allows threat actors to route arbitrary TCP traffic through a victim’s public IP address without necessarily exposing a listening port on the compromised device.
As a result, infected routers and firewalls can be repurposed to obscure attacker origin, evade geographic restrictions, stage follow-on intrusions, or provide access paths toward internal assets.
The botnet also integrates a credential-sniffing module that monitors /proc/net/tcp and captures HTTP Basic Authorization and Cookie headers, storing results in /tmp/.sniff.log. Its SSH scanner carries more than 150 credentials, including enterprise-oriented accounts such as jenkins, postgres, oracle, nagios, and deploy.
Before attempting propagation, it performs banner-based and post-authentication honeypot checks designed to avoid Cowrie, Kippo, and other analysis environments.
For disruption operations, Evooo1Bot supports 16 DDoS techniques, including UDP, DNS, SYN, ACK, GRE, fragmented TCP, and HTTP flooding.
Its persistence function can implant systemd services disguised as an “Apache HTTPD Cache Manager,” SysV init scripts, cron jobs, shell-profile hooks, and rc.local entries.
It also lowers its OOM-killer priority and keeps /dev/watchdog open to reduce the chance that local recovery interrupts execution.
Defenders should urgently patch exposed network appliances, remove unsupported or end-of-life edge devices, restrict administrative interfaces, rotate default credentials, and investigate unexpected outbound TLS traffic from routers and IoT systems.
Fortinet lists the payload infrastructure IP as 91.92.40[.]118 and identifies the malware as Linux/Agent.BDS!tr; relevant IPS, web-filtering, reputation, and anti-botnet protections are available to FortiGuard customers.
IOCs
| Indicator type | Value |
|---|---|
| IP address | 91.92.40[.]118 |
| SHA-256 | f13cb360768363d3424e2192c7805b8c8015eb8706dbbbcdead6aed8cf390109 |
| SHA-256 | 4c0886349e9d348569fffe1b7a31e474d514508bf0cd6f1e5dd99c2a73525e4d |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
[Live Webinar] Join Elastic & UnderDefense to learn how small security teams can unify AI visibility and agentic response into one operating model. -> Register Now







