

A vulnerability with Linksys Smart Wi-Fi routers allows attackers to gain unauthenticated, remote access to the vulnerable router and to access sensitive information.
The vulnerability can be exploited by just knowing the public IP address of the router. It can be exploited simply by just opening the router public IP address in the web browser and from the developer console, move to network and JNAP queries.
By just opening the JNAP queries, the sensitive information will get exposed, and it can be reproduced by sending a request to JNAP endpoint.
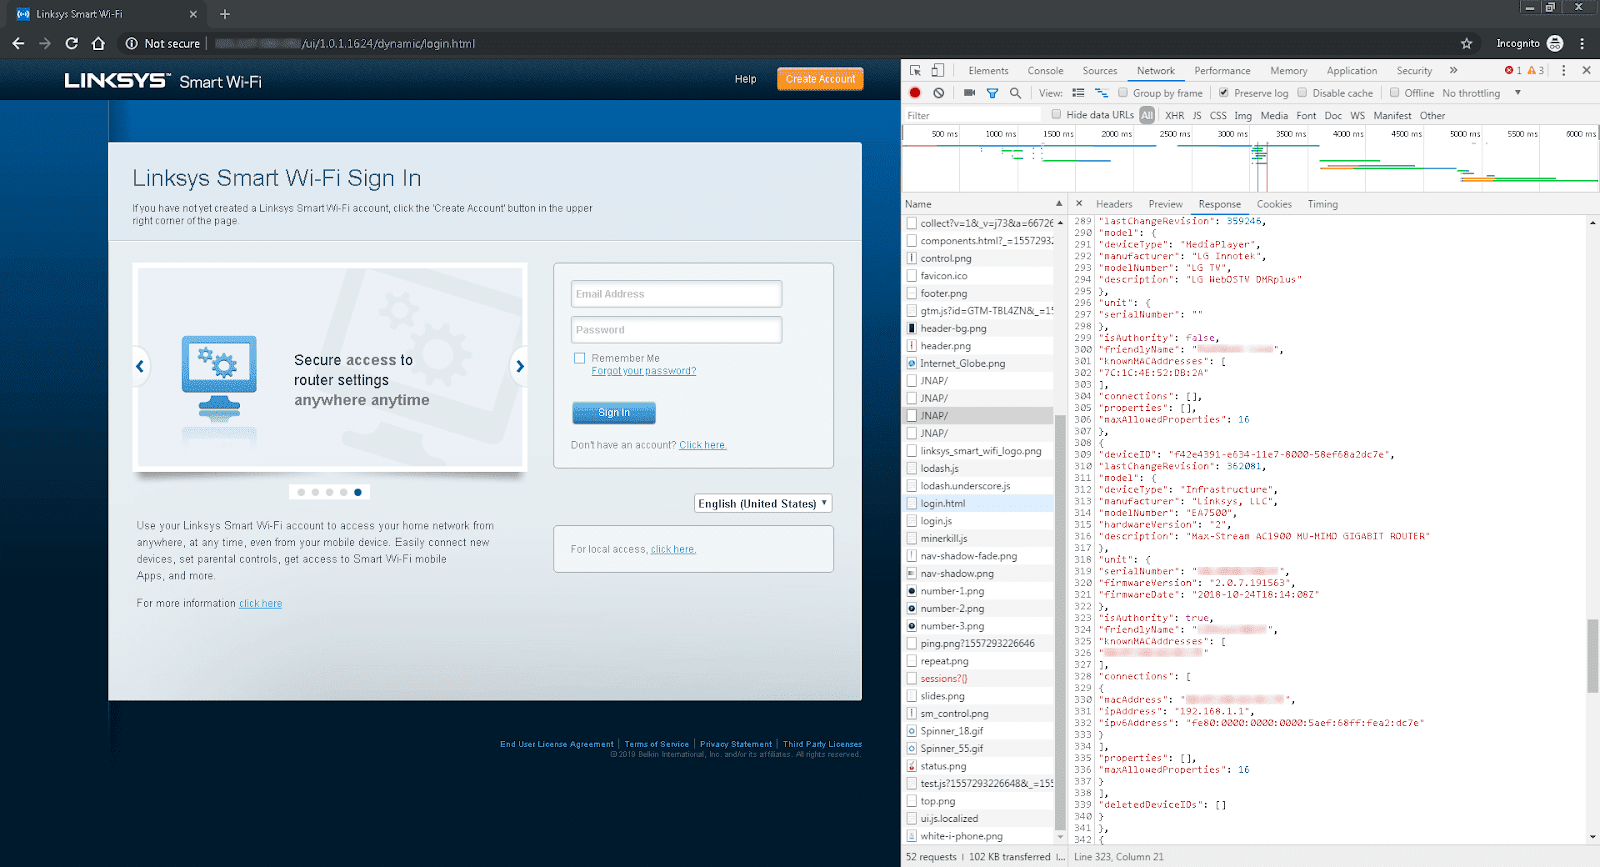
“This sensitive information disclosure vulnerability requires no authentication and can be exploited by a remote attacker with little technical knowledge,” reads BadPackets report.
Following are the sensitive information leak that includes
- MAC address of every device, including historical one
- Device name
- Operating System
In some cases, it includes device type, manufacturer, model number, and description. Other sensitive information such as settings, firewall status, firmware update settings, and DDNS settings are also leaked.
“According to researchers 25,617, Linksys Smart Wi-Fi routers are currently leaking sensitive information to the public internet.”
The leakage pose privacy concerns, by having the extracted details attackers gain access to the home or business networks to launch targeted attacks. Following are the devices affected.

756,565 MAC address was leaked Mursch said, most of the Linksys Smart Wi-Fi routers have not changed the default password, which allows an unauthenticated attacker to gain access to the router. The can also be done by merely querying the following JNAP endpoint.
“Our scans have found thousands of routers are still using the default password and are vulnerable to immediate takeover – if they aren’t already compromised,” Mursch added.
Bad Packet reproduced the issue that fixed before five years, “While CVE-2014-8244 was supposedly patched for this issue, our findings have indicated otherwise,” Mursch said.
Linksys security team determined the issue was “Not applicable /Won’t fix” and subsequently closed.
Related Read
Verizon Fios Router Vulnerabilities Allows Attackers to Gain Complete Control Over the Network
New DNS Hijacking Attack Exploiting DLink Routers to Target Netflix, PayPal, Uber, Gmail Users







