

Researchers discovered a new Linux malware called “EvilGnome” with previously unseen functionalities that capable of creating a backdoor and spying the Linux desktop users.
Based on the evidence and the operational similarities, the implant possibly distributed by Gamaredon Group, a Russian based threat group that has been active since at least 2013.
Gamaredon Group attack victims using a different form of malicious attachments, delivered via spear-phishing techniques and employed the information-stealing tools.
This malware impersonates the Gnome extension so that researchers from intezer named the implant EvilGnome which is completely undetected by all the major security software from leading vendors.

Since 70% web server market share occupied with Linux-based operating systems, Linux malware ecosystem is plagued by financial driven crypto-miners and DDoS botnet tools which mostly target vulnerable servers.
EvilGnome Infrastructure Similarities with Gamaredon
Gamaredon Group does not use any known Linux implants. EvilGnome employed the techniques and modules use of SFX, a deployment of information-stealing tools and persistence with task scheduler.
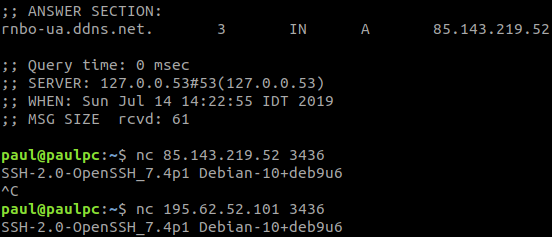
Researchers discovered that the threat actors who behind EvilGnome using a hosting provider which is used by Gamaredon Group for a year and they found a C2 server IP address that resolves 2 domains, gamework[.]ddns[.]net and workan[.]ddns[.]net.
Further investigation with C2 server reveals that it served SSH over port 3436. in which, a port open was identified that serving SSH, which means that both on EvilGnome C2 and Gamaredon’s rnbo-ua.ddns.net using the methods.
Infection Process
Initially, EvilGnome delivers a self-extracting archive shell script created with makeself, a small shell script that generates a self-extractable compressed tar archive from a directory.
There are 4 different files are identified with the archived,
- gnome-shell-ext – the spy agent executable
- gnome-shell-ext.sh – checks if gnome-shell-ext is already running and if not, executes it
- rtp.dat– configuration file for gnome-shell-ext
- setup.sh – the setup script that is run by makeself after unpacking
When analyzing the spy agent, researchers uncovered that the code was never seen before by the system and it was built in C++.
Researchers from Intezer digging deeper into spy agent and they find five new modules called “Shooters” which can perform different activities with respective commands.
ShooterSound – captures audio from the user’s microphone and uploads to C2
ShooterImage – captures screenshots and uploads to C2
ShooterFile – scans the file system for newly created files and uploads them to C2
ShooterPing – receives new commands from C2
ShooterKey – unimplemented and unused, most likely an unfinished keylogging module
“Researchers believe this is a premature test version. We anticipate newer versions to be discovered and reviewed in the future”
IOCs
EvilGnome:
a21acbe7ee77c721f1adc76e7a7799c936e74348d32b4c38f3bf6357ed7e803282b69954410c83315dfe769eed4b6cfc7d11f0f62e26ff546542e35dcd7106b7
7ffab36b2fa68d0708c82f01a70c8d10614ca742d838b69007f5104337a4b869
195.62.52[.]101
Gamaredon Group:
185.158.115[.]44
185.158.115[.]154
clsass.ddns[.]net
kotl[.]space
Related Read
Hackers Use Linux Malware HiddenWasp to Attack Linux Systems for Gaining Remote Access
New Linux Coin Miner that Deletes Other Linux Malware and Coin Miners







