

Researchers discovered nearly 85 malicious adware apps in Google play store that intended to upload for delivering adware and monetize from affected Android devices.
These Fraudulent adware apps were installed over 8 million times from the Google play store, and the malicious ads displaying in the affected phone are very difficult to close.
Past two-years adware is playing a vital role in cybercrime to cost businesses huge financial losses, and it also targets the millions of individual Android users.
These malicious app developers are employing a unique and sophisticated technique to evade the detection based on user behaviors.
Researchers discovered these 85 adware apps mostly under photography and gaming apps since these categories are very attractive for Android users.
Adware Infection Process
In order to monitor user behavior and presence, the app is recording the 2 ( “installTime”, “network time” ) different timestamps by abusing a publicly available and legitimate RESTful API.
Soon after it registers an Android component known as Broadcast Receiver that helps to monitor the user behavior after a device is woken up.
Every time the user unlocks the phone, adware keeps on performing the several checks by comparing the current time with a timestamp.
After 30 minutes from the installation, the adware app icon and create a shortcut on the device’s home screen without making any different and unusual appearance.
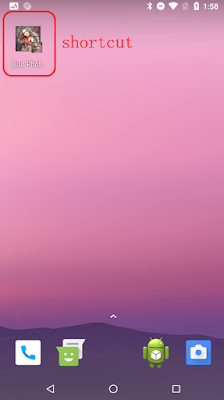
Attackers using this kindly of a method for their malicious app from being uninstalled by dragging and dropping its icon to the Uninstall section of the screen.
Displaying The Ads
Adware app registers another broadcast receiver to check if the victims unlocked the mobile. The advertisements will be displayed on the screen once it confirmed that the device is unlocked.
According to Trend Micro research, It also uses installTime and networkInstallTime to identify how long it has been installed on the device. Apart from that, it also checks the last advertisement to make sure that it doesn’t show the same ad too frequently.
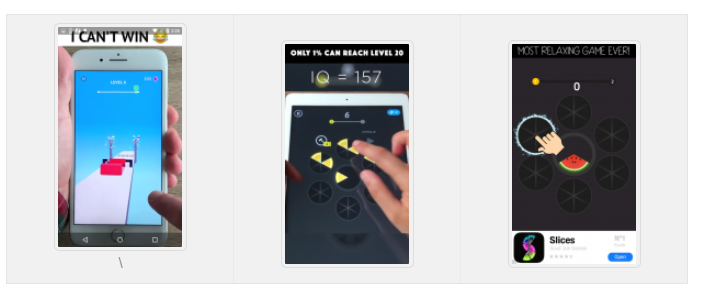
Ads are shown in the full screen of the mobile and forcefully view the whole duration of the ad before being able to close it and prevent to go back to access other application until the ad gets automatically closed.
All the malicious adware apps are reported to Google, and the adware-embedded apps are no longer on the Play store.
You can check here the Top 5 Best Adware Removal Tool to Block Annoying Ads in your mobile and computer.
Sponsored: – Manage all the Endpoint networks from a single Console.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity updates also you can take the Best Cybersecurity course online to keep yourself updated.







