

3 Indonesia Hackers has been arrested by the Interpol under coordinated cyber operation for hacking hundreds of E-commerce websites using JS-Sniffer Malware.
ANF (27), K (35), and N (23) who have resided in Indonesia and running the malicious campaign, and targeting the E-Commerce websites with the malware known as JavaScript-sniffer.
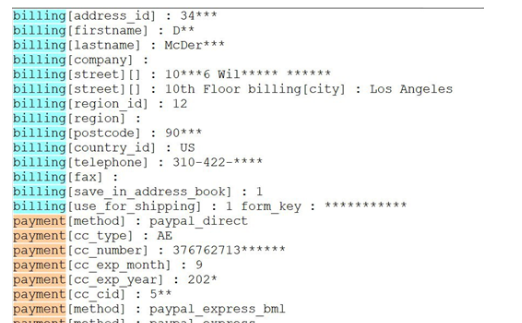
Malware authors developed with JavaScript-sniffer to attack specifically an E-Commerce website to steals the customers’ payment card details, and personal data such as names, addresses, and phone numbers, sending the information to Command and Control (C2) servers controlled by the cybercriminals.
JavaScript-sniffer initially detected in 2018, was used by the unknown cybercrime group to infect the Magento-based websites, also there was a shred of evidence collected by the Group-IB that said the attackers are used password-stealing malware and tried to infect online merchants in order to infect their websites with the JS-sniffer.
During that time, infect nearly 200 websites in Indonesia, Australia, Europe, the United States, South America, and some other countries.
These malware operators are infecting E-commerce websites from Indonesia, they were arrested with the help of the Indonesian Cyber Police and other five ASEAN countries which have shared the intelligence data to the Interpol.
Cybersecurity Firm Group-IB from Singapore has supported this investigation with digital forensics expertise helping to identify the suspects.
“The suspects have managed to infect hundreds of e-commerce websites in various locations, including in Indonesia, Australia, the United Kingdom, the United States, Germany, Brazil, and some other countries. Payment and personal data of thousands of online shoppers from Asia, Europe, and the Americas have been stolen.”Group-IB told GBHackers on Security via Email.
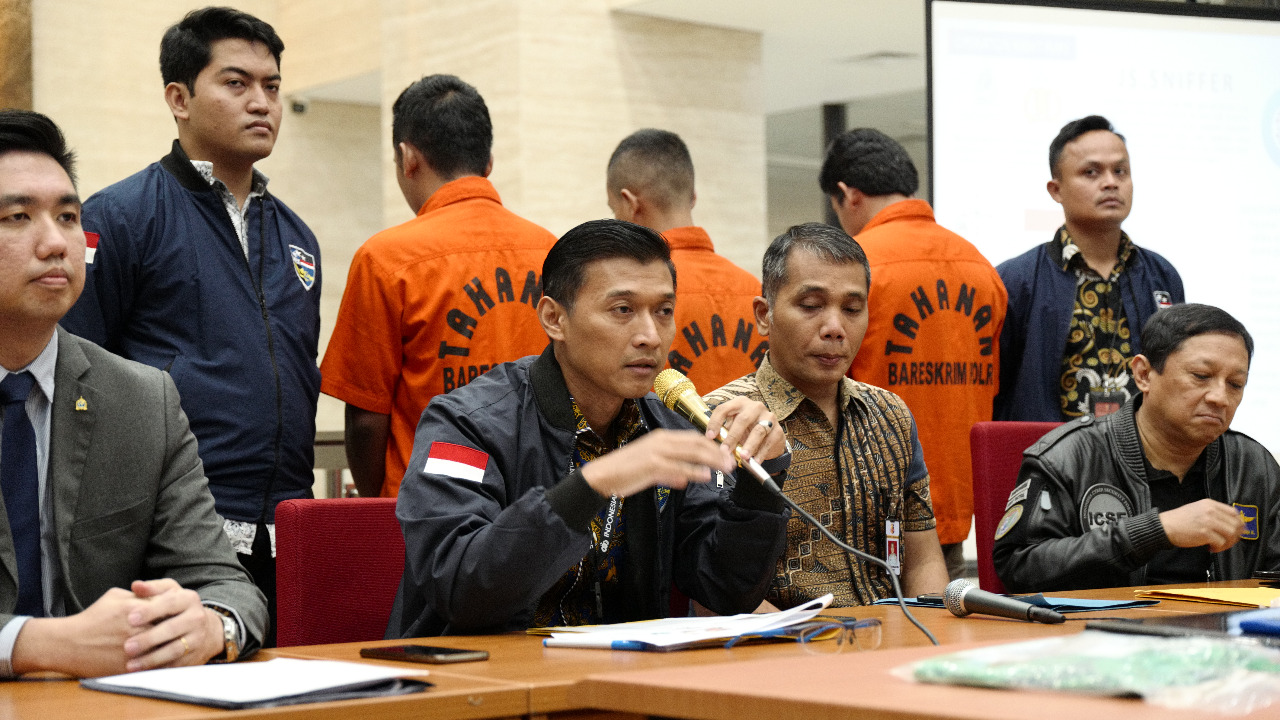
Arrest & Secenteses
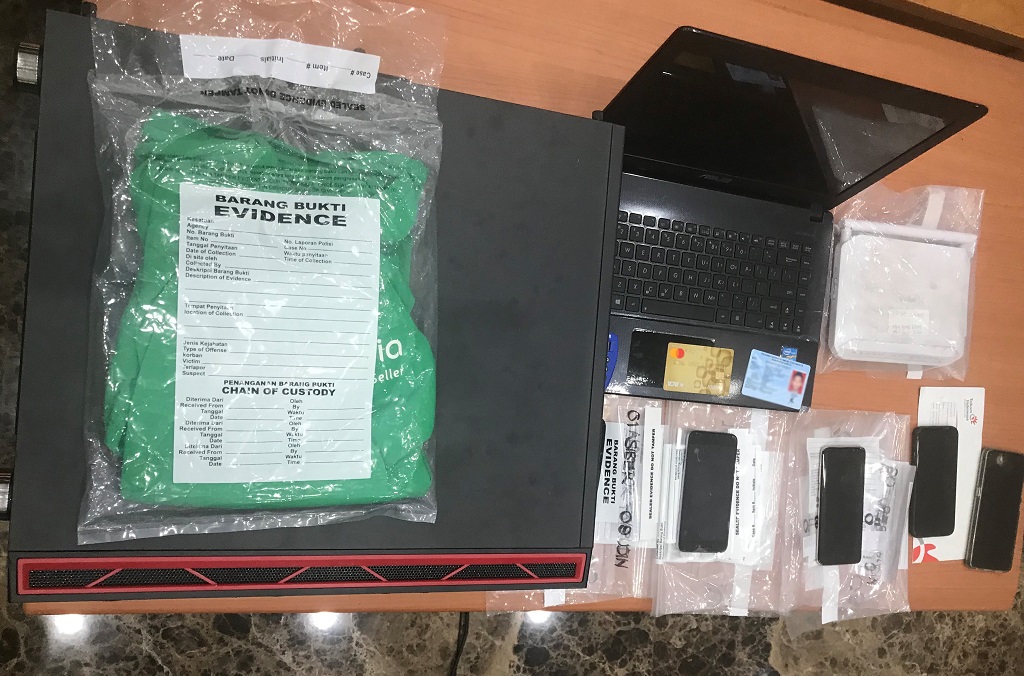
All 3 hackers were arrested in December from different regions in Indonesia and the Indonesian Cyber Police seized laptops, mobile phones of various brands, CPU units, IDs, BCA Token, ATM cards during the investigation.
According to the Indonesian criminal code, suspected operators of the GetBilling JavaScript-sniffer family are charged with the theft of electronic data, which carries up to a 10-year jail sentence.
INTERPOL’s Director of Cybercrime Craig Jones said, “Strong and effective partnerships between police and the cybersecurity industry are essential to ensure law enforcement worldwide has access to the information they need to address the scale and complexity of today’s cyberthreat landscape”
The investigation reveals that the malware derived the GetBilling family and, is used by these Indonesian Hackers to steal the various sensitive information and use it to buy goods, such as electronic devices or other luxury items and reselling it in the Indonesia market at a lower price.
“The size of the carding market, in turn, grew by 33 percent and amounted to USD 879.7 million. The sale of CVV data is also on the rise today, having increased by 19 percent in the corresponding period, and one of the key reasons behind this trend could be JavaScript-sniffers.” Group-IB told GBHackers.
The number of compromised cards uploaded to underground forums increased from 27.1 million to 43.8 million in H2 2108-H1 2019 year-on-year.
GBHackers learned that the authorities took down the Command and control servers used by these criminals to collect the data from the victims.
Also Read:
18 International Hackers who Steal Tens of Millions of Dollars Arrested For ATM Skimming Attack







