

Recently, the cybersecurity firm ESET has discovered a malware toolkit, which has been named as Ramsay, a rare malware attack with the advanced capabilities that are rare nowadays.
Ramsay is created with features to attack air-gapped computers, assemble Word and other delicate documents in a sealed storage container.
After that, the attacker simply waits for a possible opportunity to steal sensitive documents from the infected network.
Ramsay is critical because it’s one of the rarest malware attacks that has happened recently.
Thus ESET stated that this malware is mainly developed to space up the air gap and reach all the isolated networks.
Ramsay Malware Attack vectors
Moreover, Ramsay has a total of three different versions with different functions.
The very first one was organized in September 2019 (Ramsay v1), and then the second one complies in early and late March 2020 (Ramsay v2.a and v2.b).
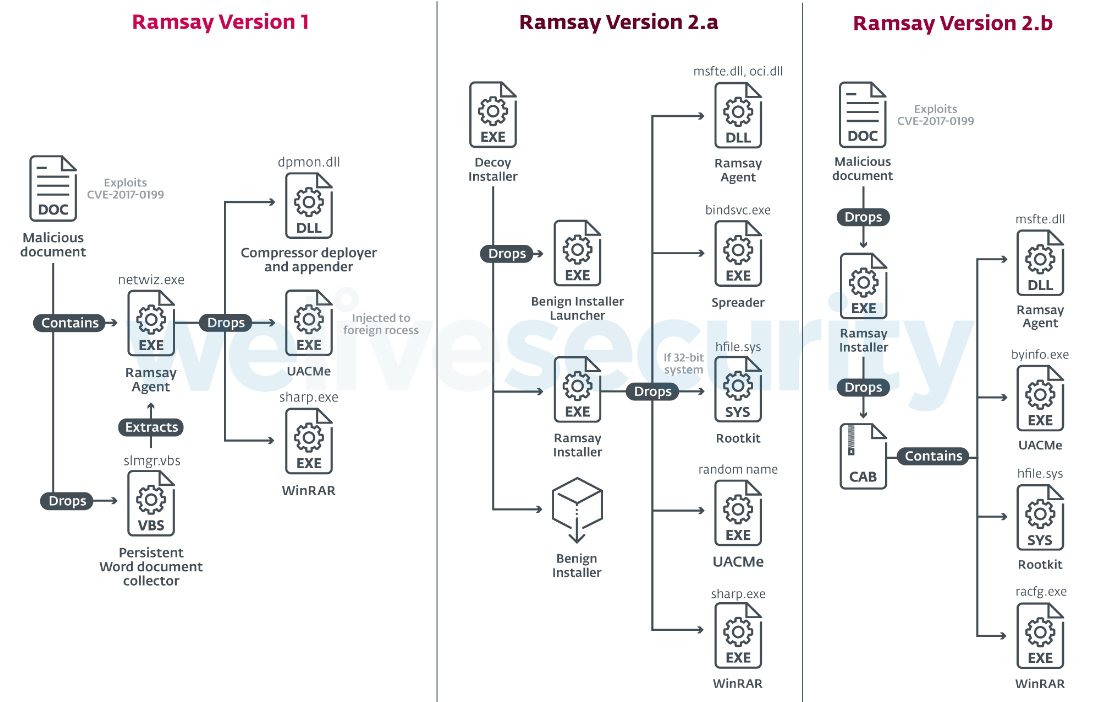
Malicious documents dropping Ramsay version 1
In this attack vector, the attacker uses the malicious documents exploiting CVE-2017-0199 through which they deliver a Visual Basic Script, “OfficeTemporary.sct.” This script then extracts within the document’s body, and then by having a base64-encoded PE under a JPG header, it pretends itself to be a typical JPG image to fool the victim.
Decoy installer dropping Ramsay version 2.a
Along with the debut of new features like Spreader component and a rootkit, this version of Ramsay, “Ramsay version 2.a,” clearly shows its deception and persistence tactics.
Malicious documents dropping Ramsay version 2.b
Just like the Ramsay version 1, in this attack vector also, the attacker uses the malicious documents but exploiting CVE-2017-11882. Through this exploit, the attackers drop “lmsch.exe,” a Ramsay Installer. In short, the Ramsay version 2.b is a slightly modified version of Ramsay version 2.a.
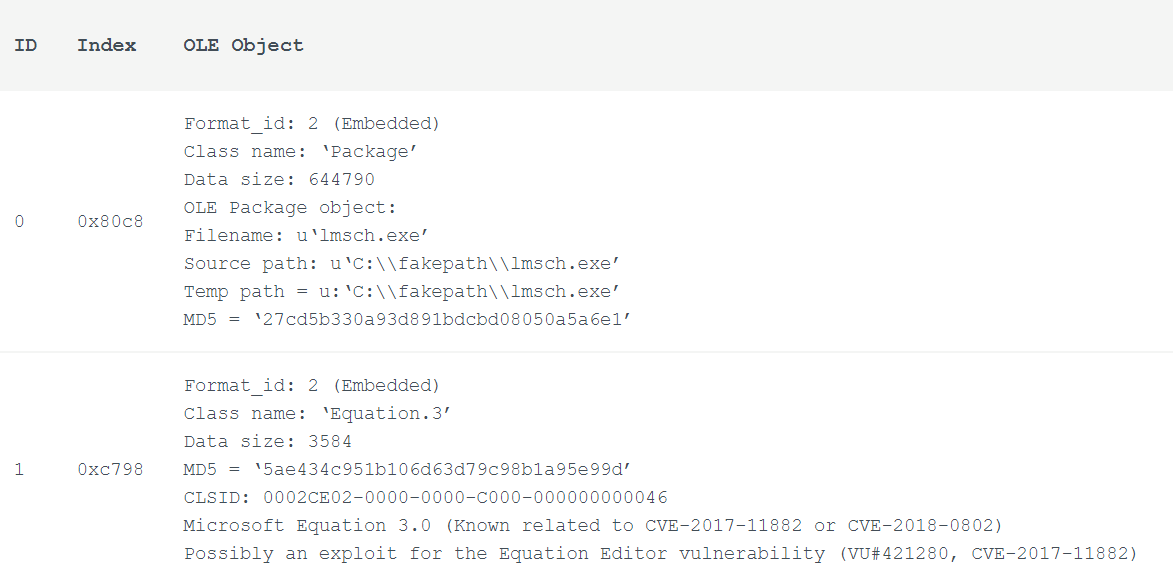
Well, all its versions are created along with the spreader module that added models of the Ramsay malware to each PE (portable executable) files that are found on portable drives and network shares.
Thus ESET said that they were so confused at first at it is quite rare and was challenging to identify it.
Most importantly, this malware is operating to jump the air gap and reach isolated networks, as we said above.
In contrast, the users would most probably move the infected executables between the company’s various network layers and ultimately end up on a remote system.
Capabilities
Well, if we talk about the capabilities of Ramsay, then it is a very highly versatile mechanism. Thus, it implements several persistent methods like command execution, file collection, communication protocol, spreading, and many more.
But Ramsay has many similarities with Retro, as both malware uses the same encoding algorithm, yet till now, it’s not clear that who is actually behind this malware attack.
Apart from this, the security researcher at ESET has also noticed Korean language metadata within the malicious documents.
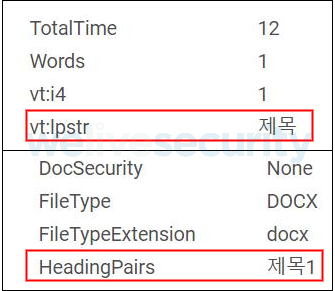
Since the Ramsay malware is similar to Retro, that’s why the security researcher at ESET, Ignacio Sanmillan believes that it must also be operated with the interests of the South Korean government as the Retro malware strain was developed by the DarkHotel group, which was also performed with the attention of the South Korean government.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity, and hacking news updates.







