Friday, October 2, 2026

New PLAYFULGHOST Malware Hacking Devices To Remotely Capture Audio Recordings

PLAYFULGHOST, a Gh0st RAT variant, leverages distinct traffic patterns and encryption, which spread via phishing emails and SEO poisoning of bundled applications, enabling keylogging, screen capture, and other malicious remote access capabilities.

A phishing campaign employed a .jpg file as a lure to deliver a malicious RAR archive. Upon extraction and execution, the archive released a Windows executable, which subsequently downloaded and executed the malware known as PLAYFULGHOST from a remote server.

lure text related to “code of conduct” used for phishing

The SEO poisoning campaign involves a malicious installer disguised as legitimate software, which, upon execution, downloads and installs additional malicious components, including PLAYFULGHOST, from a remote server.

The malicious process downloads PLAYFULGHOST components, as a vulnerable executable loads a malicious DLL, which decrypts and loads the PLAYFULGHOST payload into memory, exploiting DLL search order hijacking.
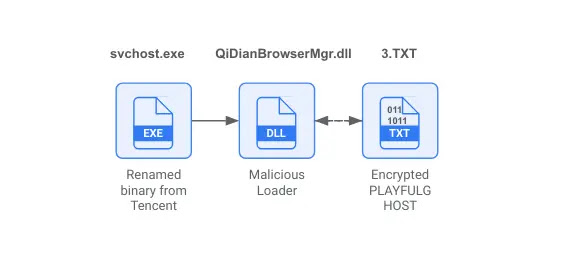
 Renamed Tencent binary loads malicious DLL to launch PLAYFULGHOST
 Renamed Tencent binary loads malicious DLL to launch PLAYFULGHOST

Researchers observed two PLAYFULGHOST malware execution scenarios, as in scenario 1, a renamed Tencent svchost.exe loaded a malicious DLL named QiDianBrowserMgr.dll, which delivered a 3.TXT payload, while in scenario 2, a renamed curl.exe (TIM.exe) loaded libcurl.dll to deliver a Debug.log payload.

PLAYFULGHOST alongside BOOSTWAVE, a shellcode dropper, TERMINATOR, a tool to terminate security software, QAssist.sys, a rootkit to hide malicious activity, and CHROMEUSERINFO.dll was found, indicating an intent to steal Google Chrome credentials. 

According to Mandiat researchers, with the help of these tools, the adversary is able to demonstrate their focus on evading detection, maintaining persistence, and data exfiltration.

 Process tree for malicious installer activity
 Process tree for malicious installer activity

It persists on the system by leveraging a combination of mechanisms, including registry key entries, scheduled tasks, the startup folder, and also may utilize a Windows Service for robust background operations.

PLAYFULGHOST is a sophisticated malware capable of remote system control, including data exfiltration (keylogging, screenshots, audio), file manipulation, remote execution (shell, RDP), privilege escalation, and anti-forensic techniques. 

Investigate Real-World Malicious Links, Malware & Phishing Attacks With ANY.RUN – Try for Free

Aman Mishra
Aman Mishra
Aman Mishra is a Security and privacy Reporter covering various data breach, cyber crime, malware, & vulnerability.

Hot this week

How To Access Dark Web Anonymously and know its Secretive and Mysterious Activities

What is Deep Web The deep web, invisible web, or...

How to Build and Run a Security Operations Center (SOC Guide) – 2023

Today’s Cyber security operations center (CSOC) should have everything...

Russian Hackers Bypass EDR to Deliver a Weaponized TeamViewer Component

TeamViewer's popularity and remote access capabilities make it an...

Web Server Penetration Testing Checklist – 2026

Web server pentesting is performed under three significant categories: identity,...

ATM Penetration Testing – Advanced Testing Methods to Find The Vulnerabilities

ATM Penetration testing, Hackers have found different approaches to...

Sony PS5 Relapse Jailbreak Exploit Uses JSC Memory Corruption and Kernel UAF

A newly released PlayStation 5 jailbreak chain, called Relapse,...

Zammad Vulnerabilities Let Attackers Execute Code and Escalate Privileges to Root

Two critical vulnerabilities in the open-source Zammad helpdesk and...

Safari History Database Tags Can Reveal Users’ Browsing Themes in Forensic Investigations

Safari's History database contains a lesser-known tagging artifact that...

Exposed Hacker Server Reveals Toolkit Used in Viva Aerobus-Linked Intrusion

A publicly exposed attacker staging server has provided a...

Multiple cPanel & WHM Vulnerabilities Enable Root Code Execution and Admin Session Hijacking

cPanel has released security updates to address three vulnerabilities...

Capacitor Vulnerability Lets Remote Content Run With Full App Origin Trust

A critical vulnerability in Capacitor, identified as CVE-2026-103922, could...

OpenAI Blocks 15,000 Requests Trying to Extract Protected Model Reasoning

OpenAI has disrupted a coordinated campaign to extract protected...

Related Articles

Recent News