Sunday, October 18, 2026

Beware of New Mac Malware Spreading via Poisoned Google Search Results

Security researchers discovered a new Mac malware Shlayer spreading through Google poisoned search results. The malware distributed masqueraded as a fake Adobe Flash Player installer (.DMG disk image).

The malware installer and its payload had a 0/60 detection rate among all antivirus engines on VirusTotal.

Mac Malware Shlayer

Intego researchers observed this newly updated Shlayer malware delivered as a Trojan horse file (.DMG disk image) masqueraded as an Adobe Flash Player.

Once the user installs the malicious Flash Player on Mac machine the image will get the mount and display instructions on how to install it.

“The instructions tell users to first “right-click” on the flash installer and select Open, and then to click Open in the resulting dialog box,” reads Intego blog post.
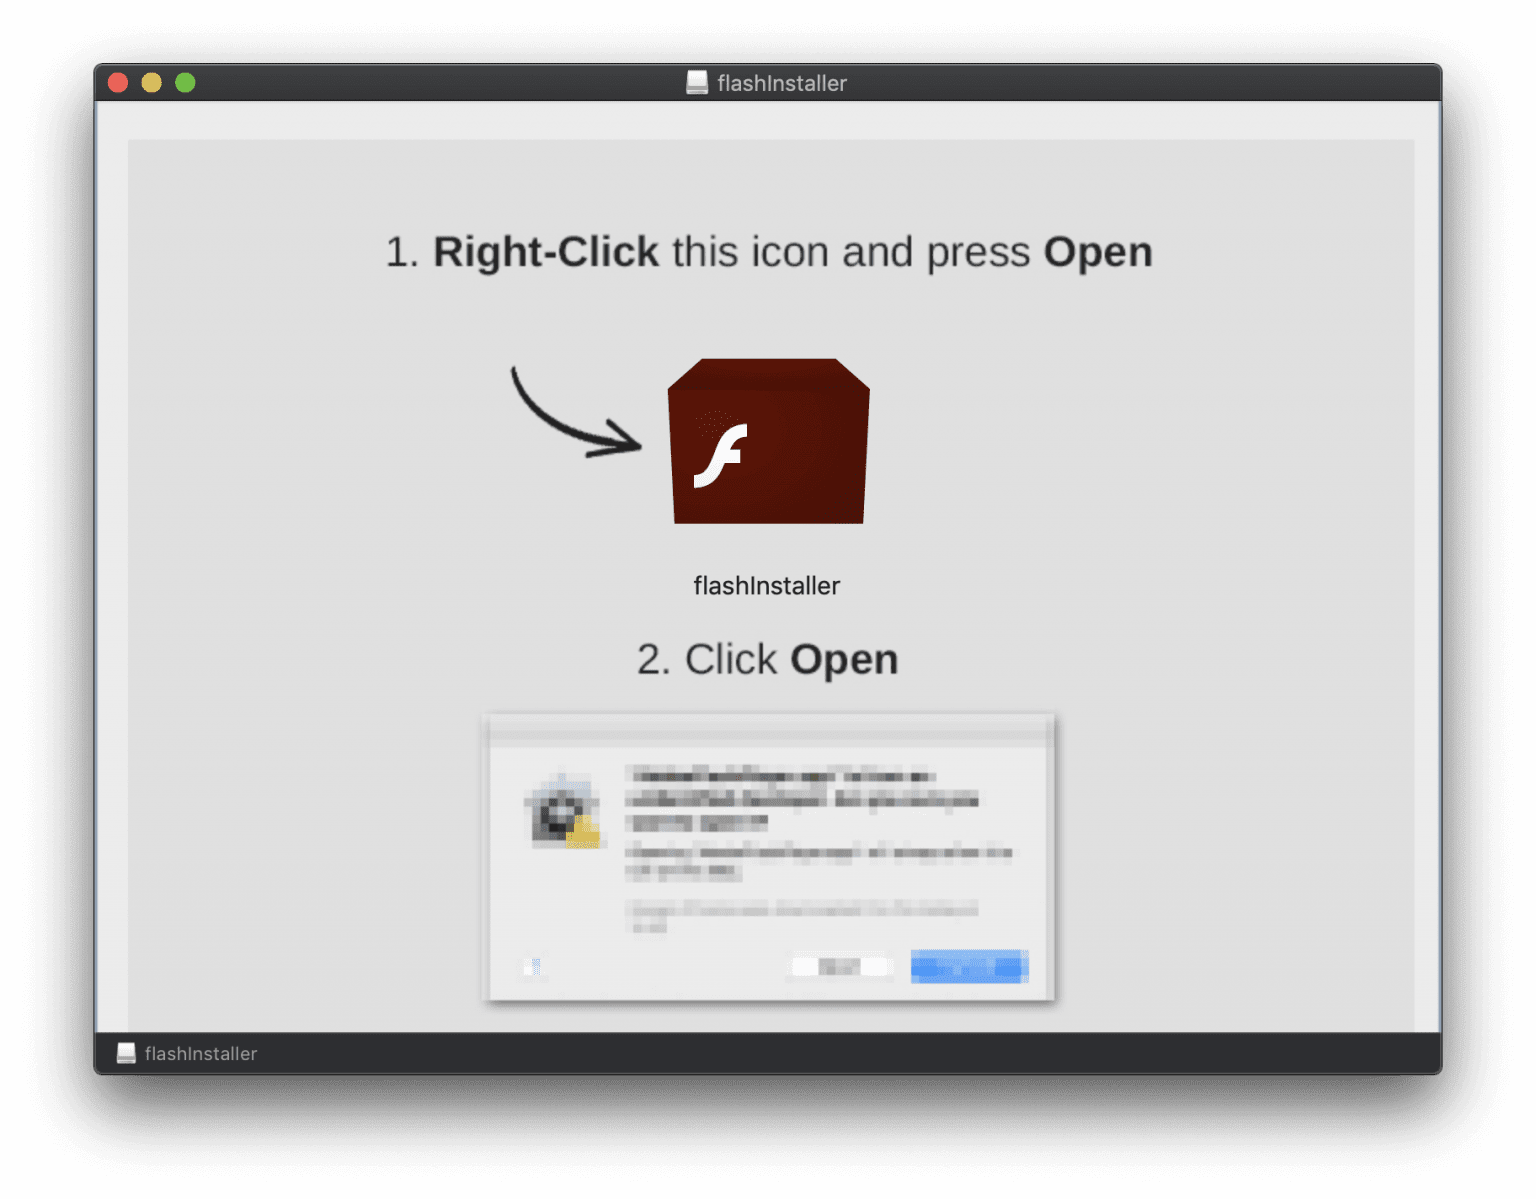
When the user starts following the instruction to installing the malicious application, the icon looks like a Flash player, but in the background, the bash shell script executed the opening terminal.

The bash script extracts password-protected .zip archive file which has a malicious app bundle, it stores the malicious app into a hidden temporary folder.

The malicious app also downloads the legitimate, Adobe-signed Flash Player installer to trick the user, but the hidden Mac app downloads malicious apps.

“The developers’ decision to hide the Mac .app within a password-protected .zip file, and to hide that within a bash shell script, is a novel idea—and it is also extremely clear evidence that the developers are trying to evade detection by antivirus software.”

“This newly re-engineered malware purports to be a legitimate Flash Player installer, but it can surreptitiously download and install additional unwanted packages containing adware or spyware.”

Shlayer malware believed to be the most widespread macOS threat, earlier this February Carbon Black researchers spotted new Shlayer malware targeting 10.10.5 up to 10.14.3.

Adobe already announced that they will stop distributing and updating Flash Player after 31 December 2020 (“EOL Date”).

You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.

Also Read

Blue Mockingbird Hacker Group Attack Windows Machines at Multiple Organizations to Deploy cryptocurrency-mining Malware

Does Your Mac Need Antivirus Protection? Here’s What You Need to Know

Gurubaran
Gurubaran
Gurubaran is a co-founder of Cyber Security News and GBHackers On Security. He has 10+ years of experience as a Security Consultant, Editor, and Analyst in cybersecurity, technology, and communications.

Hot this week

How To Access Dark Web Anonymously and know its Secretive and Mysterious Activities

What is Deep Web The deep web, invisible web, or...

How to Build and Run a Security Operations Center (SOC Guide) – 2023

Today’s Cyber security operations center (CSOC) should have everything...

Russian Hackers Bypass EDR to Deliver a Weaponized TeamViewer Component

TeamViewer's popularity and remote access capabilities make it an...

Web Server Penetration Testing Checklist – 2026

Web server pentesting is performed under three significant categories: identity,...

ATM Penetration Testing – Advanced Testing Methods to Find The Vulnerabilities

ATM Penetration testing, Hackers have found different approaches to...

Hackers Use ConnectWise SkyKick Credentials to Access Microsoft 365, Halting Cloud Backups

Attackers abused compromised ConnectWise Cloud Backup credentials to access...

Anthropic’s Claude AI Uncovers Origins of NSA-Provided Cryptographic Keys After 25 Years

Anthropic says an internal Claude research model reconstructed how...

OpenBSD Kernel Flaw Dating Back 37 Years Enables Local Privilege Escalation to Root

A newly disclosed OpenBSD kernel exploitation chain combines a...

GhostAction Hackers Hide Credential-Stealing Malware in Fake Font Files Across 94 GitHub Repositories

GhostAction attackers have expanded their GitHub credential theft campaign...

SideCopy Hackers Target Indian Organizations With ReverseRAT Malware to Steal Data

Indian authorities have warned that SideCopy hackers are targeting...

New GhostBat Android Malware Targets 60 Banking and UPI Apps to Steal PINs

A new GhostBat RAT variant targets 60 Android financial...

New ROMULUS Malware Platform Uses Six Servers to Deliver Multiple Malicious Payloads

ROMULUS, a shared ClickFix delivery platform operating across six...

Related Articles

Recent News


