

Recently, Samsung has rolled out security updates for its mobile devices to fix some critical security vulnerabilities. In September, Samsung has published the official changelog mentioning many of the vulnerabilities of all the latest over-the-air.
This security update has many vulnerability patches that fix all sought of critical vulnerabilities in many version of Android operating systems. However, the security update that the company has already released covers its Exynos-powered international Galaxy Note 9 model (SM-N960F) with the September 2020 patch.
While the OTA states that the security patch level of cooperative Galaxy devices is up to September 1st, 2020, it involves 15 security fixes, particularly to Samsung’s devices.
And on the other side, Samsung’s sustaining update joins Google’s patches with those particular to smartphones and tablets, of its customized variant of the OS.
According to the reports, the update that has been launched also implies that the first fix is Samsung’s fixes for a 5G-specific vulnerability. This vulnerability reworks in the manner in which USB debugging instructions concerning LTE and 5G commands can be used without the user’s permission.
Most Affecting Vulnerabilities
Among all the vulnerabilities, the most affecting vulnerability was CVE-2020-0240, it’s a remote code execution vulnerability produced by an “integer overflow” bug in the Android operating system. According to the researchers, this vulnerability would enable a remote attacker to gain full authority over your device.
There are some other vulnerabilities, too, that cover those which enable you to bypass user communication to obtain aerial permission. This vulnerability would allow an attacker to manage code at higher authorities, then it usually would.
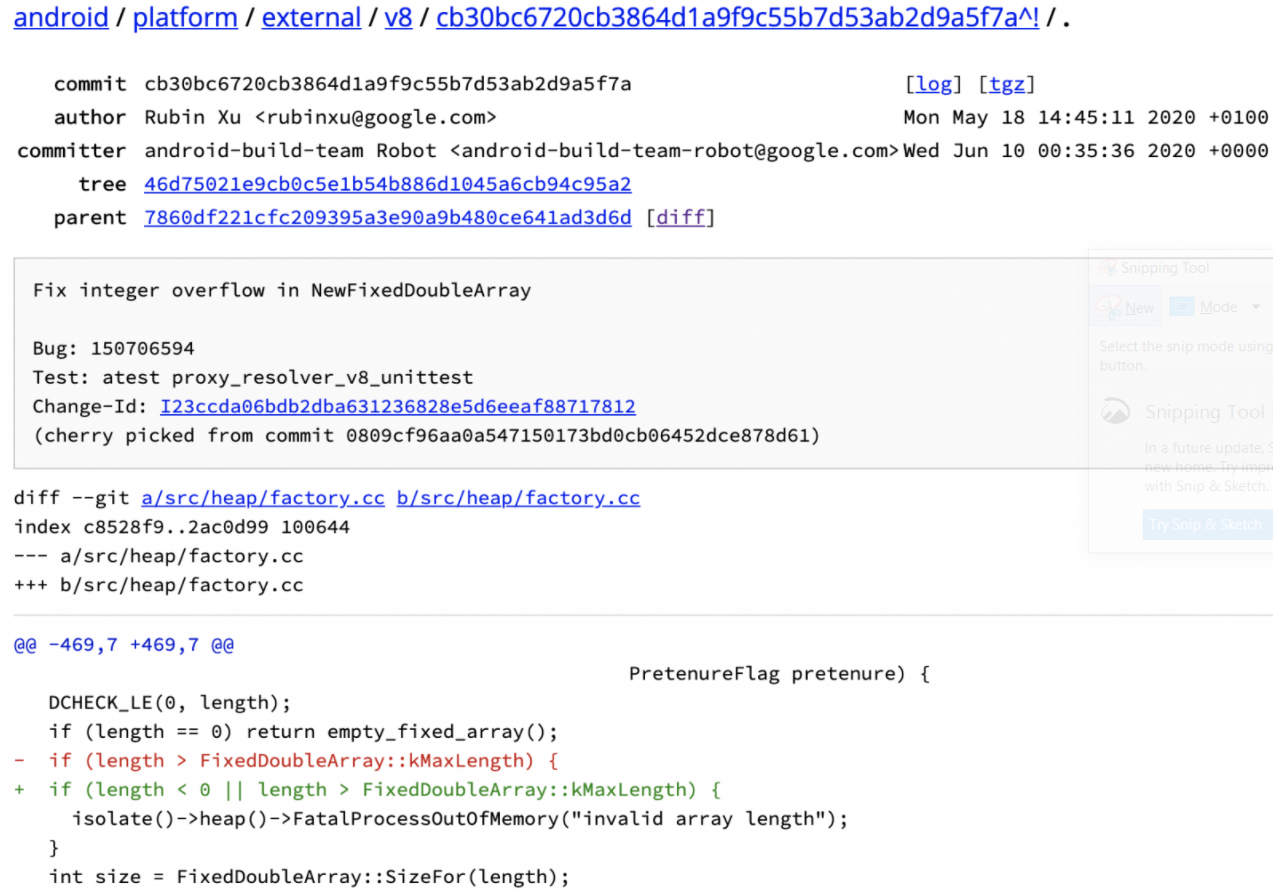
However, in the case of exploitation, the most critical vulnerability in this segment could easily allow a confined malicious application to bypass user communication demands to obtain access to additional authorities.
Other Vulnerabilities are Fixed in This Update
Framework
| CVE | Type | Severity | Updated AOSP versions |
| CVE-2020-0240 | RCE | High | 10 |
| CVE-2020-0238 | EoP | High | 8.0, 8.1, 9, 10 |
| CVE-2020-0257 | EoP | High | 10 |
| CVE-2020-0239 | ID | High | 9, 10 |
| CVE-2020-0249 | ID | High | 8.0, 8.1, 9, 10 |
| CVE-2020-0258 | ID | High | 10 |
| CVE-2020-0247 | DoS | High | 8.0, 8.1, 10 |
Media Framework
| CVE | Type | Severity | Updated AOSP versions |
| CVE-2020-0241 | EoP | High | 8.0, 8.1, 9, 10 |
| CVE-2020-0242 | EoP | High | 8.0, 8.1, 9, 10 |
| CVE-2020-0243 | EoP | High | 8.0, 8.1, 9, 10 |
System
| CVE | Type | Severity | Updated AOSP versions |
| CVE-2020-0108 | EoP | High | 8.1, 9, 10 |
| CVE-2020-0256 | EoP | High | 8.0, 8.1, 9, 10 |
| CVE-2020-0248 | ID | High | 10 |
| CVE-2020-0250 | ID | High | 10 |
Bugs May Still be Exploitable
In the case of Samsun Galaxy devices, the updates started this week, and it has its latest “security patch level” recorded “2020-08-01.” This indicates that the high severity Escalation of Privileges (EoP) vulnerabilities to be determined by the “2020-08-05 security patch” are yet exploitable.
In the case of CVE-2020-0259, this vulnerability can enable a locally present attacker to perform the arbitrary code execution on an unpatched device by increasing all the privileges.
But, the experts have advised all the users to update their Android devices instantly, so that they can safeguard themselves against these bugs and secure their devices fully, and also recommended users to make sure that the “auto-update” settings have been enabled.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity updates
Also Read:
BLURtooth – A new Vulnerability Let Attackers to Overwrite the Authentication Keys







