

The security researchers at Proofpoint have uncovered that the Iranian Hacking group, TA456 which is also known as “Tortoiseshell” and “Imperial Kitten” has recently executed several targeted attacks on defense contractors with malware.
On Facebook, the hackers of this group mimicked themselves as aerobics instructors simply to fool the defense contractors and then compromise their systems to exfiltrate sensitive data.
Here during the ongoing cyber espionage, the hackers mainly targeted the employees of the contractor companies working in the US aerospace defense; especially those who are involved in the operations in the Middle East.
In 2019 the hackers created a Facebook and Instagram profile of “Marcella Flores” and by exploiting this fake profile the hackers mimicked as an aerobics instructor.
Marcella Flores is none other than an imaginary character that is used by the hackers for their illicit activities.
Here at this stage the threat actors took their time and spent months establishing contact with their targets, correspondence with them by mail and in private messages, before moving on to attempts to infiltrate malware.
Malware and Campaign
The cybersecurity experts at Proofpoint have reported & dubbed the malware as, “Lempo,” it’s the updated version of the “Liderc.” Lempo is basically a VBS (Visual Basic Script) that is dropped by an Excel macro.
This VBS identifies the host in several ways by exploiting the built-in Windows commands, and then by using Microsoft’s CDO (Collaboration Data Objects) it exfiltrates the data.
Apart from this, the threat actors who created and abused the fake profile has also used the following things to trick their victims and make them believe they are real:-
- Private messages
- Social Media Profiles
- Photographs
- Flirty personal messages
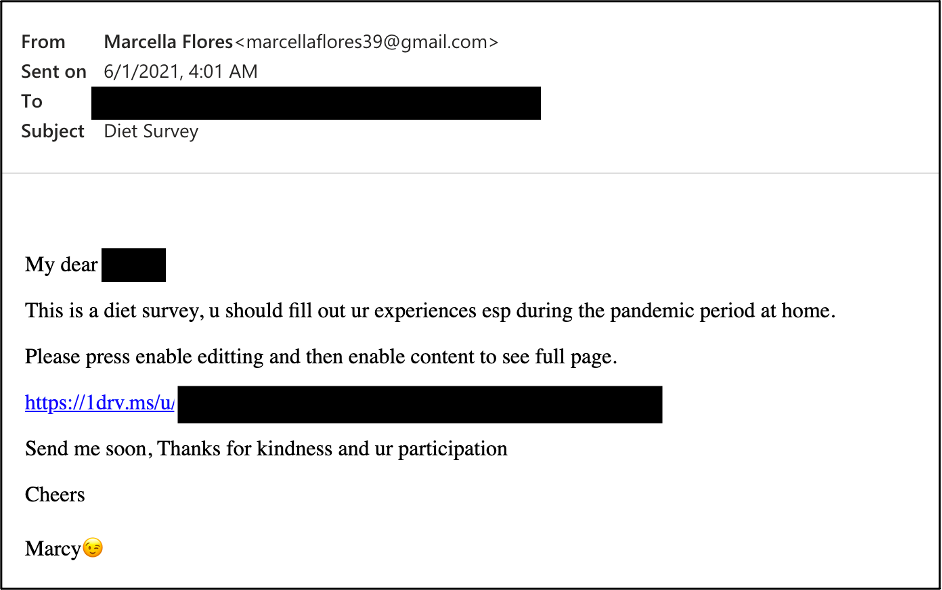
While as part of their espionage operation the hackers have also used those emails to send their victims links to OneDrive which led them to with a document with a survey related to diet, or a video file, as part of their long-standing correspondence.
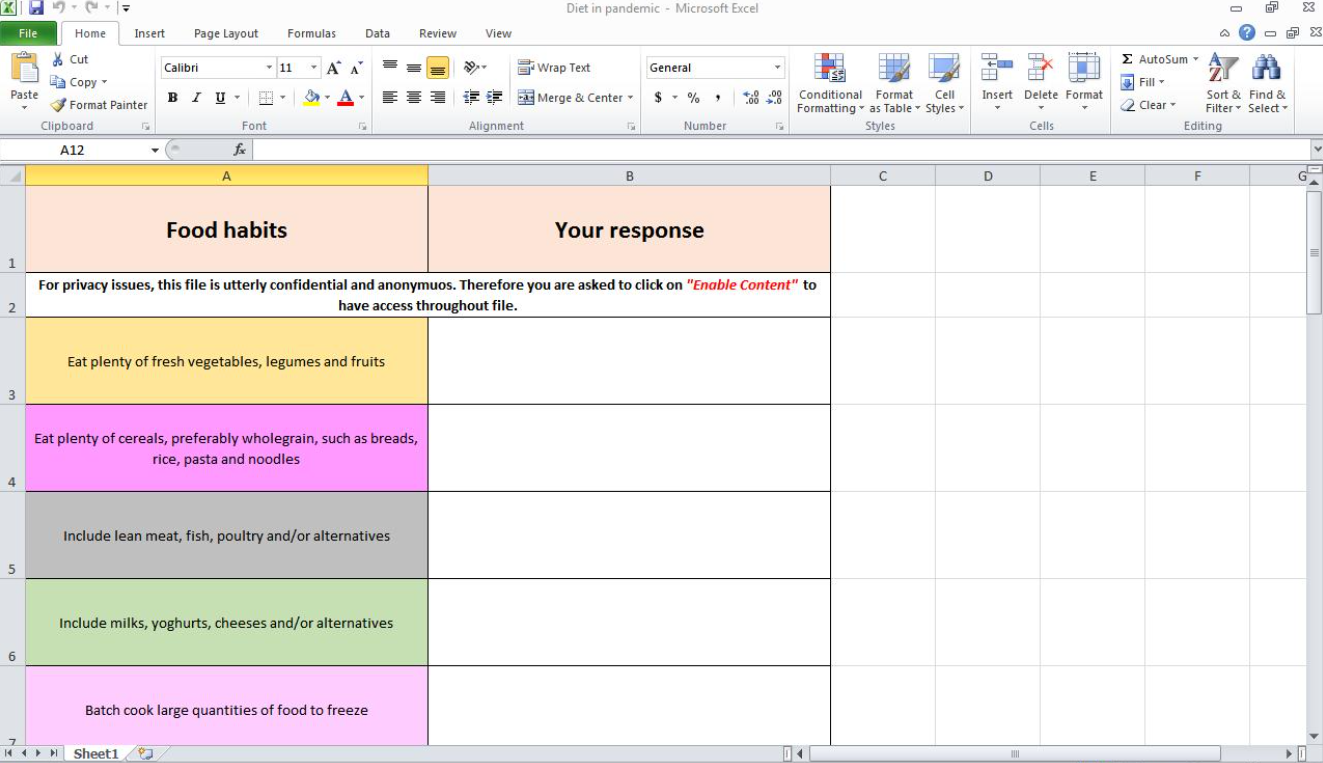
Information and records collected by Lempo
- Date and time
- Computer and usernames
- System information via WMIC os, sysaccount, environment, and computer system commands
- Antivirus products located in the “SecurityCenter2” path
- Drives
- Tasklist
- Software and version
- Net users and user details
Moreover, on the victim’s Windows computer the malware provides endurance to attackers which enables them to search and steal all the confidential data present on the compromised system. Through which easily an attacker can execute sophisticated spy campaigns.
However, at this moment the fake profile with the name, “Marcella Flores” was deactivated by the threat actors. According to the reports, in this spy campaign, the hackers of this group targeted more than 200 military defense, and aerospace companies in the US, UK, and Europe.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.







