

Threat actors associated with BazarLoader, TrickBot, and IcedID have increasingly co-opted the malware loader Bumblebee.
It has been discovered that hackers are using it to penetrate target networks for the purpose of post-exploitation activities as part of their campaigns to breach target networks.
Meroujan Antonyan and Alon Laufer, the researchers from Cybereason, explained the situation in the following manner:-
“An intensive amount of reconnaissance is conducted by the operators of Bumblebee. Moreover, even after executing a command, they redirect the output of that command to files so that it can be exfiltrated.”
Technical Analysis
Users typically launch Bumblebee infections by executing LNK files that load the malware using the system binary.
Phishing emails with malicious attachments or links to malicious archives containing Bumblebee malware are used to distribute the malware.

During the month of March 2022, Google’s TAG discovered for the first time what Bumblebee was doing on the internet. By unmasking Exotic Lily, the brokers that belong to the larger Conti collective as well as TrickBot, they were able to accomplish this feat.
An embedded command is present in this LNK file that runs Bumblebee DLL using the following files:-
- odbcconf.exe
- Living Off the Land Binary (LOLBin)
- .rsp
While the reference to the Bumblebee DLL can be found in the .rsp file.
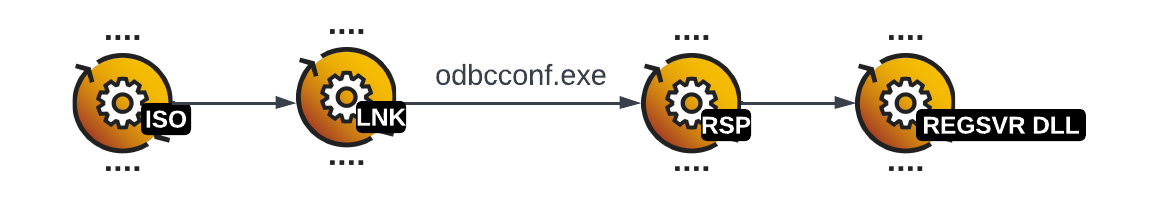
According to the report, As a general rule, spear-phishing campaigns are used to obtain initial access for delivering the attack. A modification to the method was made in the course of the year by avoiding macro-enhanced documents in favor of ISO and LNK files, which are more reliable.

A command to launch the Bumblebee loader is contained in the LNK file. The resultant conduit is then used to carry out the following actions at the next stage:
- Maintaining persistence
- Elevation of privileges
- Reconnaissance
- Theft of credentials
The Cobalt Strike adversary simulation framework was also employed to simulate the adversary’s behaviors upon gaining elevated privileges on the infected endpoint during the attack.
This provides the threat actor with the ability to move laterally across the network. AnyDesk remote desktop software can be deployed on an infected system in order to achieve persistence.
A highly privileged user’s credentials were stolen in this incident, and the details were subsequently misused to make it possible for the attacker to take control of the Active Directory server.
Recommendation
Following are the recommendations made by the Cybereason GSOC:-
- Ensure that the security tool you have installed has the Anti-Malware feature enabled.
- On your security tool, you should make sure that the Detect and Prevent modes are enabled.
- Downloaded files from the internet should be handled in a secure manner.
- In email messages that come from external sources, you should never download any files from them.
- Ensure that you have a data recovery plan in place.
- Backups of your data should be kept on a regular basis in a secure location that is accessible to you remotely.
- Ensure that your passwords are strong and that they are not easy to guess.
- Passwords should be rotated on a regular basis to ensure that they remain secure.
- It is important to make sure that two-factor authentication is enabled whenever possible.
Secure Azure AD Conditional Access – Download Free White Paper







