

There has been an addition to the Iranian APR group Charming Kitten’s malware arsenal recently with the addition of a new malicious tool. This newly added tool authorizes the threat actors to retrieve user data from the following accounts:-
- Gmail
- Yahoo!
- Microsoft Outlook
The tool was discovered by Google’s Threat Analysis Group (TAG) and is called Hyperscrape. By initiating a fake session or stealing credentials, the attacker will pose as a legitimate user in order to initiate the authentication process.
After successful execution, it downloads the whole inbox of the targeted victim by running the scraper.
Charming Kitten
As a government-sponsored organization, Charming Kitten targets high-risk users regularly. In addition to being a prolific APT, Charming Kitten is also thought to be tied to Iran’s IRGC.
Approximately two dozen Iranian accounts were targeted. Currently, the tool is in active development, with the oldest sample dating back to 2020. Cybersecurity analysts have notified the victims that their accounts have been compromised and will need to be resecured.
The primary aim of the threat actor is espionage and financial gains, and this has been clarified after tracking and analyzing the following groups:-
- APT35
- Cobalt Illusion
- ITG18
- Phosphorus
- TA453
- Yellow Garuda
Hyperscrape
This malware, Hyperscrape, is written in .NET and runs primarily on Windows-based machines. Among the features of this tool is the capability of obtaining information from an email inbox and exfiltrating its contents.
There are even instances in which it can delete security emails that are sent to the target by Google, alerting them to a suspicious login attempt.
As soon as the tool opens and downloads the email as an “.eml” file, the messages are marked as unread. Hyperscrape previously had the ability to request data from Google Takeout as a feature in earlier versions of the program.
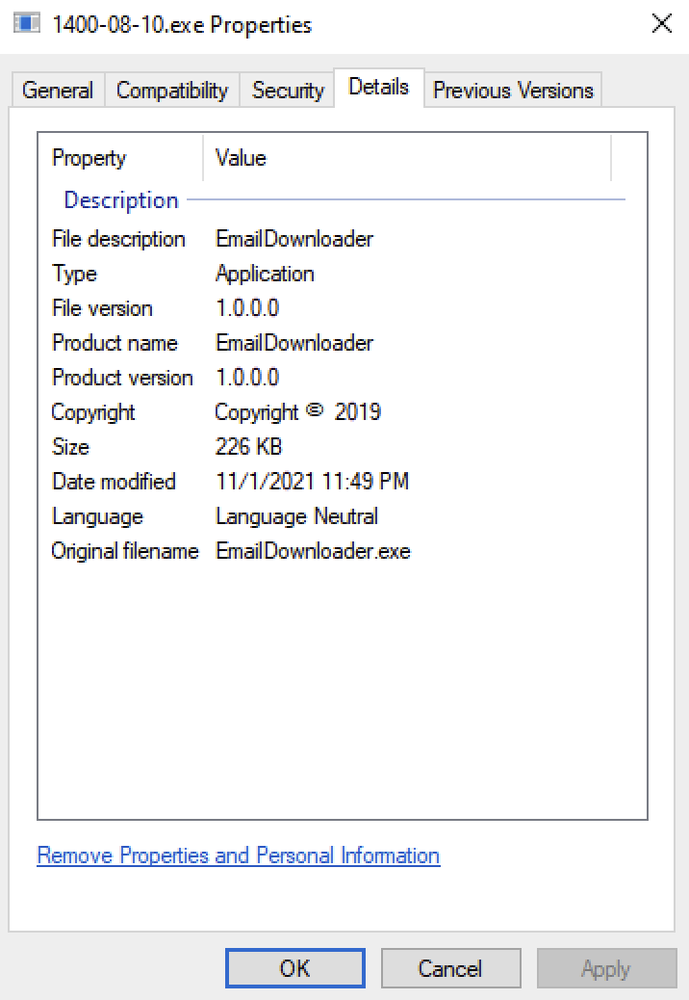
Among the features that Google Takeout offers are the ability to export your data to an archive file that can be downloaded.
This tool launches an HTTP GET request to a C2, and if it does not find the “OK” response body in the response body, then it will terminate.
A hardcoded string was used to store C2, which was unobfuscated in the version tested. There was also an obfuscation method called Base64 used in later versions.
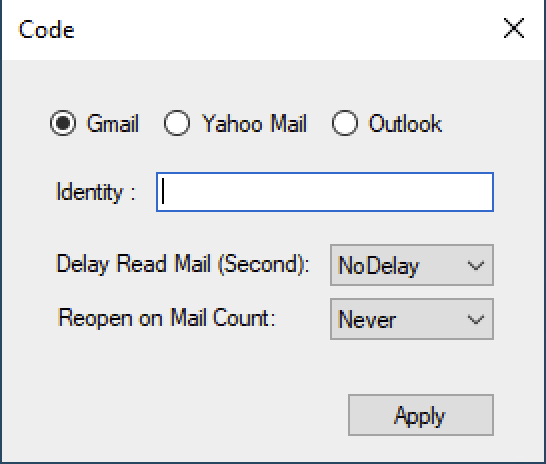
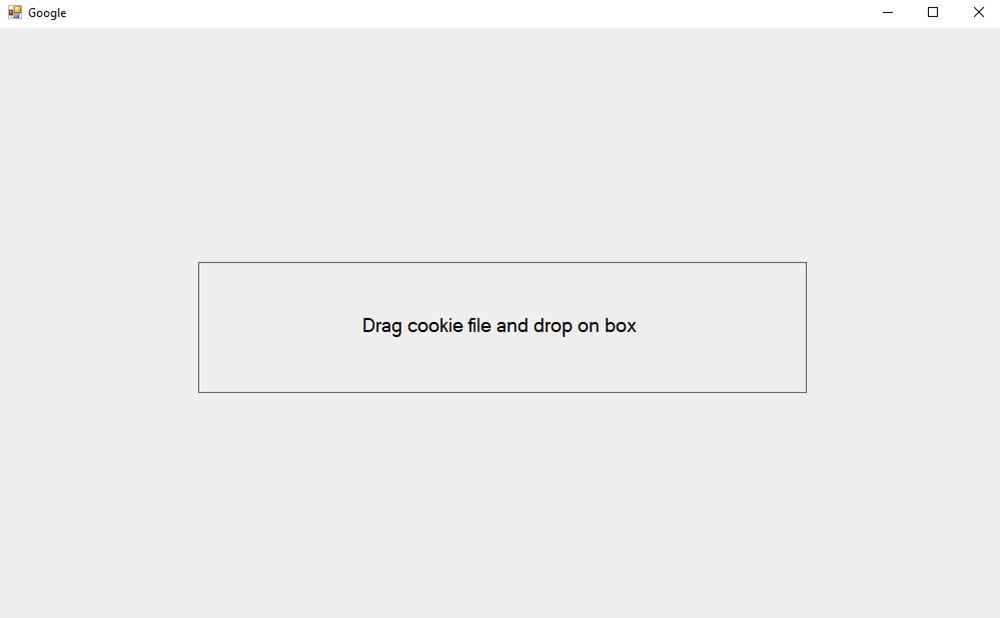
There would be a new form appearing within the system that will allow the operator to drag and drop the cookie file path into a new field if it was not supplied via the command line.
Hyperscrape’s Actions
For every email found, it performs the following actions:-
- Clicks on the email and opens it
- Downloads it
- If the email was originally unread, mark it as unread
- Goes back to the inbox
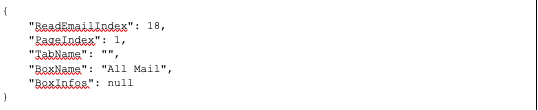
There is a folder called Downloads where the emails are saved with the extension “.eml”. Counts of the emails that have been downloaded are recorded in a log file.
There was a previous occurrence of the group making use of a custom surveillance program called LittleLooter for Android. An implant with a rich set of features capable of gathering sensitive data from compromised devices.
However, for now, the experts at TAG have confirmed that all the compromised account holders were notified about this incident to secure their accounts.
Secure Azure AD Conditional Access – Download Free White Paper







