

The Distributed Denial of Service (DDoS) attacks, hit 14 major US airport websites. The websites were temporarily shut down due to DDoS attacks led by pro-Russian hacker group ‘KillNet’, who hit back against the Western countries’ aggressive actions against Russia due to the war in Ukraine.
According Kiersten Todt, Chief of Staff of the US Cybersecurity and Infrastructure Security Agency (CISA), “Obviously, we’re tracking that, and there’s no concern about operations being disrupted”
DDoS Attacks Against Airports Websites
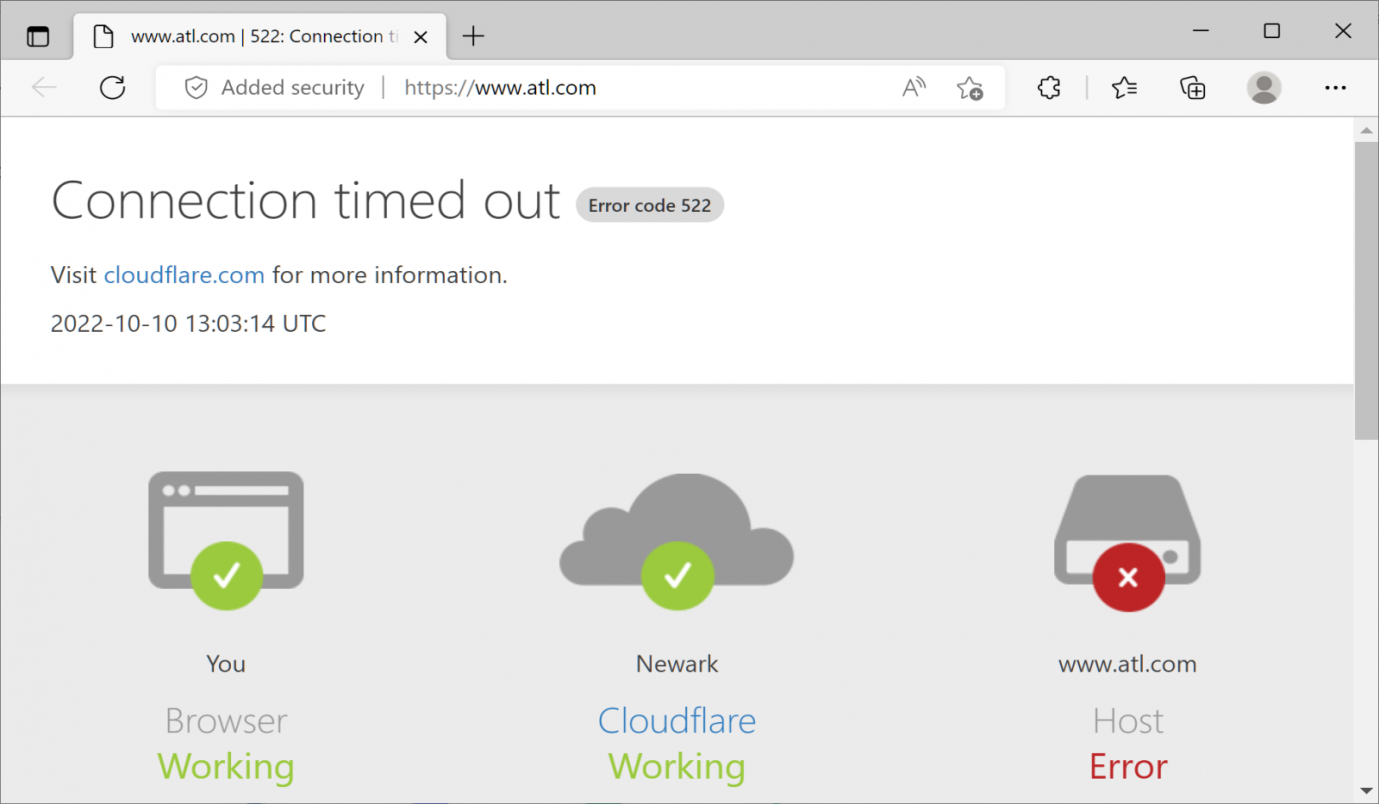
On October 10, 2022, the DDoS attacks have overwhelmed the servers hosting these sites with false web traffic, making it impossible for travellers to connect and get updates.
The following are the airport websites that were affected:
- Hartsfield-Jackson Atlanta International Airport (ATL),
- Los Angeles International Airport (LAX)
- Chicago O’Hare International Airport,
- Orlando International Airport,
- Denver International Airport,
- Phoenix Sky Harbor International Airport, and
- other airports in Kentucky, Mississippi, and Hawaii
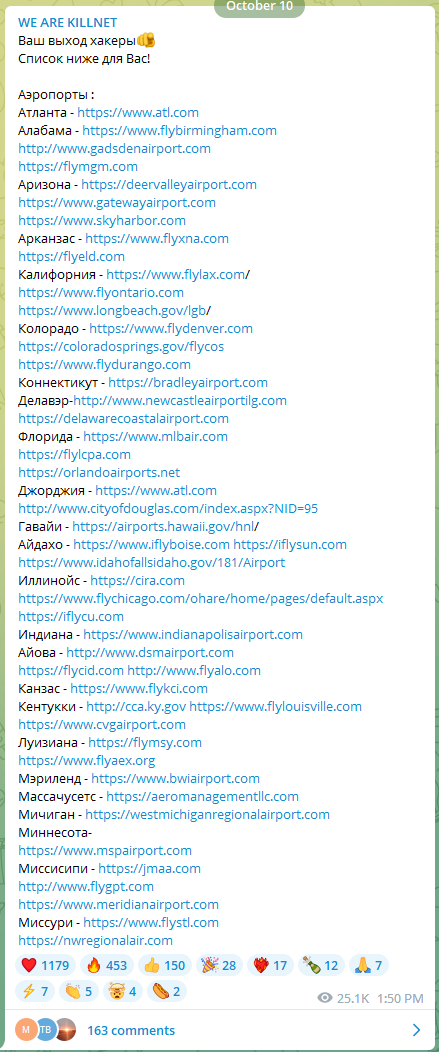
DDoS attacks seem to have hit the US airport websites after Killnet listed the US airport website domains on its Telegram channel on Sunday.
Sponsored: Block more Intense DDoS Attack , Always Enable Multi-layered Protection
Reports say the websites were targeted by volunteers with custom software designed to overwhelm the websites with false web traffic, hence making the websites unreachable to the public.
In this case, the travellers could not access the airport website to get updates about their scheduled flights or book airport services. Attackers overwhelm computer servers by sending thousands of fake requests at the same time. So the servers that host the airport sites end up being busy and tied up resolving these fake requests.
Killnet has previously claimed responsibility for mastermind behind the cyber attacks on organizations in Lithuania after the Baltic country blocked the shipment of some goods to the Russian enclave of Kaliningrad in June 2022. In August 2022, US Defence giant Lockheed Martin and its subsidiaries’ website was hacked.
“DDoS attacks are favoured by actors of varying sophistication because they have visible results, but these incidents are usually superficial and short lived,” John Hultquist, a vice president at Google-owned cybersecurity firm Mandiant.
Sponsored: Block more Intense DDoS Attack , Always Enable Multi-layered Protection







 attacks, hit 14 major US airport websites. The websites were temporarily shut down due to DDoS attacks led by pro-Russian hacker group 'KillNet', who hit back against the Western countries' aggressive actions against Russia due to the war in Ukraine.)