

Researchers discovered a new Critical Android vulnerability that may allow attackers to perform remote code execution on a vulnerable Android device and to take control of it.
The vulnerability resides in the way Android handing the proxy auto-config (PAC), a file that defines how web browsers and other user agents can automatically choose the appropriate proxy server.
In this case, Android uses a library called libpac. In order to parse the Javascript, libpac using the V8 JS engine which is the main attack surface and the version of V8 is vulnerable to recent exploit and leads to crash the PacProcessor service.
Researchers explain that “the crash wasn’t caused by an issue within V8 but instead was due to a problem with allocations of ArrayBuffers within the context of the JS function FindProxyForUrl.”
PAC settings can be accessed in Android by going to the current wifi network -> editing the advanced settings -> selecting “Proxy Auto-Config” in the proxy dropdown.
Austin Emmitt, a security researcher from NowSecure found this vulnerability in July 2019 and reported to Google and it was confirmed as “Critical” severity.
Vulnerability Details
Austin manually found the vulnerability in Android with the help of a few tools & tricks. The vulnerability occurs due to improper initialization of an object that provides methods for ArrayBuffer objects in V8.
“He refers that the vulnerability is due to the use of automatic storage of the instance of ArrayBufferAllocator on the stack on line 770 of proxy_resolver_v8.cc in the chromium-libpac library.”
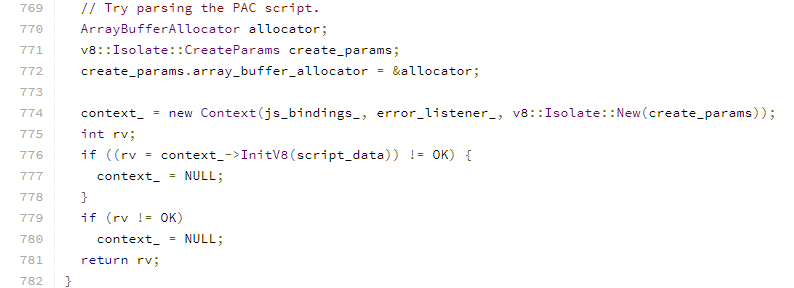
The attacker who control the PAC script has the ability to manipulate what urls are passed to “FindProxyForURL” function and also attacker can trigger the call to the ArrayBuffer functions based on whether the PAC URL matches an appropriate exploit string” said via blog post.
The vulnerability can be exploited remotely by the attacker in two different ways.
- Leak an address to executable memory
- Spray the heap sufficiently to ensure that attacker-controlled bytes are executed.
The researcher believes that the ret gadget (a sequence of instructions ending in RET is called a gadget) would give the attacker a powerful read and write primitive since this could return to the attacker an ArrayBuffer of unlimited size that can read and write any values using the normal DataView methods.”
Another advantage for attackers is the PacProcessor will restart after a crash that helps the attacker to execute an exploit as many as he can.
PoC Exploit
The researcher published a PoC exploit that uses a malicious app along with a malicious PAC script to execute arbitrary code and perform the elevation of privilege and gains the INTERNET permissions associated with PacProcessor.
The exploit can be launched by run poc.py which hosts the malicious PAC file and app. You can find the PoC code under the PoC exploit category.
“This vulnerability potentially affects any user that uses PAC scripts and could result in remote code execution. Also, Android versions below 8.0 may enable apps to set the system proxy settings, which would allow a malicious app to exploit the vulnerability without the user needing to manually set a PAC URL.” Austin Concluded.
You can also read the complete technical details here.
Also Read
NFC Beaming Vulnerability in Android Let Hackers to Infect Vulnerable Devices With Malware
Vulnerability in Qualcomm Chip Let Hackers Steal Sensitive Data From Android Devices







