

The Sophos cybersecurity researchers have recently spotted new variants of APT C-23’s Spyware, and is primarily use this Android Spyware to hack their targeted Android users in the Middle East.
This new variant has included all new features into their malicious apps which makes them more resilient to actions by users and who might try to extract them manually.
Not only this, but it also extracts the security and web hosting companies that try to block access to, or to shut down, their command-and-control server domains; and this group has been active since 2017.
However, the new variants come in the style of an app that indicates to install updates on the victim’s phone, with names that incorporate:-
- App Updates
- System Apps Updates
- Android Update Intelligence
Changing Covers After Installation
Initially, when the user opens the app for the first time, it captures all of your data to make it easier for them to spy on you.
The app also enables the developers to see all your data remotely; in short, those who use this app, the threat actor, could know about all their data and information.
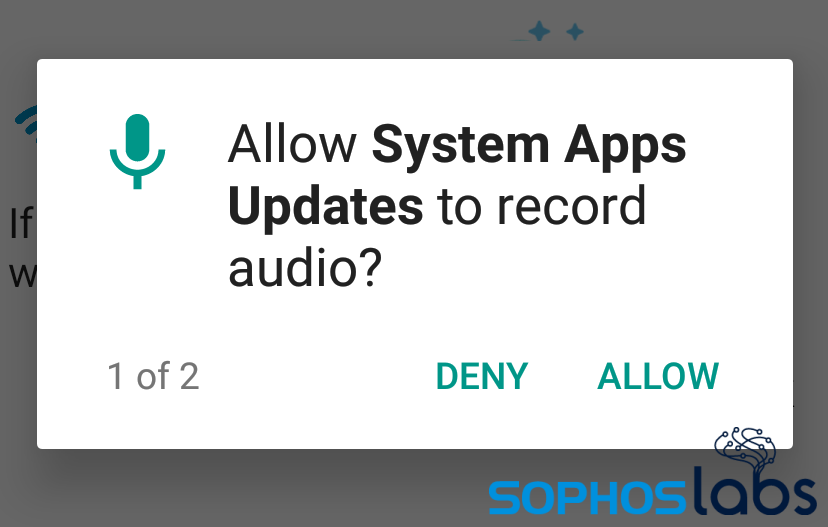
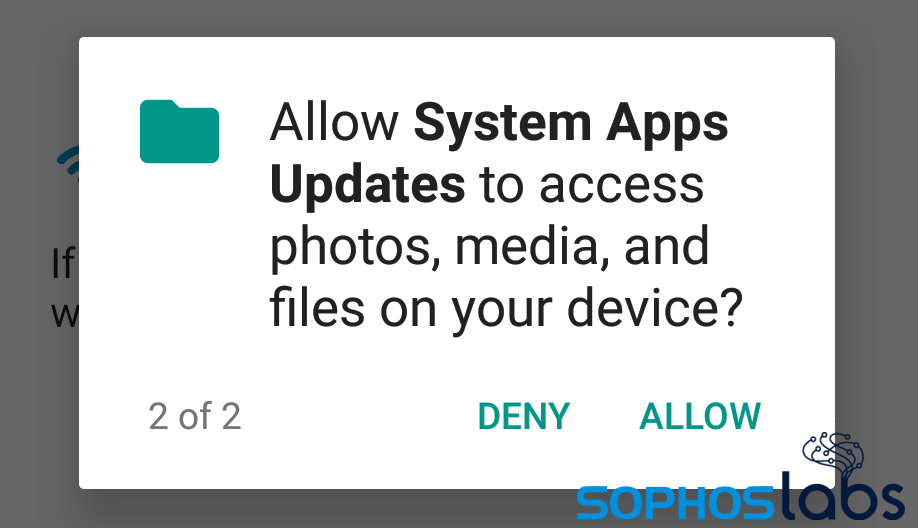
However, the app seems to be a scam; it is specifically designed to get users’ attention and ask them to give it more permissions.
The app’s requests resemble to justify the need for the supplementary features, but all these are a scam that attracts users’ attention.
For example, the request to “Enable Notifications” claims that the app needs this functionality or else “you won’t receive notifications in real-time.”
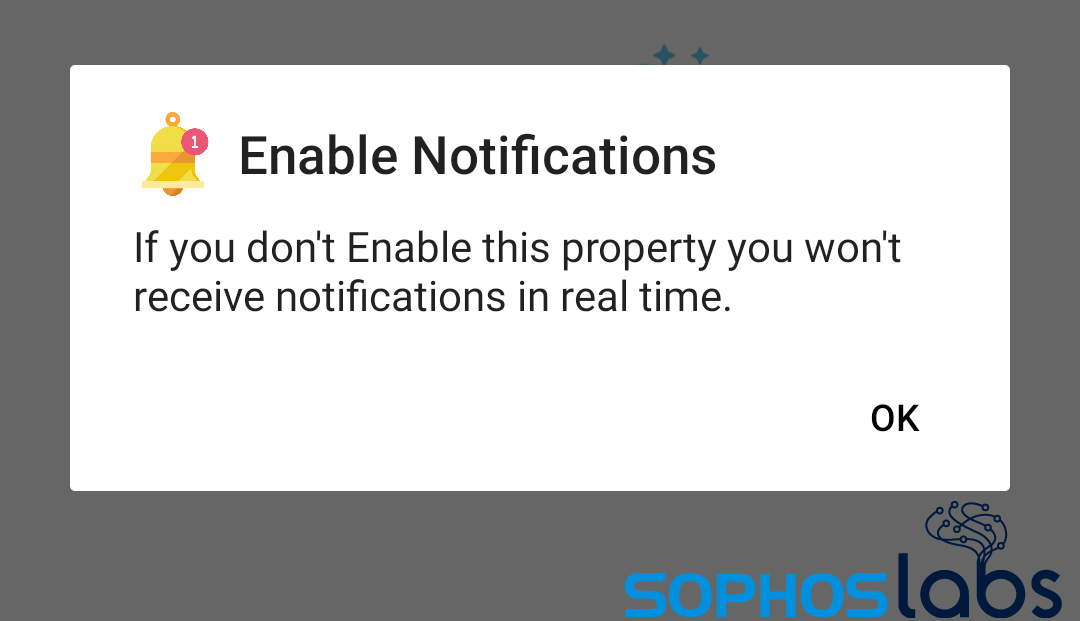
All this permission grants Spyware the capability to understand the full-text messages and the names of contacts, from any messaging apps, like Facebook or WhatsApp.
Functionalities of the Spyware
Some functions are played by the Spyware, and here we have mentioned them below:-
- Assembles SMS, contacts, call logs
- Assembles images and documents
- To record audio, incoming and outgoing calls, including WhatsApp calls
- To take screenshots and record video of the screen
- Taking pictures utilizing the camera
- Protecting its icon
- Reading notifications from WhatsApp, Facebook, Facebook Messenger, Telegram, Skype, IMO Messenger, or Signal.
- Deleting notifications from built-in security apps and Android system apps, package Installer, and its notifications.
Recommendations
Here are some recommendations suggested by the experts:-
- Users must install apps from all trusted sources such as Google Play.
- Users always prefer updating Android OS and applications through Android Settings and Google Play.
- Users must not rely upon third-party apps.
Since spyware attacks are increasing rapidly, and Android Spyware is one of the most popular Spyware produced by APT-C-23 starting four years ago. That’s why it is important to stay protected from such attacks.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity updates.







