

Google has introduced a new data deletion policy for the Google Play Store with the intention of giving customers more knowledge and control over their in-app data.
Because Google wants users to be able to delete their data without reinstalling each app, developers who provide an in-app account deletion experience will also have to provide a web-based option.
“As the new policy states, when you fulfill a request to delete an account, you must also delete the data associated with that account,” Google.
“The feature also gives developers a way to provide more choice: users who may not want to delete their account entirely can choose to delete other data only where applicable (such as activity history, images, or videos).”
“For developers that need to retain certain data for legitimate reasons such as security, fraud prevention, or regulatory compliance, you must clearly disclose those data retention practices.”
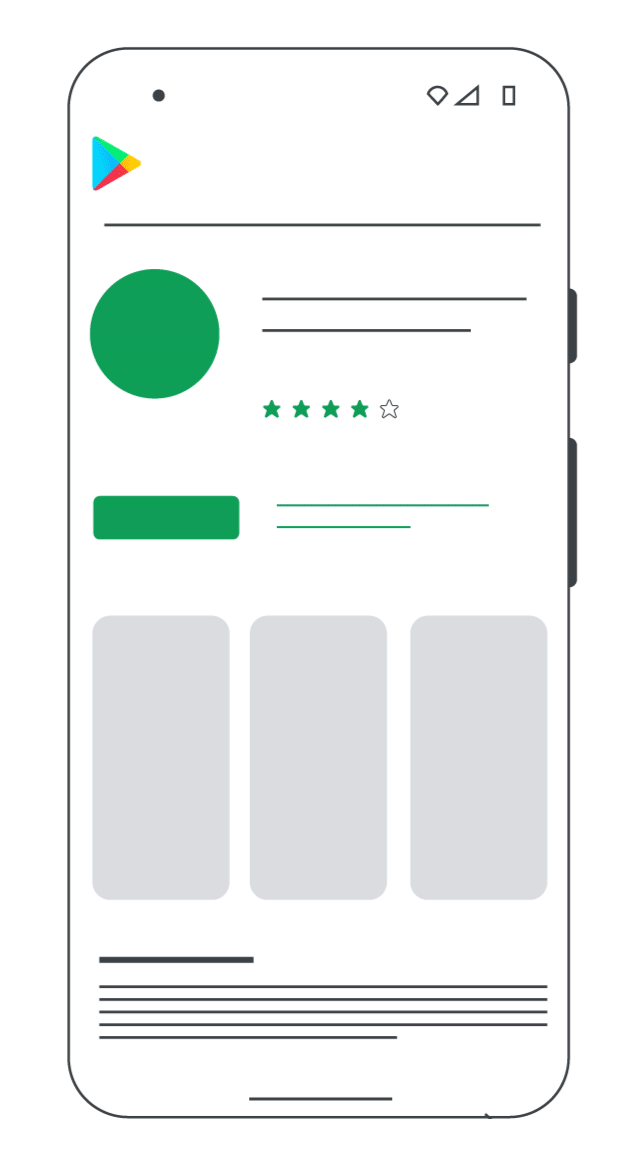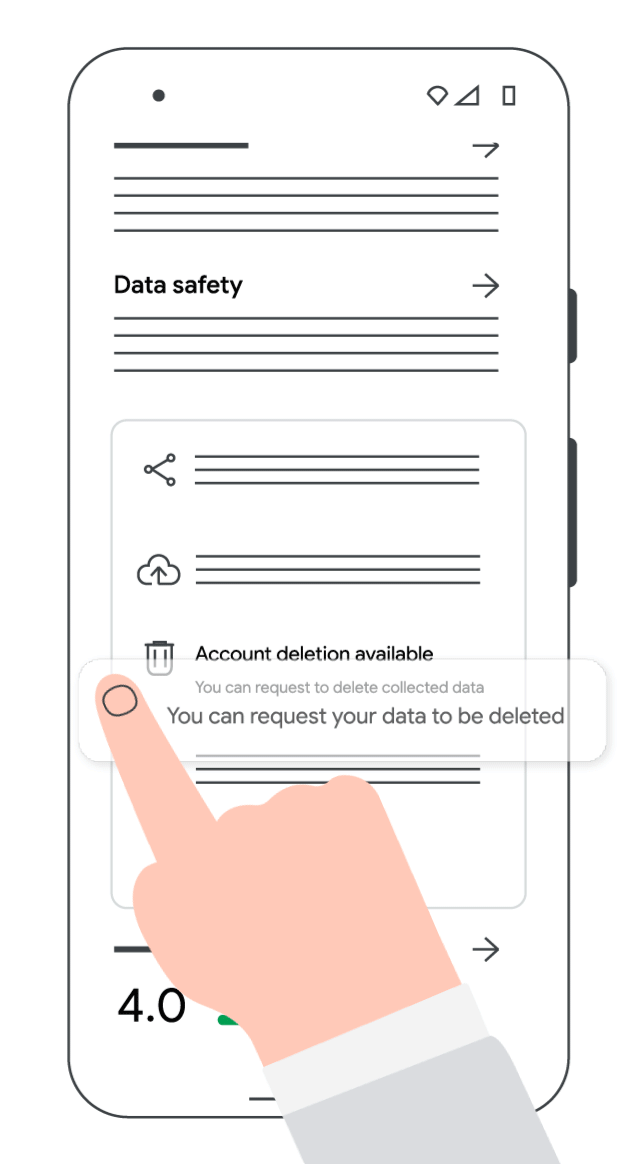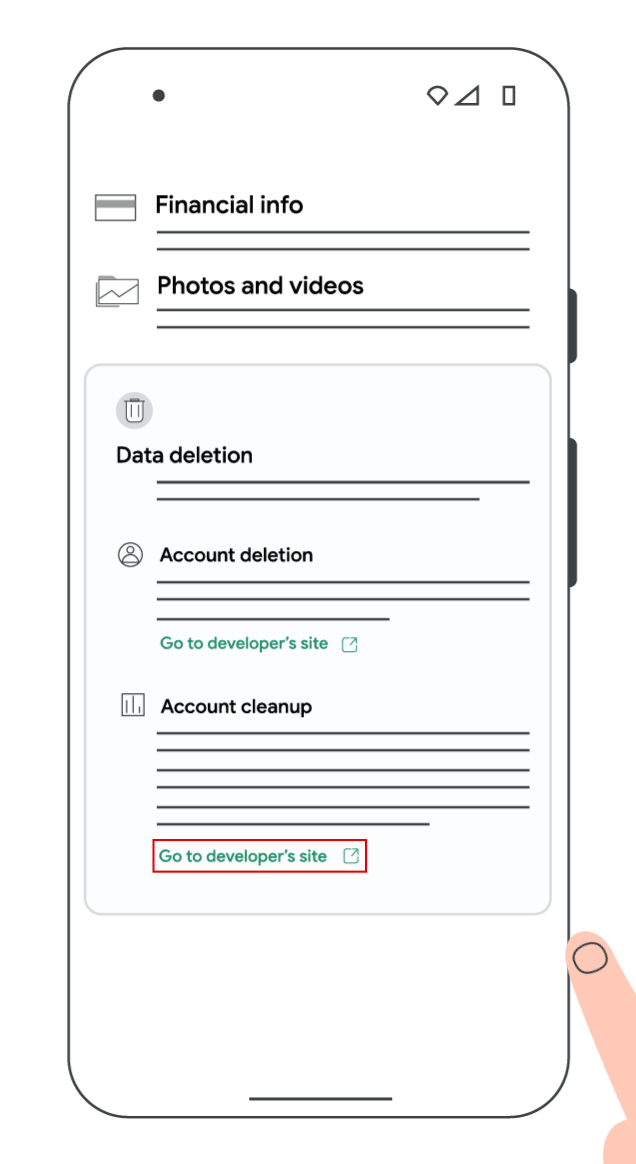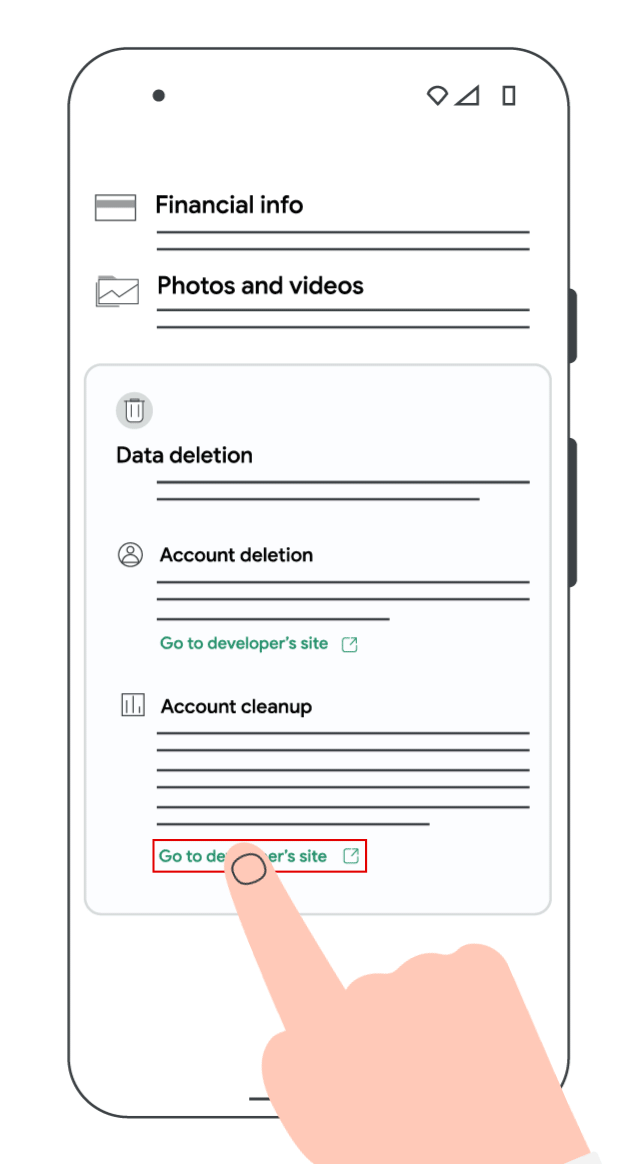
The company stated that by December 7, it will ask developers to answer questions about their app’s data deletion in the Data Safety form.
The developer responses in the form are reflected in Google Play’s Data Safety section, which provides users with labels containing information about an app’s data collection practices.
Next year, the new Play Store policy will be fully implemented, but until then, developers must give more information by the given time regarding their data deletion procedures.
No one will be permitted to publish new apps or release app updates any longer if they fail to provide the necessary deletion procedure information on time.
Beginning in early 2024, users can see the submitted data deletion information in the app store listings, including updated data deletion badges in the new Data deletion area and the Data safety area.
Also, after May 31, 2024, non-compliant apps may be removed from Google Play; however, developers may still request an extension through the Play Console.
Searching to secure your APIs? – Try Free API Penetration Testing
Related Read:
- Beware: Malicious Apps On Apple & Google Play Push Users into Fake Investments
- Android Malware on Google Play with 2 Million Installs Steal Sensitive Data
- Over 75 Applications on Google Play with 13M Installations Deliver Adware
- Android Apps on Google Play Store to Distribute Banking Malware as Document Scanners


