

Drinik Android trojan is using a new version to target 18 Indian banks, posing as the app used by the country to manage tax payments. The main aim of these criminals is to steal personal and bank account information from their victims.
Malware known as Drinik has been in the news since 2016 and is a relatively old malware. As a result of this malware, the Indian government has previously issued a warning to Android users regarding the possibility of stolen information being used to generate income tax refunds.
Currently, the Drinik app is available as an APK file that is integrated into the iAssist app for Android. Constant monitoring of the different variants of Drinik Android malware has been conducted by Cyble Research & Intelligence Labs over the past few years.
In the case of this malware variant, it communicates with a Command & Control (C&C) server hosted on IP 198[.]12[.]107.13. The previous campaign had also used the same IP address for its command and control communication, which indicates that the same Threat Actor (TA) was behind both campaigns.
Drinik’s Evolution
CRIL has observed this malware to have 3 different variants since last year. In September 2021, the first malware variant appeared on the scene, which was used to steal credentials using phishing pages.
Two new variants of the virus have been discovered in the wild during the year 2022, which include the ability to record screen activity and log keystrokes.
However, the new variant of the malware has different features, and that’s why we have mentioned all the elements in the below list:-
- Keylogging
- Abuses Accessibility
- A phishing page is being used to harvest credentials
- The payload APK is downloaded
- Sends SMS from the infected device
- Steal incoming SMSs
- Overlay attack
- Screen recording
- Receiving commands via FirebaseCloudMessaging
Stealing User’s Data
In its most recent version, the malware appears as an APK named ‘iAssist,’ which is allegedly the official tax management tool of the Income Tax Department of India.
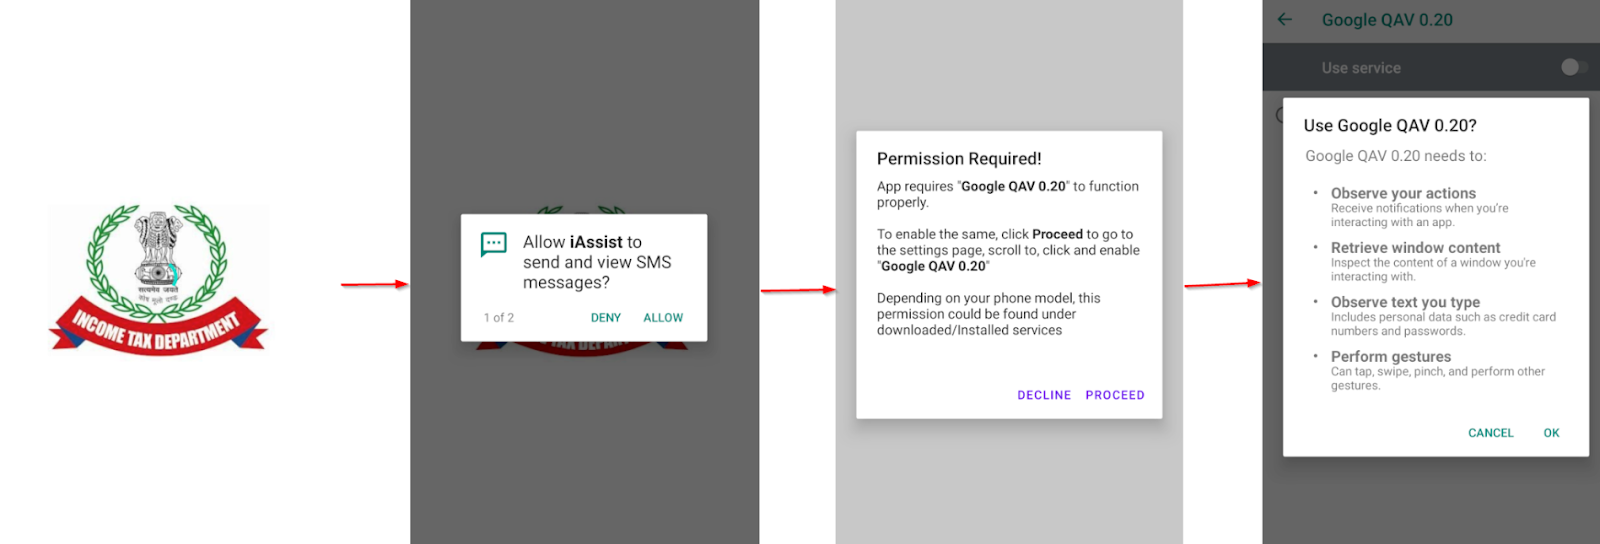
When the application is installed, it will request access to the user’s SMS, call log, and external storage devices. While apart from this, a permission request will also be made for receiving, reading, and sending SMS messages.
The next step is to ask the user if they wish to give the app permission to use the Accessibility Service. Upon granting permission, it uses Google Play Protect to perform the following tasks:-
- Navigation gestures
- Record the screen
- Capture keystrokes

By the end of the app, the actual Indian income tax website will be loaded via WebView instead of phishing pages; the app will be set up to steal the user credentials through screen recordings and keylogging.
APK Metadata Info
- App Name: iAssist
- Package Name: lincoln.auy.iAssist
- SHA256 Hash: 86acaac2a95d0b7ebf60e56bca3ce400ef2f9080dbc463d6b408314c265cb523
Banks were targeted
Using the Accessibility Service, Drinik constantly keeps an eye on events related to the targeted banking apps so that they can easily implement their attacking process.
Several banks are being targeted, including SBI (State Bank of India), a bank that serves more than 450,000,000 people daily with a huge network of 22,000 active branches.
Using the keystroke data collected from the users, the malware will attempt to exploit that user’s credentials to send them to a C2 server if it finds any match.
Recommendations
The cybersecurity experts have recommended some mitigations, so we have listed them below:-
- Software should only be downloaded and installed from official apps stores.
- Untrusted sources should never have access to your card details, CVV number, card PIN, or Net Banking credentials.
- Make sure you are using a reputable antivirus.
- Multi-factor authentication should be enforced wherever possible.
- Always use strong and unique passwords.
Also Read: Download Secure Web Filtering – Free E-book







