

On Friday, Google released a beta version of Client-side encryption (CSE) for Gmail. This newest service is only useful to organisations that can produce their own decryption keys because CSE is designed for organisational use.
Google has now made “end-to-end encryption” available for Gmail on the web, following Meta’s 2016 offer to use it for WhatsApp. However, it only provides client-side encryption (CSE).
Notably, Client-side encryption (Google refers to as E2EE) was already available for users of Google Drive, Google Docs, Sheets, Slides, Google Meet, and Google Calendar (beta).
“We’re expanding customer access to client-side encryption in Gmail on the web. Google Workspace Enterprise plus, Education plus, and Education Standard customers are eligible to apply for the beta until January 20th, 2022”, Google announces.
End-To-End Encryption for Gmail
Sensitive information in the email body and attachments are rendered unreadable by Google servers using client-side encryption in Gmail. Customers retain control of both the identity service used to access encryption keys.
“You can use your own encryption keys to encrypt your organization’s data, in addition to using the default encryption that Google Workspace provides,” explains Google.
“With Google Workspace Client-side encryption (CSE), content encryption is handled in the client’s browser before any data is transmitted or stored in Drive’s cloud-based storage.
“That way, Google servers can’t access your encryption keys and decrypt your data. After you set up CSE, you can choose which users can create client-side encrypted content and share it internally or externally.”
Google Workspace already uses the latest cryptographic standards to encrypt all data at rest and in transit between our facilities. Client-side encryption supports a wide range of data sovereignty and compliance requirements while enhancing the secrecy of your data.
For customers of Google Workspace Enterprise Plus, Education Plus, and Education Standard, Gmail E2EE beta is presently available.
By submitting their Gmail CSE Beta Test Application, which should include the email address, Project ID, and test group domain, they can apply for the beta until January 20, 2023.
Google says this feature will be OFF by default and can be enabled at the domain, OU, and Group levels (Admin console > Security > Access and data control > Client-side encryption).
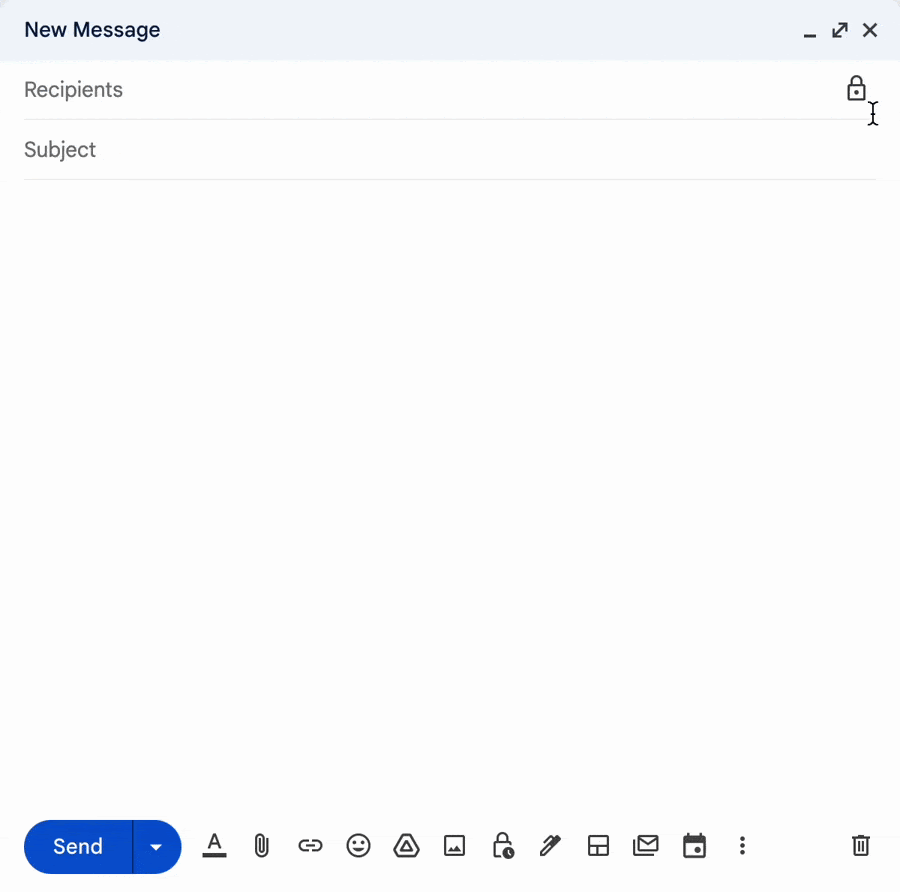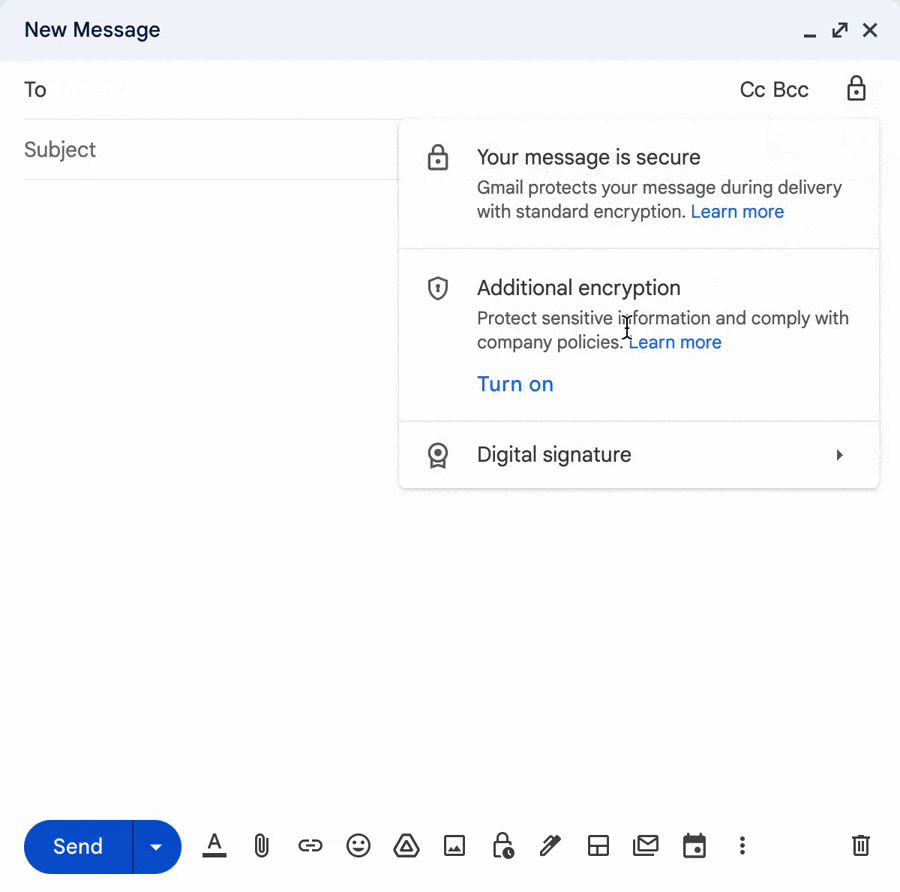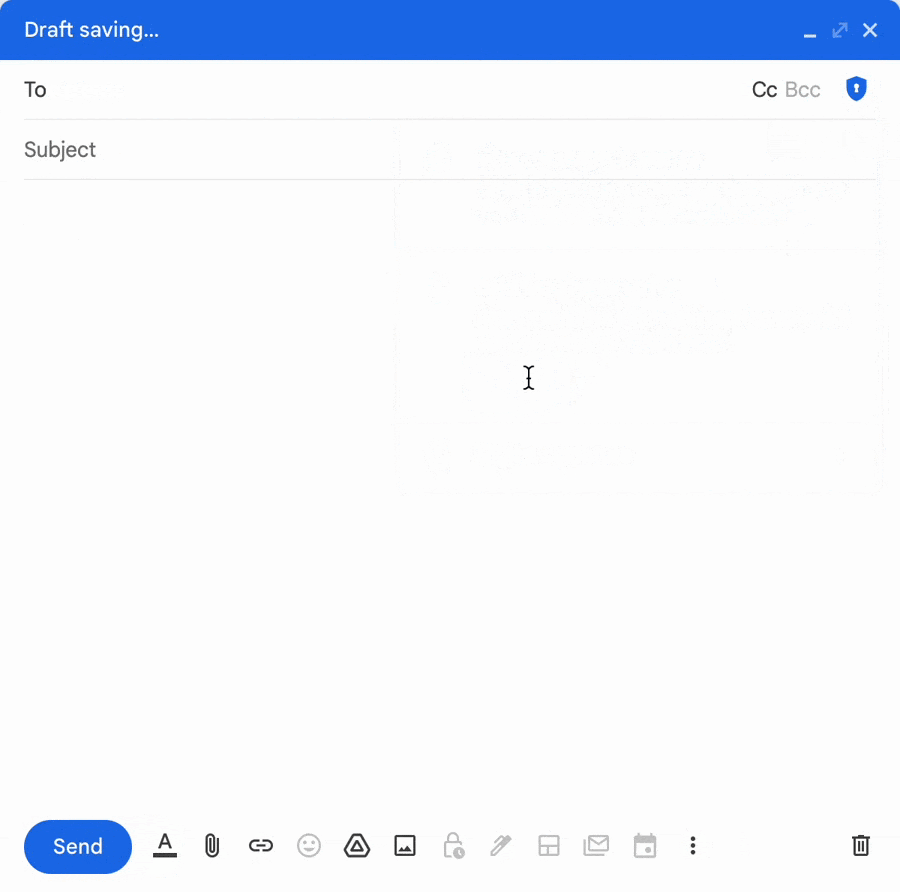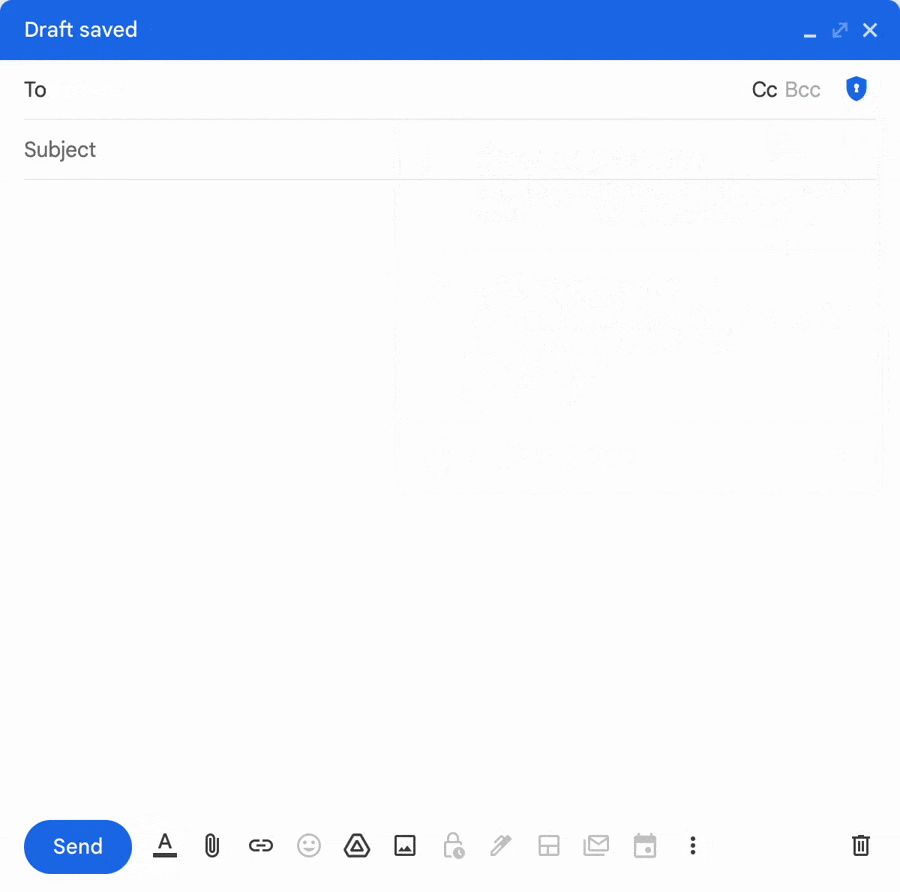
To add client-side encryption to any message, click the lock icon and select additional encryption, compose your message and add attachments as normal.
Also, the feature is not available to Google Workspace Essentials, Business Starter, Business Standard, Business Plus, Enterprise Essentials, Education Fundamentals, Frontline, and Nonprofits, as well as legacy G Suite Basic and Business customers. Also, the service has not yet been rolled out for personal accounts.
Finally, End-to-end encryption is something we take for granted in the modern era when hacking and data leakage is becoming more frequent occurrences.
Secure Web Gateway – Web Filter Rules, Activity Tracking & Malware Protection – Download Free E-Book


 for Gmail. This newest service is only useful to organisations that can produce their own decryption keys because CSE is designed for organisational use.)