

Security researchers have uncovered a massive coordinated exploitation campaign where threat actors launched over 2.5 million malicious requests against vulnerable systems during the Christmas 2025 holiday period.
The campaign represents a sophisticated, multi-faceted initial access broker operation targeting Adobe ColdFusion servers alongside 46 additional technology stacks across nearly 800 vulnerabilities.
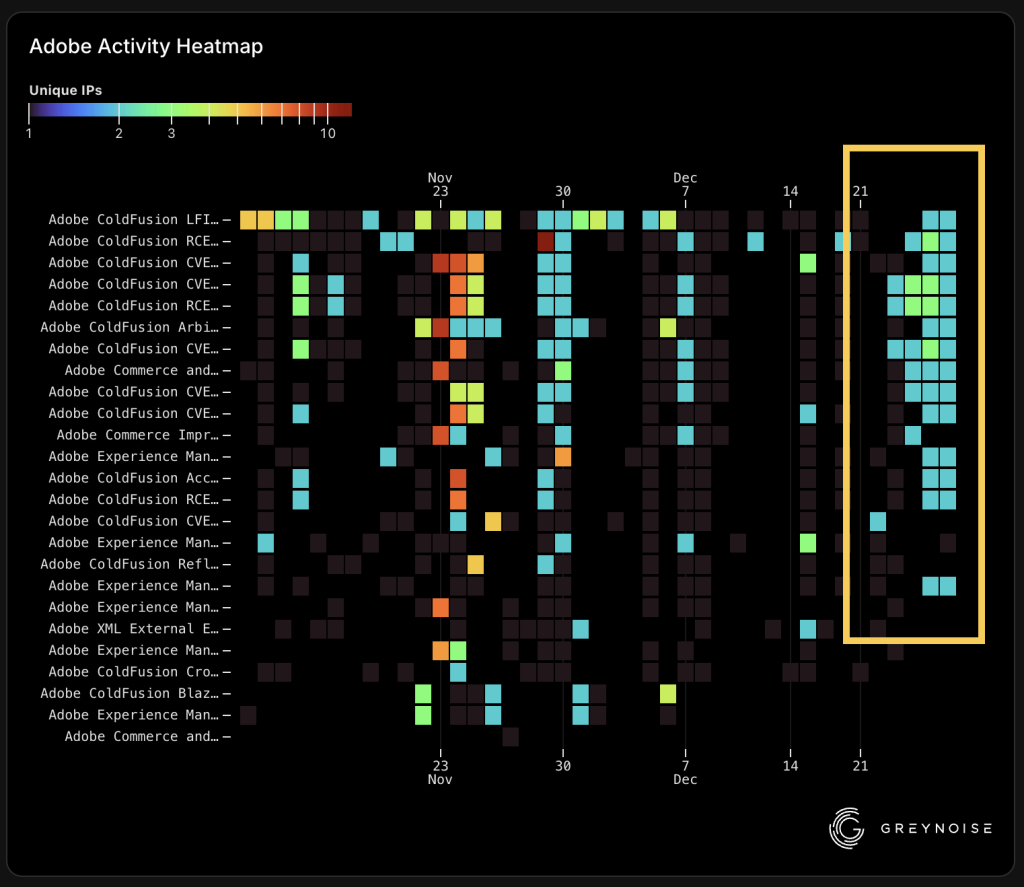
The primary attack wave focused on 10+ Adobe ColdFusion CVEs, with researchers identifying just under 6,000 direct requests against ColdFusion infrastructure.
However, deeper analysis revealed the true scope: two primary IP addresses operating from Japan-based hosting provider CTG Server Limited generated over 2.5 million requests across 767 distinct CVEs, leveraging approximately 10,000 unique callback domains for attack verification.
The threat actors deliberately timed the campaign for maximum impact, concentrating 68 percent of attack traffic on Christmas Day when security teams typically operate at reduced capacity.
This deliberate timing suggests a sophisticated threat actor with operational knowledge of enterprise security monitoring cycles.
The attackers used ProjectDiscovery Interactsh out-of-band callback infrastructure to verify successful exploitation attempts in real-time, enabling rapid identification of vulnerable systems suitable for follow-up compromise.
The campaign exploited critical vulnerabilities including CVE-2023-26359, a deserialization RCE affecting ColdFusion, which received 833 exploitation attempts.
CVE-2023-38205, an access control bypass, was targeted 654 times, while CVE-2023-44353 triggered 611 requests.
| CVE ID | Vulnerability Type | Requests |
|---|---|---|
| CVE-2023-26359 | Deserialization RCE | 833 |
| CVE-2023-38205 | Access Control Bypass | 654 |
| CVE-2023-44353 | Remote Code Execution | 611 |
| CVE-2023-38203 | Remote Code Execution | 346 |
| CVE-2023-38204 | Remote Code Execution | 346 |
| CVE-2023-29298 | Access Control Bypass | 342 |
| CVE-2023-29300 | Remote Code Execution | 176 |
| CVE-2023-26347 | Access Control Bypass | 171 |
| CVE-2024-20767 | Arbitrary File Read | 146 |
| CVE-2023-44352 | Reflected XSS | 8 |
The primary attack vector employed JNDI/LDAP injection through WDDX deserialization, leveraging the JdbcRowSetImpl gadget chain to trigger remote code execution.
Beyond ColdFusion, the campaign demonstrates methodical reconnaissance across enterprise infrastructure.
Researchers at Greynoise identified 4,118 unique HTTP fingerprints and targeting of Java application servers, web frameworks, CMS platforms, Atlassian products, network devices, and surveillance systems.
| IP Address | Organization | Requests | Percentage | ASN |
|---|---|---|---|---|
| 134.122.136.119 | CTG Server Limited | 3,188 | 53.7% | AS152194 |
| 134.122.136.96 | CTG Server Limited | 2,683 | 45.2% | AS152194 |
| 23.234.85.20 | tzulo, inc. | 34 | 0.6% | AS11878 |
| 38.225.206.87 | Kennies Star India | 12 | 0.2% | AS150654 |
| 38.225.206.88 | Kennies Star India | 11 | 0.2% | AS150654 |
| 172.81.132.99 | DataWagon LLC | 7 | 0.1% | AS27176 |
Confluence OGNL vulnerability CVE-2022-26134 alone received 12,481 requests, while the legacy Shellshock vulnerability CVE-2014-6271 triggered 8,527 attempts.
The threat actors operated from AS152194 (CTG Server Limited), a Hong Kong-registered hosting provider with documented associations to phishing infrastructure and spam operations.
Security researchers have identified the network as hosting FUNNULL CDN infrastructure targeting luxury brands. This combination of abuse history and rapid IP space acquisition suggests limited abuse enforcement mechanisms.
Organizations operating Adobe ColdFusion servers should immediately apply security patches for CVE-2023-26359, CVE-2023-38205, and related vulnerabilities.
Security teams should implement network-based detection for JNDI injection payloads, OAST callback domains, and the identified threat actor IP addresses and JA4+ network fingerprints.
Continuous vulnerability scanning and monitoring of exploitation attempt patterns remain critical defensive priorities.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


