

The Lapsus$ hacking group recently compromised one of Microsoft’s employees, which allowed the threat actors to steal parts of Microsoft’s source code. There is evidence of a destructive element within Microsoft Security teams’ efforts to track a large-scale social engineering campaign.
As a result, Microsoft Azure DevOps server source code (37GB) was recently released by the Lapsus$ hacking group, and Microsoft has tracked this group as DEV-0537.
The stolen source code which is released by the threat actors includes several internal projects of Microsoft for:-
- Bing
- Cortana
- Bing Maps
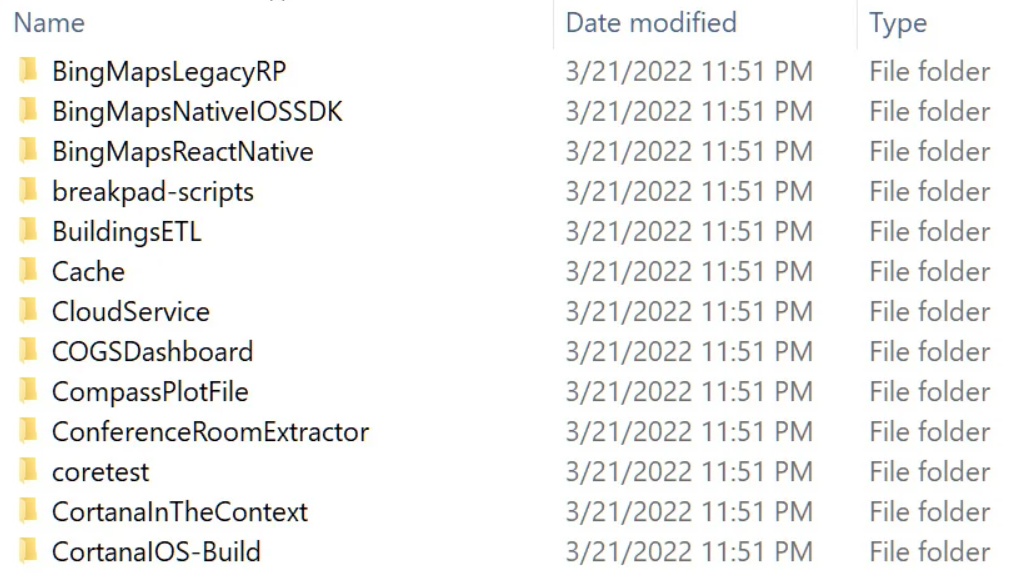
An employee account at Microsoft has been compromised by Lapsus$, giving it limited access to the source code repository, confirmed by Microsoft itself.
Targets
A main characteristic of DEV-0537 is that it uses a pure extortion and destruction attack model without deploying ransomware. Initially, DEV-0537 started targeting organizations in the following countries:-
- The United Kingdom
- South America
However, now the operators of this group have expanded their range to the global targets in the following sectors:-
- Organizations in government
- Technology
- Telecom
- Media
- Retail
- Healthcare
- Cryptocurrency exchanges
Microsoft explained in an advisory:-
“No customer code or data was involved in the observed activities. Our investigation has found a single account had been compromised, granting limited access. Microsoft does not rely on the secrecy of code as a security measure and viewing source code does not lead to elevation of risk. The tactics DEV-0537 used in this intrusion reflect the tactics and techniques discussed in this blog.”
Methods Used to Compromise the Credentials
The main goal of the Lapsus$ hacking group is to gain access to corporate networks through compromised credentials, and below here we have mentioned all the methods used by them to compromise the credentials:-
- By using the malicious Redline password stealer, secure sessions can be obtained and passwords can be stolen.
- On criminal underground forums, buying credentials and session tokens is common.
- An employee at a target organization is paid in return for access to credentials and approval of multi-factor authentication.
- Finding exposed credentials in public code repositories.
Additionally, these credentials give the hacking group access to source code repositories on the following platforms:-
- GitLab
- GitHub
- Azure DevOps
In addition to harvesting valuable data, the threat actors are then exploiting NordVPN connections to conceal their locations while executing destructive attacks on the infrastructure of victims to initiate the incident response.
Recommendations
To protect against threats such as those posed by Lapsus$, Microsoft recommends the following measures:-
- Make sure to enable or implement MFA.
- Make sure your endpoints are healthy and trusted.
- Make VPNs more secure by utilizing modern authentication methods.
- Maintain and strengthen the security of your cloud environment.
- Awareness of social engineering attacks should be improved.
- In response to the DEV-0537 intrusions, implement operational security processes.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.







