

By default, Microsoft will block the execution of VBA macros in five Microsoft Office applications to block the hack attacks. Users of the following Microsoft product will not be able to enable the macro scripts in untrusted documents that are downloaded from the internet:-
- Microsoft Access
- Microsoft Excel
- Microsoft PowerPoint
- Microsoft Visio
- Microsoft Word
To protect the users from a range of dangerous malware whose operators depend on deceptive, malicious methods, Microsoft has intended and executed this change.
While Microsoft has stated:-
“While we provided a notification bar to warn users about these macros, users could still decide to enable the macros by clicking a button. Bad actors send macros in Office files to end-users who unknowingly enable them, malicious payloads are delivered, and the impact can be severe including malware, compromised identity, data loss, and remote access.”
Mark of the Web (MOTW)
On the internet, through email or website, users receive a document; then, after opening the document, users were promoted to allow and run the malicious Microsoft macro.
Here users can be lured to enable the attacker to gain the initial foothold into the system. In this new change, a security risk banner was displayed by the app, which states:-
“Microsoft has blocked macros from running because the source of the file is untrusted.”
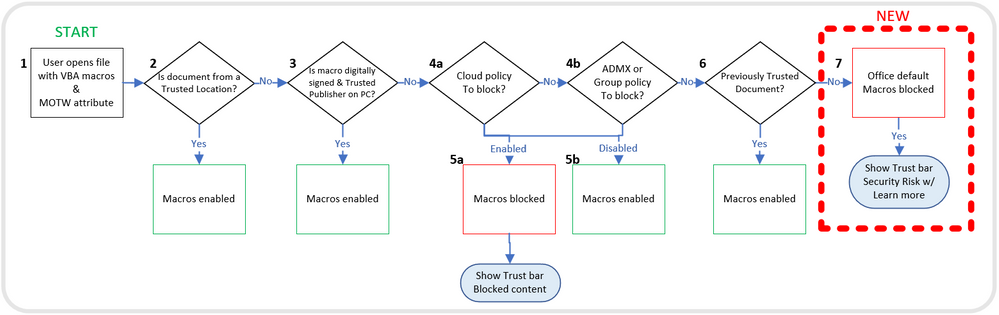
While for Microsoft, this issue was not easy to solve since VBA macros are often used by the companies to automate certain operations and tasks when opening specific files like:-
- Importing data
- Updating content
Apart from this, from April 2022, users will notice a warning in which Microsoft will notify the users about the macros in documents that cannot be enabled for security reasons.

However, from an organization’s trusted network, the documents that will contain the VBA macros will still be able to run. While this new implementation will be visible in the Microsoft Office 2203 version; this current channel will start in early April 2022.
This will later become available in other update channels like:-
- Current Channel
- Monthly Enterprise Channel
- Semi-Annual Enterprise Channel
Moreover, Microsoft has also intended to enforce the change in other versions of Office-like:-
- Office LTSC
- Office 2021
- Office 2019
- Office 2016
- Office 2013
To stop users from accidentally opening the files from the internet that contain macros, the organizations can use “Block macros from running in Office files from the Internet.”
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity updates.






