

Large-scale well-organized phishing as a service (PhaaS) operation is uncovered recently by Microsoft. This platform helps users to customize campaigns and develop their own phishing ploys.
The PhaaS platform can be used for phishing kits, email templates, and hosting services. The operation was marketed by the threat actors as Bulletprooflink when they found a high volume of a unique sub-domain.
Full-Scale Phishing Facilitator
Bulletprooflink provides a starting point for people to get into phishing campaigns without any significant resources. Multiple sites are maintained under aliases and the group is assumed to be active since 2018.
Here are the things offered by the ground as their serves:-
- Instructional videos
- Advertisements
- Promotional materials
While the security researchers have asserted that it is known to hawk their wares on plenty of underground forums.
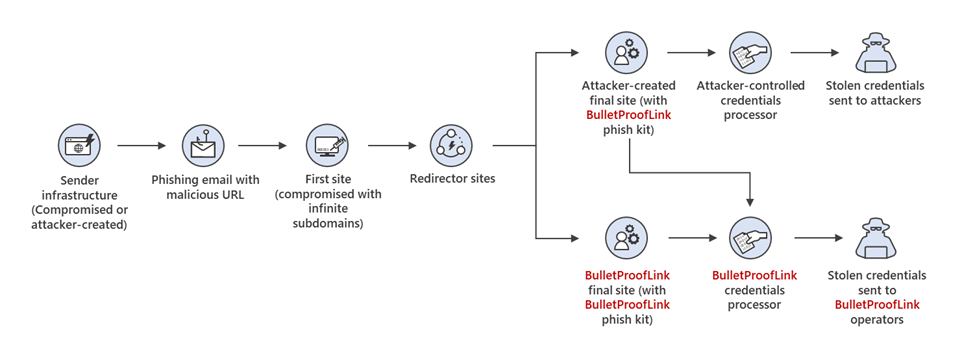
Moreover, this massive malicious campaign is notable because in this campaign the operators have used more than a high volume of newly created and unique subdomains in a single run and the count of new domains ranges more than 300,000.
Phishing kits and phishing-as-a-service (PhaaS)
Phishing kits generally refer to kits that are sold on a one-time sale basis from phishing kit sellers are resellers. This also includes different files that come with ready-to-use email phishing templates designed to evade detection.
Phishing-as-a-service is a software model which needs threat actors to pay an operator to develop complete Phishing campaigns. Bulletprooflink is an example of a phishing-as-a-service operation.
Double theft used to boost profits
Buletprooflink operation is spotted while investigating phishing attacks, and it is the driving force that has eventually targeted many corporate organizations.
The threat actors who are behind the Bulletprooflink provide cybercriminals with several services. It ranges from selling phish kits and email templates to providing posting automated services under single payment on a monthly subscription.
Break down of BulletProofLink services
According to the group’s about us web page the operator maintains multiple sites under their aliases, Bulletprooflink, anthrax which also includes Youtube with instructional advertisements and promotional materials.
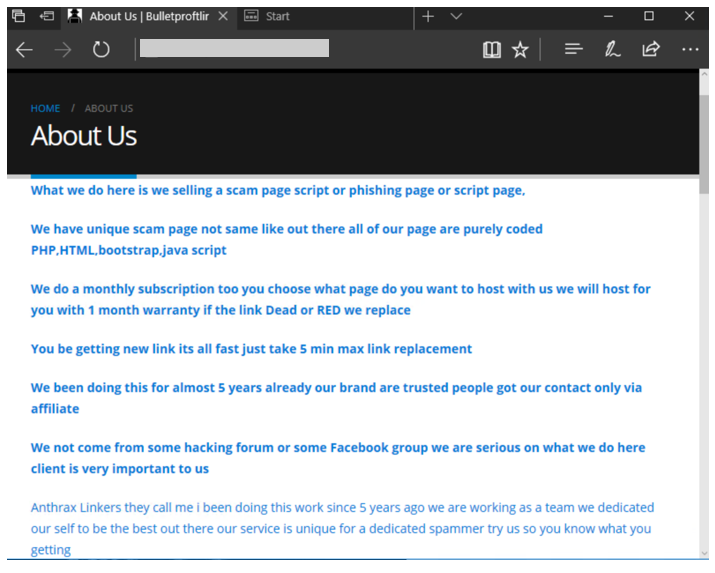
As per the ICQ chat logs posted by the operator customer refer to the group as the aliases interchanging. All these details are rugged upon by the templates, services provided by Bulletprooflink operators.
Here are the things offered in BulletProofLink services:-
- BulletProofLink registration and sign-in pages
- Credential phishing templates
- Customer hosting and support
How does Microsoft Defender for Office 365 guard against PhaaS-driven phishing attacks?
Protection against particular attacks is allowed through investigation, while the specific email campaigns help to detect similar attacks that used the same methods such as infinite subdomain abuse, brand impersonation, etc.
We are able to scale and expand the coverage of these protections to multiple campaigns by studying phishing as a service operation. Microsoft defender for office 365 can help in taking full advantage of the tools that are available and strengthen defenses against the threat of Phishing.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity updates.







 operation is uncovered recently by Microsoft.)