

Researchers discovered an advanced SMS phishing attack on some of the targeted Android phone’s that allows a remote attacker to trick victims in accepting the new settings and control the browser home page, Email server over the air.
There are certain Android smartphone model vulnerable for this SMS phishing attack that including Samsung, Huawei, LG, and Sony.
Basically, the network operators using a process called “over-the-air (OTA) provisioning” also called as ” Open Mobile Alliance Client Provisioning (OMA CP) ” to deploy the network-specific settings when new phone joining their network.
Attackers perform this advanced SMS phishing attack by abusing the OTA provisioning to send the malicious settings via weakly-authenticated provisioning messages.
There are several smartphones manufactured by Samsung, Huawei, LG and Sony which is nearly 50 % of Android phones around the world let attackers change the malicious setting to spy the communication remotely.
Unfortunately, the recipient cannot verify whether the newly suggested settings comes from the original network operator or attacker due to the limited authentication.
Attack Flow over the Air
Attack needs to have $10 worth USB dongle which can be used to send binary SMS messages along with a simple script to compose and send the OMA CP message to the victim mobile.
This process can be performed by anyone who has has a cheap USB modem to trick the victims and install malicious settings and redirect all their traffic through the attacker-controlled proxy.
According to the checkpoint report, OMA CP allows changing the following settings over-the-air:
- MMS message server
- Proxy address
- Browser homepage and bookmarks
- Mail server
- Directory servers for synchronizing contacts and calendar
Researchers test the attack using Samsung smartphone by sending an unauthenticated OMA CP message. meanwhile, they noticed that there is authenticity check when victims receive the CP messages and just accept the CP message is enough to install the malicious settings.
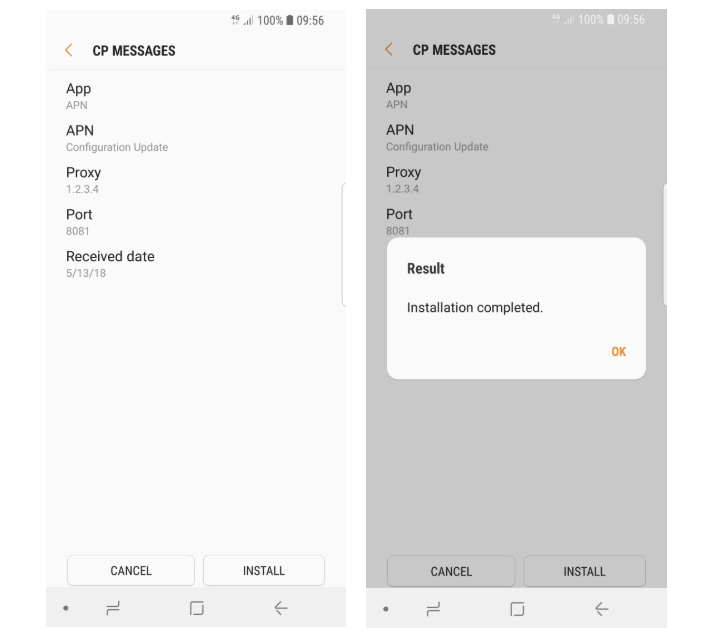
Also if the attacker wants to perform this attack on Huawei, LG or Sony phones, it requires to obtain the International Mobile Subscriber Identity (IMSI) numbers and it can be obtained via an Android application having READ_PHONE_STATE permission.
“For those potential victims whose IMSI could not be obtained, the attacker can send each victim two messages. The first is a text message that purports to be from the victim’s network operator, asking him to accept a PIN-protected OMA CP, and specifying the PIN as an arbitrary four-digit number Checkpoint researchers said.
Once it’s done, the attacker sends him an OMA CP message authenticated with the same PIN. Such CP can be installed regardless of the IMSI, provided that the victim accepts the CP and enters the correct PIN.
By successfully install the malicious settings through a single SMS phishing attack, attackers gain full access to the emails from built-in email client in Android phones and web browsers home page.
Researcher successfully testing this attack with Huawei P10, LG G6, Sony Xperia XZ Premium, and a range of Samsung Galaxy phones, including S9.
Checkpoint found this flaw in March and reported to the specific vendors to apply the fixed to prevent the users from this advanced phishing attack.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and Hacking News update.







