

Cryptocurrency stolen by North Korean hackers has been seized by the FBI and private investigators for a value of approximately $30 million. There has never been a case where stolen cryptocurrency has been seized from a North Korean hacking group.
In March of this year, a video game company was robbed of $30 million worth of cryptocurrency by government-supported hackers. There is a worrying trend in crypto crime right now that is one of the most troubling – specifically, the theft of funds from:
- DeFi protocols
- Cross-chain bridges
A large amount of cryptocurrency has already been stolen from the DeFi protocol so far in 2022 by North Korean-linked hacker groups.
Approximately 10 percent of the stolen cryptocurrency is represented by seized funds. As of the time of the theft in March, the total value of the stolen funds was approximately $620 million from Ronin Network, it’s a sidechain that is designed for Axie Infinity, a game with a play-to-earn model.
These seizures were largely made possible by the Chainalysis Crypto Incident Response team. Assisting law enforcement agencies and industry players by using advanced tracing techniques and liaising with them to quickly freeze the stolen funds and follow them to cash out points.
Hacked Ronin Bridge
A number of private keys held by Ronin Network’s cross-chain bridge transaction validators were obtained by the Lazarus Group during the attack.
Two transactions were approved using this majority, both of which were withdrawals, as follows:-
- One for 173,600 ether (ETH)
- The second one was for 25.5 million USD Coin (USDC)
A laundering process was then initiated, and Chainalysis began tracking the funds to find out where they came from.
Until now, more than 12,000 crypto addresses have been used to launder these funds in order to hide their origins. Clearly, this illustrates the high degree of sophistication at which the hackers were able to launder money.
Laundering Stages
There are five stages in the typical North Korean DeFi laundering process, and here below we have mentioned them:-
- Stolen Ether sent to intermediary wallets
- Ether mixed in batches using Tornado Cash
- Ether swapped for bitcoin
- Bitcoin mixed in batches
- Bitcoin deposited to crypto-to-fiat services for cashout
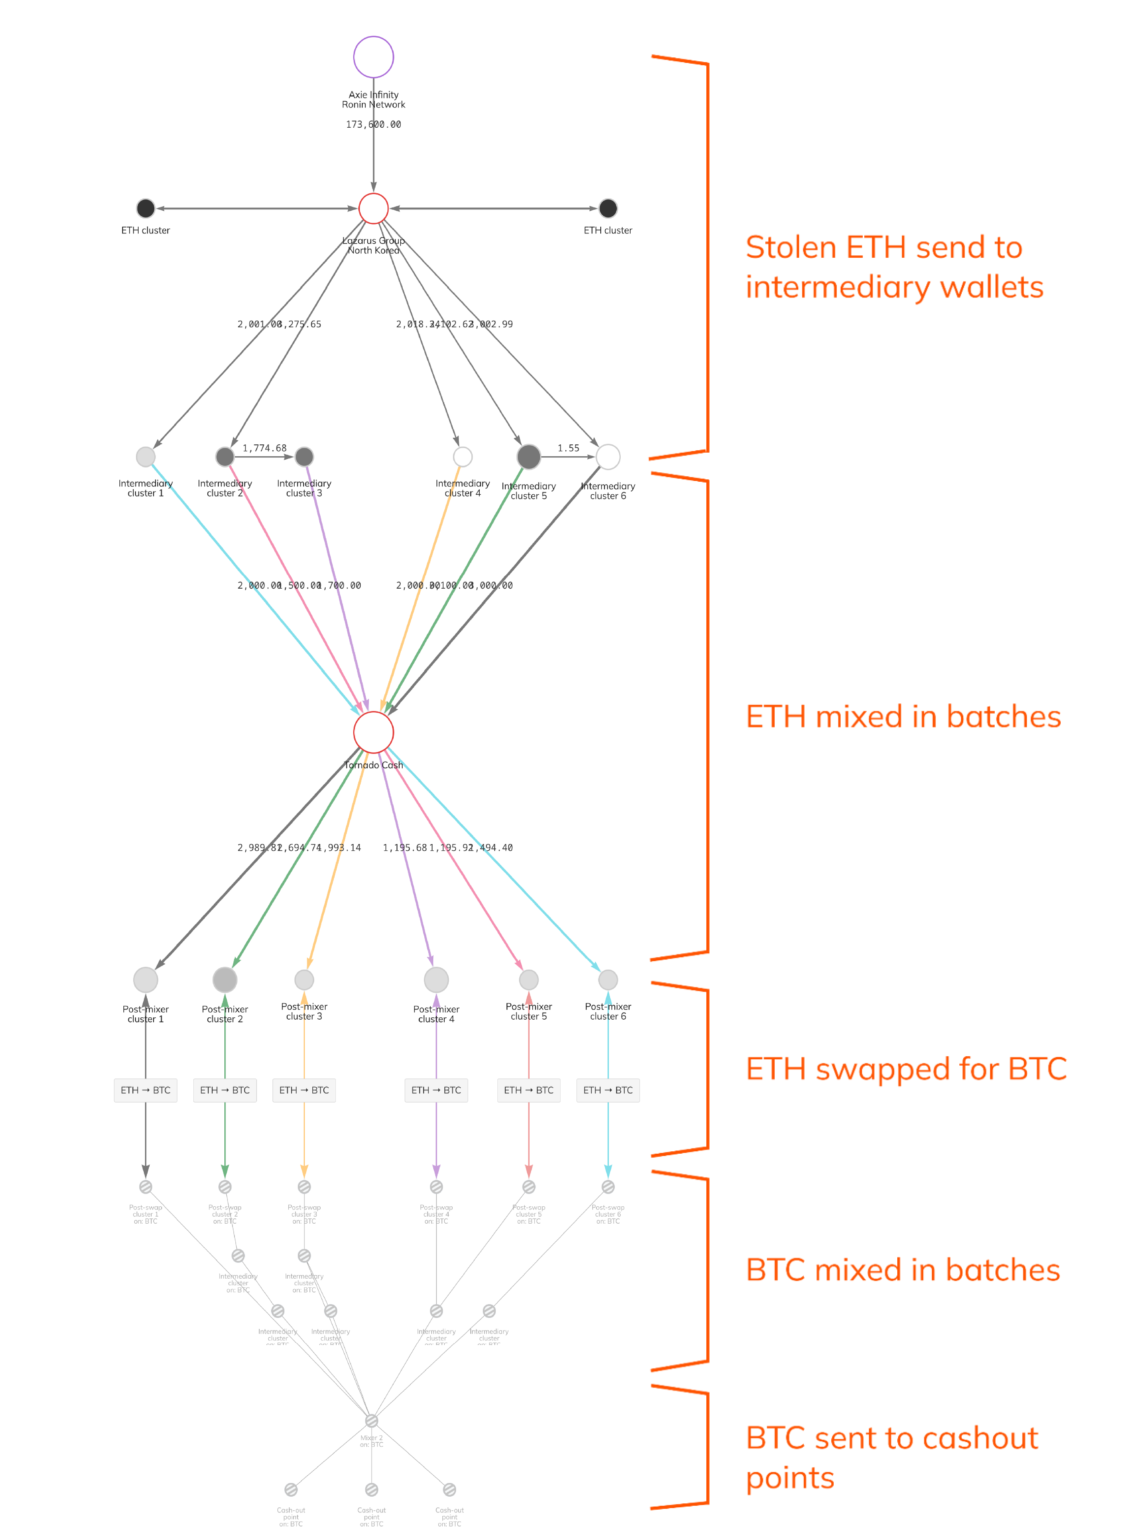
Tornado Cash, however, has been sanctioned by the US Treasury’s OFAC in response to its involvement in money laundering. There has been a shift away from the Ethereum mixer by Lazarus Group since then.
In the investigation of hacks such as the one suffered by Axie Infinity, the transparency of cryptocurrency plays an essential role.
In order to understand and disrupt the laundering activities of cybercrime organizations, investigators need to have access to the right tools. There are two key things that need to be stressed: transparency and collaboration.
Download Free SWG – Secure Web Filtering – E-book







