

In an attack campaign dubbed “Operation Digital Eye,” a suspected China-nexus threat actor has been observed targeting business-to-business IT service providers in Southern Europe.
The attack operation lasted roughly three weeks, from late June to mid-July 2024. The intrusions could have allowed the attackers to gain a strategic foothold and compromise downstream entities.
In particular, threat actors exploited Visual Studio Code and Microsoft Azure infrastructure for C2 purposes, attempting to avoid detection by disguising illicit activity as legitimate.
“Our visibility suggests that the abuse of Visual Studio Code for C2 purposes had been relatively rare in the wild before this campaign.
Operation Digital Eye marks the first instance of a suspected Chinese APT group using this technique that we have directly observed”, Tinexta Cyber and SentinelLabs researchers.
Leveraging 2024 MITRE ATT&CK Results for SME & MSP Cybersecurity Leaders – Attend Free Webinar
Chinese APT via Visual Studio Code Tunnels
The Microsoft Visual Studio Code Remote Tunnels technology, which initially emerged to facilitate remote work, offers complete endpoint access, including the ability to execute commands and manipulate files.
Furthermore, Visual Studio Code tunneling uses Microsoft-signed executables and Microsoft Azure network infrastructure, both of which are frequently not closely watched and are normally permitted by firewall rules and application restrictions.
Because of this, this method might be difficult to identify and could bypass security measures. This makes Visual Studio Code tunneling a compelling and potent tool for threat actors to take advantage of, especially when combined with the complete endpoint access it offers.
To get access to database servers and web servers that are visible to the Internet, the attackers first used SQL (Structured Query Language) injection.
The web traffic logs discovered showed User-Agent request headers, which indicates the attackers automated the identification and exploitation of SQL injection vulnerabilities using the sqlmap tool.
The threat actors used a PHP-based web shell named PHPsert to gain initial access and sustain ongoing access.
“To disguise the files implementing PHPsert and attempt to evade detection based on filesystem activity, the attackers used custom names tailored to the infiltrated environments, making the file names appear legitimate”, researchers said.
“This included using the local language and terms that aligned with the technological context of the targeted organizations”.
The threat actors used a range of third-party applications and built-in Windows programs to perform reconnaissance after gaining an initial footing.
to the Local Security Authority Subsystem Service (LSASS) process using the CreateDump tool.
The threat actors frequently named the files they deployed using the pattern do.* The attackers used pass-the-hash methods and RDP (Remote Desktop Protocol) connections to migrate laterally across the internal network from the initial compromised endpoints.
Further, they employed a specially modified version of Mimikatz, which was implemented in an executable called bK2o.exe, for the pass-the-hash attacks.
Visual Studio Code Remote Tunnels, built on Microsoft’s dev tunnel technology, allow developers to access and work on remote systems.
Activities such as execution of commands and modifying files are made possible by this access, which also includes the file system and command terminal.
The threat actors installed a portable Visual Studio Code executable called code.exe, which is digitally signed by Microsoft, and used the winsw tool to execute it as a Windows service.
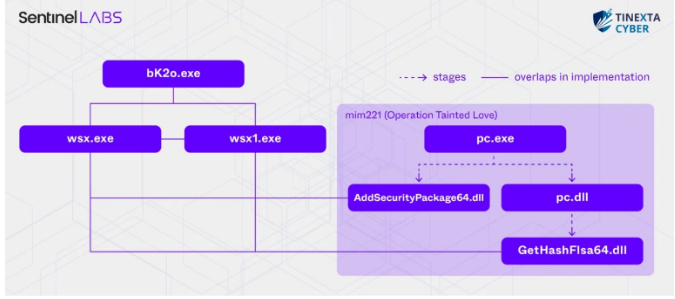
Further, wsx.exe, wsx1.exe, mim221 components that were used in Operation Tainted Love, and simplify_32.exe were used in Operation Soft Cell.
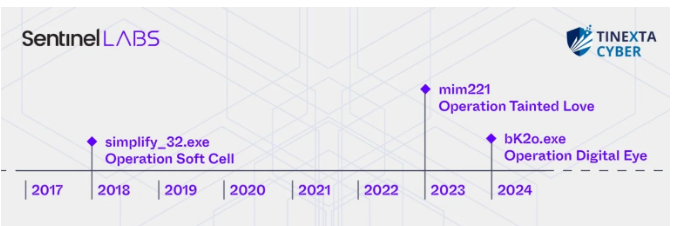
“We assess that Operation Digital Eye was highly likely conducted by a China-nexus cluster with cyberespionage motivations. The specific group responsible remains unclear due to the extensive sharing of malware, operational playbooks, and infrastructure management processes among Chinese APT clusters”, researchers said.
According to the research, the operators were most active in the networks of the targeted organizations between 9 a.m. and 9 p.m. CST, which is the average working hour in China.
According to an earlier study, a suspected North Korean gang has been using Visual Studio Remote Tunnels to stay persistent in a hacked network since 2023.
Further, threat actors disseminated a Windows Shortcut (LNK) file to launch Visual Studio Code and turn on its tunneling functionality to provide remote access, according to a report published by Cyble in October 2024 that detailed unattributed activities.
Unit 42 released a report in September 2024 on a campaign that used Visual Studio Code as a backdoor to target Southeast Asian government entities. The campaign was credited to Stately Taurus (also known as Mustang Panda).
Chinese APT groups frequently adopt pragmatic, solution-focused strategies to avoid detection, as demonstrated by this campaign’s abuse of Visual Studio Code Remote Tunnels.
This necessitates that defenders reevaluate conventional security methods and establish strong detection systems in place to spot such evasive tactics instantly.
Investigate Real-World Malicious Links,Malware & Phishing Attacks With ANY.RUN - Try for Free


