

A sophisticated malware campaign dubbed GitVenom has infected over 200 GitHub repositories, targeting developers with fake projects masquerading as legitimate tools.
The repositories, active for nearly two years, deploy stealers, remote access Trojans (RATs), and clippers to compromise systems and steal sensitive data, including cryptocurrency wallets.
According to the Kaspersky Report, Security researchers estimate the threat actors behind GitVenom have stolen at least 5 BTC (≈$485,000) through this operation.
Campaign Mechanics and Evasion Tactics
The malicious repositories impersonate popular developer tools, including Telegram bots, Valorant hacking utilities, Instagram automation scripts, and Bitcoin wallet managers.
To evade detection, attackers meticulously craft README.MD files in multiple languages, complete with installation guides, usage examples, and troubleshooting tips.
For example, a Python-based “Instagram follower bot” repository included step-by-step instructions for configuring API keys—a tactic meant to build trust before deploying malware.
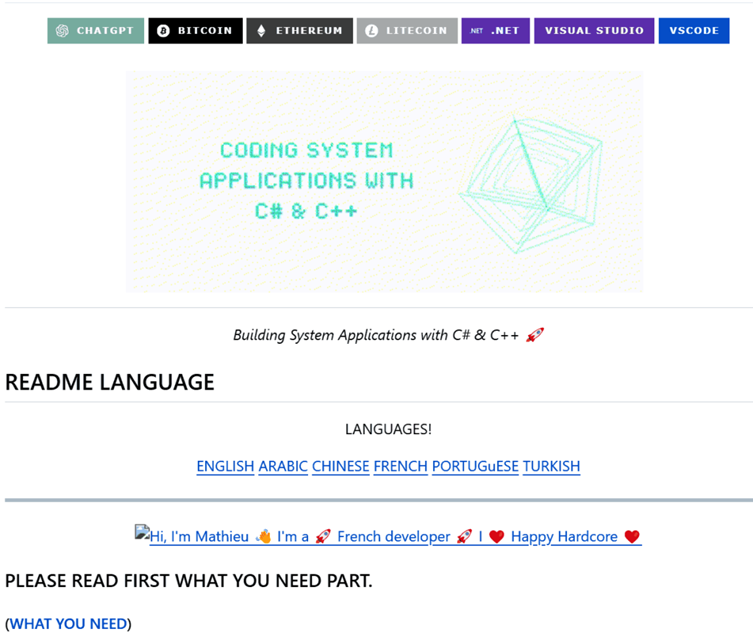
Attackers used AI to write detailed instructions in multiple languages
Automated Commit Spoofing
Attackers automated repository activity by generating timestamp-based commits every few minutes, creating the illusion of active maintenance.
One repository logged over 12,000 commits in six months, mimicking the update patterns of legitimate open-source projects.
This strategy helped malicious repositories evade GitHub’s default “sorted by recently updated” filters, pushing them higher in search results.
Malware Payloads and Financial Impact
GitVenom’s repositories span Python, JavaScript, C, C++, and C#, broadening their attack surface. Malicious payloads include:
- Node.js Stealer: Harvests usernames, passwords, browser history, and cryptocurrency wallet data, compresses it into a .7z archive, and exfiltrates it via Telegram bots.
- AsyncRAT: An open-source RAT enabling keylogging, screen capture, and remote command execution.
- Clipper Malware: Scans clipboards for cryptocurrency addresses and substitutes them with attacker-controlled wallets. In November 2024, one wallet linked to this campaign received a single 5 BTC transfer.
Victims span Russia, Brazil, Turkey, and Southeast Asia, with lures tailored to regional developer interests.
Brazilian repositories promoted “CPF generators” (national ID tools), while Turkish repos advertised VPN bypass tools for streaming platforms.
Experts recommend manually reviewing code dependencies before integration, particularly for projects lacking two-factor authentication (2FA) among contributors.
Attackers frequently used single-contributor accounts created days before repository publication.
- Audit Stars and Forks: Legitimate projects typically accrue organic engagement over time. A repository with 200 stars but only two forks may indicate bot activity.
- Monitor Direct Links: Avoid downloading repositories shared via unsolicited messages or unverified forums. Attackers often use URL shorteners to mask GitHub links.
The GitVenom campaign underscores the escalating risks of supply chain attacks in open-source ecosystems.
As threat actors refine their social engineering tactics, developers must adopt defensive practices—from rigorous code audits to endpoint protection tools.
GitHub has removed the identified repositories, but researchers warn copycat campaigns are inevitable.
Vigilance remains the cornerstone of cybersecurity in an era where malicious innovation outpaces traditional defenses.
Free Webinar: Better SOC with Interactive Malware Sandbox for Incident Response, and Threat Hunting - Register Here







