

The experts of ESET telemetry have recently declared that the attack rate of Stalkerware for Android is increasing rapidly. As per the report of 2020, nearly 48% of attacks have increased as compared to the 2019 attack rate.
However, Stalkerware generally monitors the GPS location of victims’ devices, conversations, pictures, browser history, and many more. Not only this the analysts also claimed that Stalkerware also stores and transmits all this data as per their requirements.
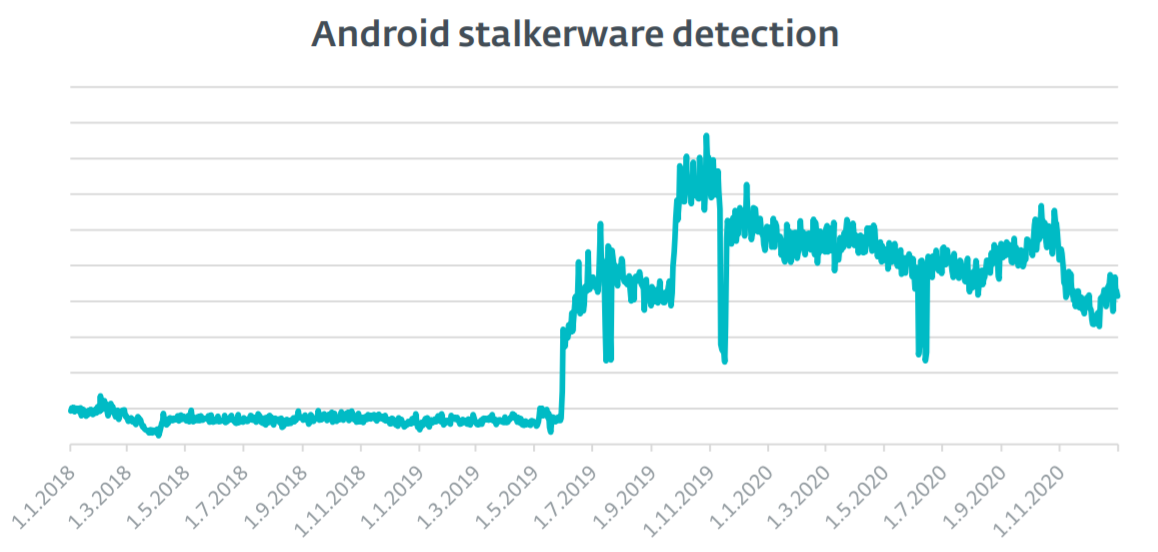
Stalkerware apps have become quite popular in the last couple of years, and in a regular investigation, the security researchers found that some Stalkerware keeps a lot of data regarding the stalkers, using the app and collecting all the data of victims’ on a server.
Over 150 Security Flaws in 58 Stalkerware apps
The security specialists at ESET have detected a total of 158 privacy and security issues in 58 Android Stalkware apps.
All these issues belong to several vendors that are enabling the threat actors to take control of a victim’s device, and later they can hijack a stalker’s account, administer remote code execution, intercept data, and the hackers can also frame the victim by uploading counterfeit evidence.
Security Issues
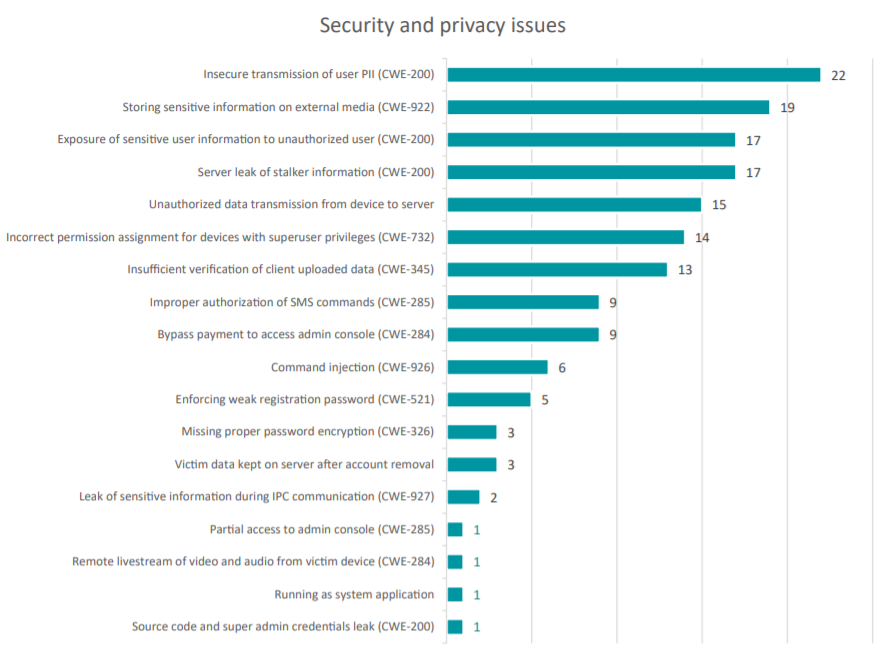
As we told that the researchers have discovered 158 security and privacy issues in 58 Stalkerware apps, and all these issues were ordered as per the prevalence of their occurrence, which has been found in the scrutinize Stalkerware.
However, after a proper analysis, the analysts have asserted that in this type of attack, the stalker counterspy upon the victims through the Stalkerware.
Most Widespread Issues
Here we have mentioned below all the widespread issues:-
- Among the nine different App vendors, one provider using a Metasploit payload as a monitoring app, and all these apps are based on Droid-Watcher, it’s an open-source Android spyware.
- Personally identifiable information of users was transmitted by 22 apps over an unencrypted connection to the Stalkerware server.
- Easy theft of software is being allowed by some apps that have hardcoded license keys in cleartext.
- Among the 58 Android apps, 19 of them collect all the sensitive information of the users.
- 17 Android apps have leaked the data of the client, and it’s enabling a victim to collect data of the stalker using the IMEI number of the device.
- Nearly, 17 apps reveal user data that were stored in the servers to unauthorized users, outwardly requiring any authentication.
- Immediately after installation, 15 apps were detected that transmit unauthorized data from a device to the servers, before the stalker registers.
- 13 apps have insufficient verification protections for the data that is being uploaded from the victim’s phone.
The cybersecurity authorities have warned all the potential future clients of Stalkerware, regarding the usage of the software against their partners and loved ones.
Apart from this, they have also detected that there are some Stalkerware that are keeping information about the stalkers just by using the app and collected the data of their victim on a server.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.







