
A newly disclosed Windows zero-day, YellowKey, is attracting significant attention because it can bypass BitLocker protection and expose data on encrypted drives without requiring the victim’s recovery key in the public attack scenario described by researchers and media reports.
The issue was published by the researcher known as Nightmare-Eclipse, who released materials showing attacks against Windows 11, Windows Server 2022, and Windows Server 2025.
The disclosure is serious because BitLocker is widely trusted as a last line of defense when a laptop, workstation, or server falls into the wrong hands. In YellowKey’s currently public form, the attacker needs physical access to the target device.
However, experts still view that as a high-impact risk because the attack can lead to unrestricted access to the protected volume after a reboot into recovery mode.
Windows BitLocker 0-Day
Available reporting indicates that YellowKey does not break BitLocker’s encryption algorithm itself. Instead, the weakness appears to lie within the Windows Recovery Environment (WinRE), where a trusted recovery component can be abused to unlock access in ways defenders did not expect.
Reports say the attack uses specially prepared files placed on a USB device, and another documented variation involves writing those files to the EFI system partition, which is normally outside BitLocker protection.
Once the system boots into recovery mode, the vulnerable component can parse the file structure and open a shell with access to the BitLocker-protected drive.
Security researcher Will Dormann highlighted what he called the more important detail: the FsTx log on the removable media appeared able to modify files on a different volume when replayed by WinRE.
That finding suggests YellowKey may point to a deeper flaw in how Windows recovery handles cross-volume NTFS transaction replay, meaning the full security impact may be broader than the BitLocker bypass alone.
The public mitigation picture is still unclear. Some reports said a BitLocker PIN, along with a BIOS password, could help reduce exposure.
Still, later updates said the original researcher claimed there is also a variant that can work even in TPM-plus-PIN environments, although that version was not publicly released.
Affected systems
One important detail is that Windows 10 was not reported as affected in the same way. That points to a problem tied to newer WinRE behavior in Windows 11 and recent server editions rather than to every BitLocker deployment across Microsoft’s product line.
Independent security researcher Kevin Beaumont confirmed that the YellowKey exploit is valid, which gave the disclosure immediate credibility beyond the original repository posting.
At the time of those reports, YellowKey was still being described as an unpatched zero-day, increasing concern that public proof-of-concept material could accelerate copycat experimentation.
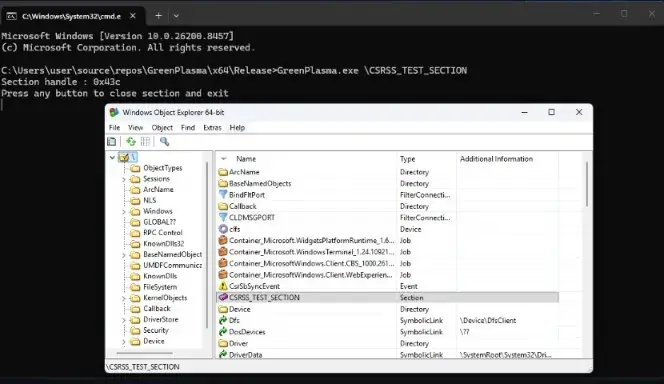
YellowKey did not arrive alone. The same researcher also published GreenPlasma, a separate Windows flaw involving CTFMON and arbitrary section creation that could be used to develop a local privilege-escalation path on Windows 11 and Windows Server 2022 and 2025.
That pairing matters because Nightmare-Eclipse has already released other Windows exploitation projects this year, including BlueHammer, RedSun, and UnDefend. Security firms previously linked that earlier tooling to real-world intrusion activity, showing how quickly public Windows exploit research can move from online release to operational abuse.
For defenders, YellowKey is a warning that full-disk encryption alone cannot protect a device if recovery paths, removable media access, and physical security controls are left exposed.
Until Microsoft provides clearer guidance or a fix, organizations using Windows 11 and affected server platforms may need to review BitLocker protector settings, WinRE exposure, and physical access assumptions much more closely.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.







