

Researchers discovered a widespread Iranian malware campaign called Fox Kitten that targeting the several organization networks by exploiting the Vulnerabilities in VPN.
The organization its targets are mainly related to IT, Telecommunication, Oil and Gas, Aviation, Government, and Security sectors around the world.
Once the attacker successfully exploited the network, they are gaining the persistence access to the internal system and foothold in the networks of numerous companies.
Fox Kitten campaign believed to be originated from Iran, and infamous Iranian offensive group APT34-OilRig are behind this attack also researchers suspected that this campaign has some connection with PT33-Elfin and APT39-Chafer groups.
Large infrastructure is used for this campaign to perform a various malicious operation on behalf of the attack including:
- Develop and maintain access routes to the targeted organizations
- Steal valuable information from the targeted organizations
- Maintain a long-lasting foothold at the targeted organizations
- Breach additional companies through supply-chain attacks
As we have reported several malicious campaigns that involved by the APT34 threat actors group and among those attacks, This is one of the high profile targeting cyberattack that currently encounter by the ClearSky researchers.
During the attack, Threat actors are using several hacking tools that contain several open sources tool available on the internet and some of them are self-developed on their own.
Exploiting Bugs for The Initial Breach
Threat actors from APT 34 initially breaching the targeted organization network by exploiting the vulnerabilities in VPN such as Pulse Secure VPN, Fortinet VPN, and Global Protect by Palo Alto Networks.
Once the obtain the network, an attacker using a variety of communication tools, including opening RDP links over SSH tunneling for encrypted communication and try to maintain the access in the infected network.
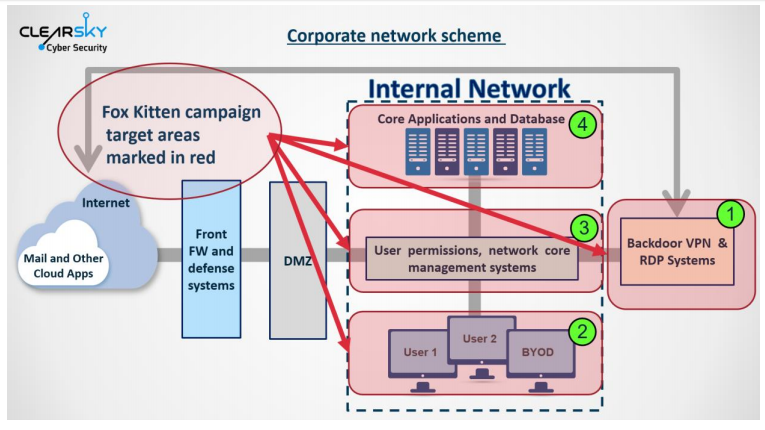
There are several hacking tools are identified that includes self-developed tools: STSRCheck, POWSSHNET, VBScript, Socket-based backdoor over cs.exe, Port.exe and open souce tools such as Invoke the Hash, JuicyPotato, and some of the legitimate tools including Ngrok, FRP, Serveo, Putty and Plink .
These tools are using various purposes in this attack such as privilege escalation, foothold ensuring, and creating a gap for RDP connection and information theft.
According to the ClearSky research ” The main VPN systems exploited by the attackers are Pulse Secure Connect, Global Protect (by Palo Alto Networks), and Fortinet FortiOS. We assess with a high probability that vulnerabilities in Citrix will be used by the attackers as well. “
Researchers also found that the attackers created a special local admin user at the infected network to maintain the high permissions at the station even if the password of the station owner’s main user will be changed.
After gaining successful access to the targeted computer, attackers start moving files from the compromised computer to their own computers through the exfiltration channel.
“This stage’s main concept is establishing the ability to connect, through RDP, to the target company, categorizing relevant files either by looking at them online or through filename lists, and then exfiltrating them to the attacker in different ways. Researchers said”.
At the end of the attack, after successfully infiltrating the organization, the attackers have performed a routine process of identification, examination, and filtering of sensitive, valuable information from every targeted organization.
Also Read: Most Dangerous APT Hacker Group’s Deadly Cyber Attacks of the Year 2019-2020 – Complete Collection
Follow us on Twitter, Linkedin, Facebook for Daily cyber security & hacking news updates.







