

he hackers behind the TrickBot Malware has updated their new propagation module known as “Nwrom.” As people are very familiar with the TrickBot malware, but this time, it appears with a new propagation module.
Now many of you must be thinking that what is different about this propagation module? It is a spreading module that is generally used for stealing sensitive information, which contributes backdoor access, which later used by several illegal groups to disseminate different malware.
GBHackers Reported several TrickBot activities that were first discovered in 2016, and it usually starts with accessing the background that has been run by the user currently.
Once it gets a way to enter the computer, it gradually downloads various modules to perform different malicious tasks first in the computer and then in the network.
TrickBot modules and the modules used to spread
Well, it is a propagation module that are specifically developed to steal sensitive data by performing its different malicious infection. TrickBot is different from other malware because it uses different binaries to perform the various tasks during its whole operation.
At first, TrickBot saves the Windows executable (EXE) malicious file to the disk, which known as the “TrickBot loader.” Well, if we take two examples fo windows 10 and 7, then you may know the whole thing.

Well, if any window 10 get infected, then the TrickBot modules can only be found in system memory. Whereas in the infected Windows 7, users can additionally see artifacts that are associated with modules and are saved in the disk.
Recently TrickBot and Ransomware operators have joined hand and came together to get access to a negotiated network so that they can easily use this ransomware.
“But, the artifacts that are shown in windows 7 are encrypted binaries, and later during the operation, these encrypted binaries get decrypted and get operated from the system memory as TrickBot modules” Palo Alto Research stated.
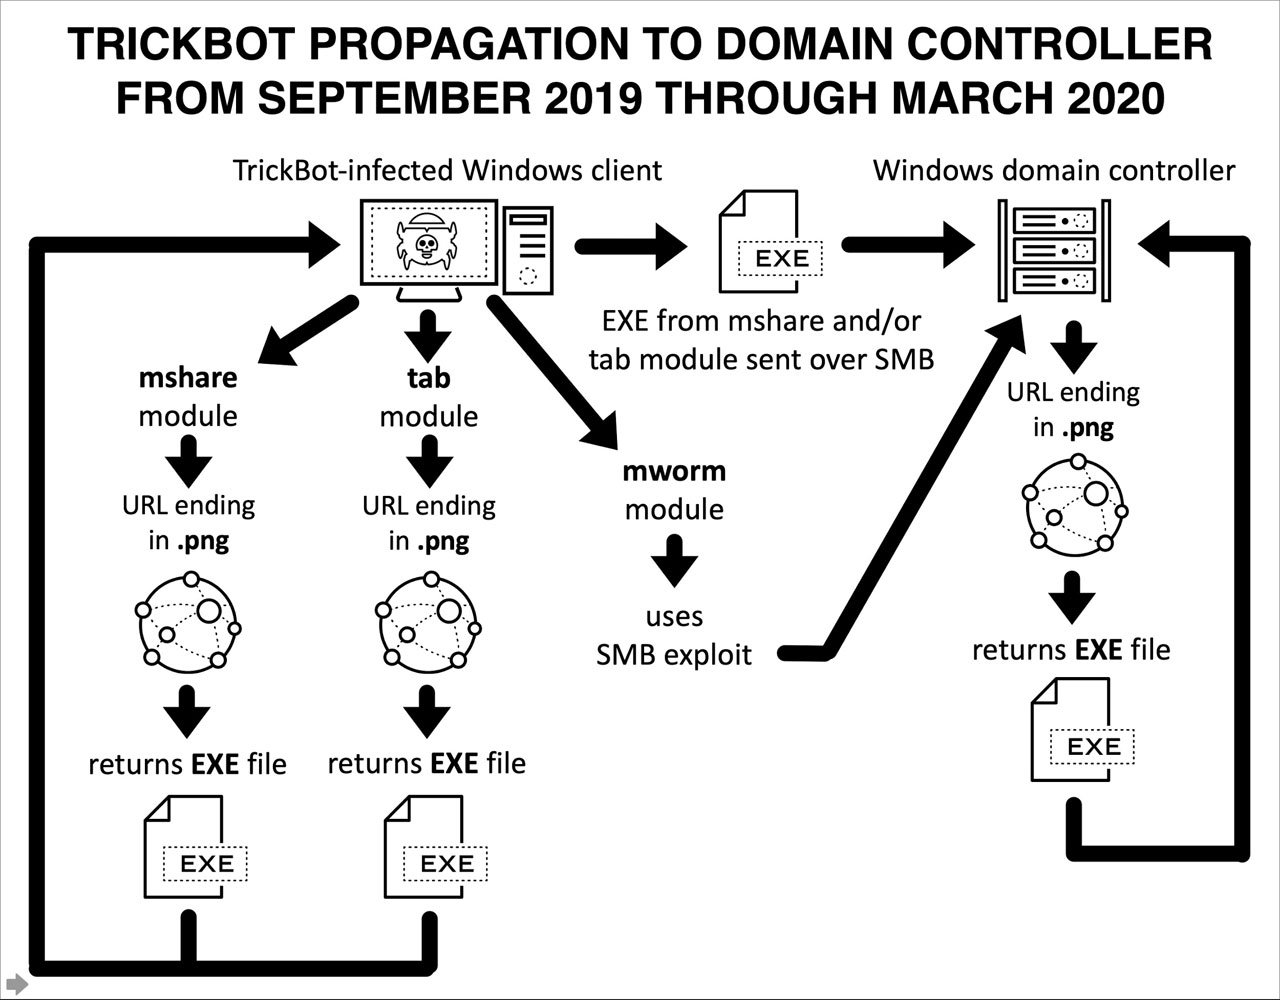
Here are the modules used by the TrickBot:-
- Mshare module
- Tab module
- Mworm module
To exploit the SMB vulnerabilities in the domain controller the module does this, and here is the chart we have mentioned below in which you can see the flow of the spread caused by the above TrickBot modules.
Goodbye Mworm: Hello “Nwrom”
Apart from this, the new nworm module also launches the infection in the memory of the domain controller, simply to make it more complex and remain undetectable, so that it can be executed without any issue.
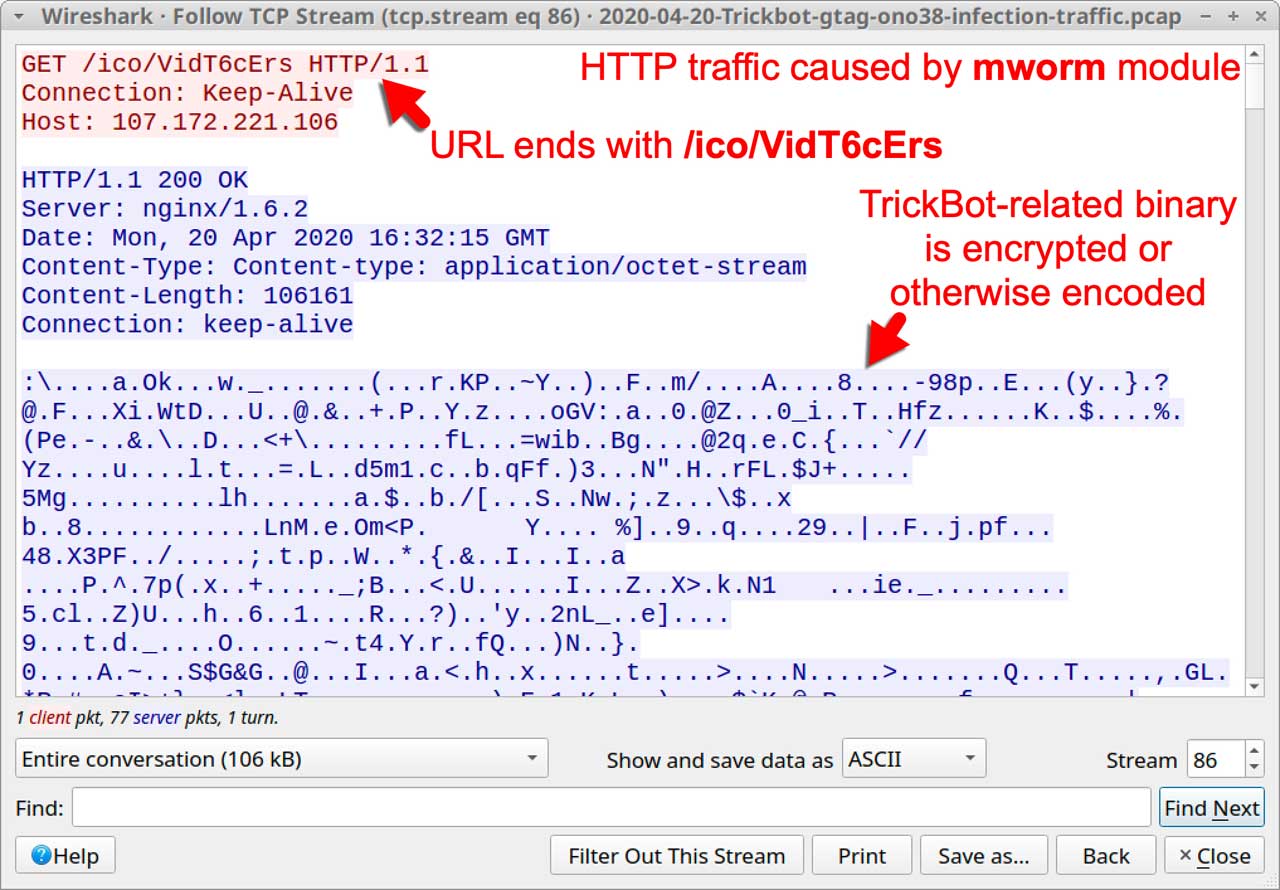
We know that TrickBot has introduced the new “Nwrom” propagation module, while in early 2020, TrickBot stopped using the “Mworm” module in one of the lab atmospheres. So, when TrickBot stops using the Mworm, then the operators of the TrickBot introduced new artifacts that are named as “Nwrom,” Which initially rose in one of the infected window 7.
Most importantly, this new module, ‘Nwrom’ does not appear until the TrickBot infection does not happen in the AD atmosphere with DC as similar to the ‘Mworm’.
So, what do you think about this? Share all your views and thoughts in the comment section below.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.







