

We all know that there are different security solutions are available to keep a firm or an organization safe and secure from cyber threats. But nowadays, all these security solutions are becoming a threat to the firm. As recently, a vulnerability has been detected in the Bit Defender antivirus, well this vulnerability allows hackers to run arbitrary code remotely.
The vulnerability was assigned CVE-2020–8102, and this vulnerability has impacted the recent update version of the Bit Defender antivirus. Moreover, the researchers claimed that this vulnerability has a powerful and dangerous impact as it has attacked an antivirus that is generally used by various users to protect their devices.
Vulnerability Details
The details that have been concluded by the researchers is that the vulnerability has Incorrect Input Validation in the Safepay browser that is the element of Bitdefender Total Security 2020.
It enables an external, specially crafted web page to operate remote commands inside the Safepay Utility process. According to the researchers, this vulnerability has affected the Bitdefender Total Security 2020 versions 24.0.20.116.
Here are the flaw details along with CVSS score:-
- CVE ID: CVE-2020-8102
- CVSS score: 8.8
- Affected vendors: Bitdefender
- Affected products: Bitdefender SafePay
Summary of The Findings
This case is entirely related to Kaspersky, and they also have similar input methods but without most of the conflicting results. But, the websites can easily acquire some security tokens from these error pages.
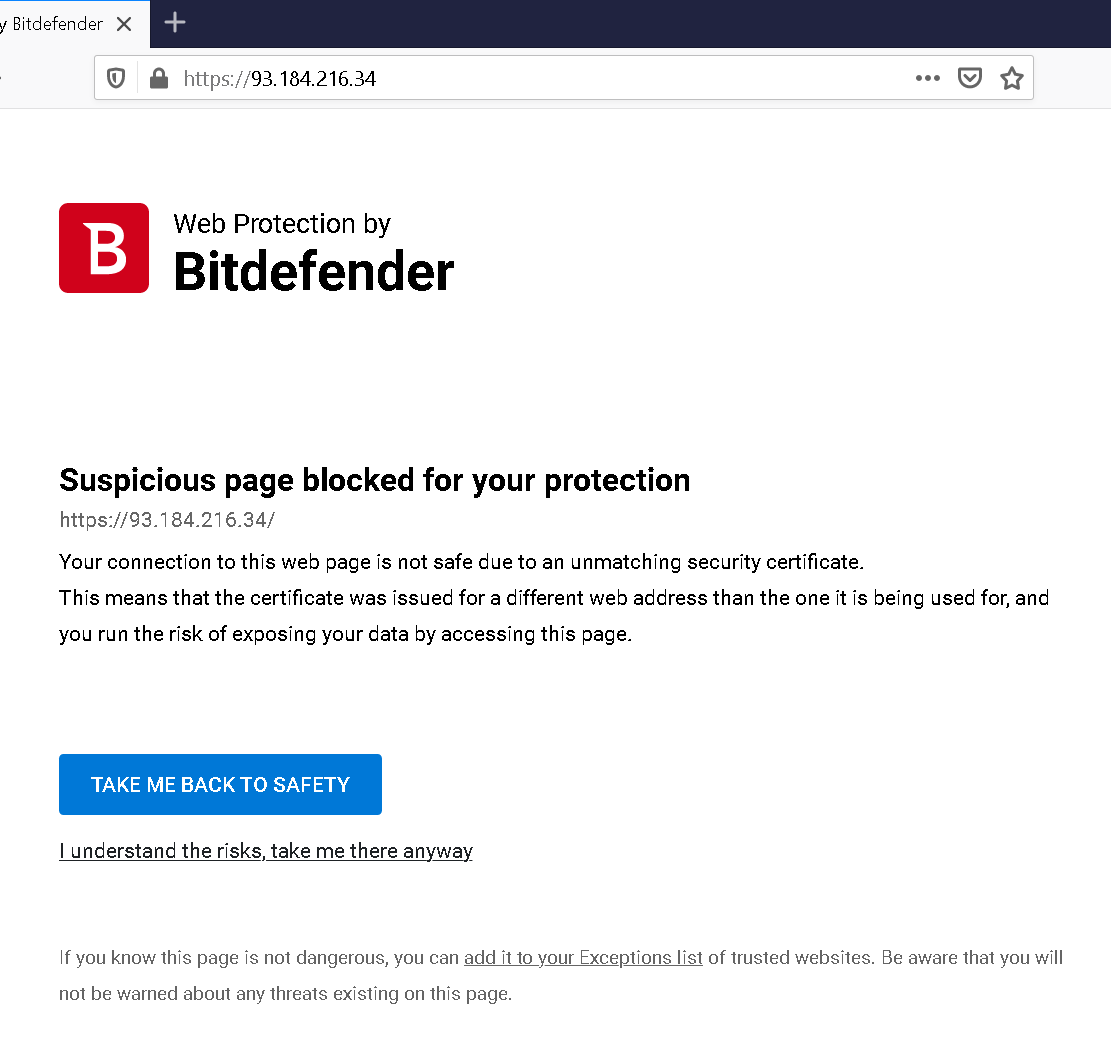
They know that these security tokens cannot be used to cancel errors on other websites, but they can utilize these tokens to start an assembly with the Chromium-based Safepay browser.
According to the Bitdefender Advisory report , there API was never intended to allow untrusted data, so it is attacked by the same vulnerability that the security experts have observed in Avast Secure Browser before.
In this case, an attacker can readily insert the command-line flags, and therefore it results in arbitrary applications commencing up.
Starting And Exploiting Banking Mode
Bitdefender provides some code template that implies how they generate code that has been injected in the banking website, with the help of this template.
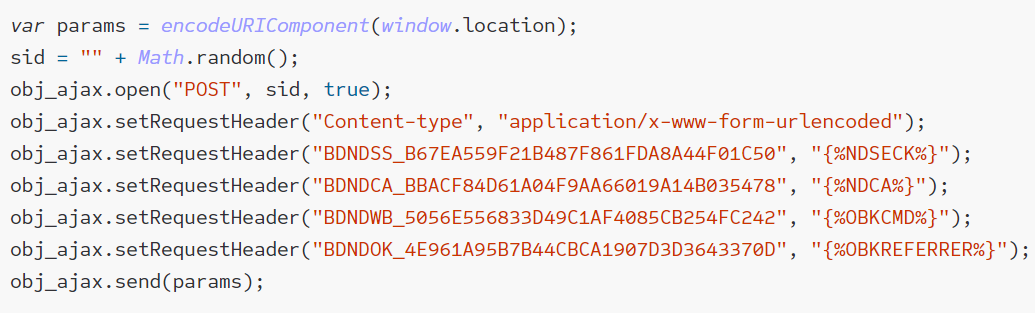
Somehow these templates are not used anymore, but we have a way to open an ill-disposed website in the Safepay browser, and it can probably negotiate all the correctly separated online banking websites operating there.
Antivirus are used to keep our devices safe, but if they are getting attacked by hackers, then it could result in a severe loss.
Moreover, Bitdefender is investigating this vulnerability by themselves, and they have now installed an automatic update that fixes this vulnerability in versions 24.0.20.116, and it will fix in all following releases.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.
Also Read:
Cisco Webex Meetings for Windows Let Hackers Gain Access to Sensitive Data
VLC Vulnerability Let Remote Hackers to Execute Arbitrary Code with User Privilege







