

Security researchers discovered new spyware used by the APT-C-23 threat group to target Android users through fake Android app store.
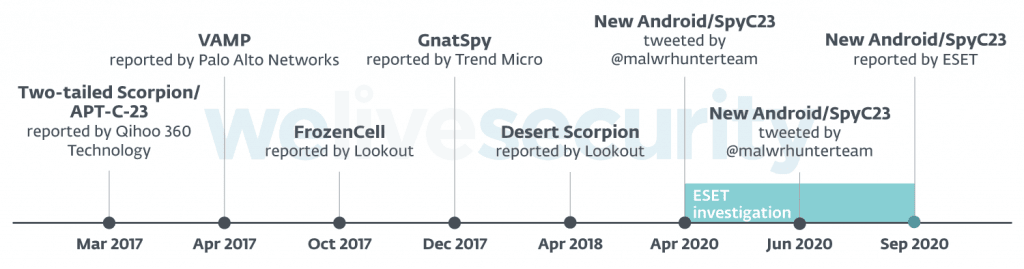
The APT-C-23, a threat group is also known as a Two-tailed Scorpion and they target mainly the Middle East. The Android spyware used by the group was first spotted in 2017, now the recent version was found to have extended spying functionality.
Earlier this year Checkpoint warned of APT-C-23 hacking group attacks targeting mobile devices, in Apri & June @malwrhunterteam tweeted about the new Android malware sample, that found to be connected.
Android Malware Via Fake App Store
ESET researchers observed a fake Android app store “DigitalApps” used by the threat actor group to distribute the malware.
The fake app store has both malicious and clean items, the non-malicious application redirects the users to another unofficial Android app store and malicious apps have malware hidden in along with its functionality.
The attackers mainly target users via the messaging apps to trick the users in requesting for number permissions that include “taking pictures and videos, recording audio, reading and modifying contacts, and reading and sending SMS.”

The following are some of the apps used by attackers to hide malware that includes AndroidUpdate, Threema, and Telegram.
Once the malware activity is initialized, in most cases, victims are requested to install a legitimate app that contains sources fo malware. The malware get’s installed in the phone silently along with the legitimate app and the spyware silently runs in the background.
When the malware is launched for the first time it records the victim to the C&C server and sends the device information to the server.
The following are the capabilities of the malware
- Take pictures
- Record audio
- Restart Wi-Fi
- Exfiltrate call logs
- Exfiltrate all SMS messages
- Exfiltrate all contacts
- Download files to the device
- Delete files from the device
- Steal files with particular extensions (pdf, doc, Docx, ppt, pptx, xls, xlsx, txt, text, jpg, jpeg, png)
- Uninstall any app installed on the device
- Steal APK installers of apps installed on the device
- Hide its icon
- Get credit balance of SIM on the device (it can get a balance by making a call to three different cellular operators: Jawwal, Wataniya, Etisalat)
- Record screen and take screenshots
- Record incoming and outgoing calls in WhatsApp
- Make a call while creating a black screen overlay activity (to hide call activity)
- Read the text of notifications from selected messaging and social media apps: WhatsApp, Facebook, Telegram, Instagram, Skype, Messenger, Viber, imo
- Dismiss notifications from built-in security apps on some Android devices:
- Dismiss its notifications (an unusual feature, possibly used in case of errors or warnings displayed by the malware)
For C&C communication attackers mainly use under maintenance websites and the communication with the C&C server is encrypted.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.
Also Read







