

Google launched the new version of Chrome (Chrome 90) recently for Windows, Mac, and Linux platforms. After the release, researchers claimed that this recent update incorporates fixes for seven security flaws.
The incorporated fixes also include a zero-day flaw that the company claims has already been exploited. The experts affirmed that CVE-2021-21224 is the fourth zero-day Chrome vulnerability that was discovered in 2021.
This vulnerability was spotted on April 5, 2021, by one of the IT security researcher Jose Martinez. This vulnerability is quite confusing and hazardous, as it continued lack of indicators of compromise or any meaningful information regarding attacks.
Zero-day Vulnerability
The zero-day vulnerability is tracked as CVE-2021-21224, and it is described as an input mismatch by the experts in the V8 rendering engine. This zero-day vulnerability had been corrected in JavaScript V8, but it was not present in the latest version of Chromium.
Along with this zero-day vulnerability, the threat actors could easily execute arbitrary code on victims’ systems. Moreover, rather than a zero-day flaw, the new release also fixes other severe security loopholes.
Moreover, Google also specifically listed the four high-severity vulnerabilities whose fixes were contributed by the external cybersecurity researchers.
Bugs Fixed
Below we have mentioned a list of bugs that were fixed in this new version of Google Chrome:-
- CVE-2021-21222 (Severity: High)
- CVE-2021-21223 (Severity: High)
- CVE-2021-21224 (Severity: High)
- CVE-2021-21225 (Severity: High)
- CVE-2021-21226 (Severity: High)
Update Your Chrome ASAP
The Zero-day vulnerability is very dangerous; that’s why Google suggests that users must go to the ‘Settings —> About Chrome’ page to manually complete the update check procedure.
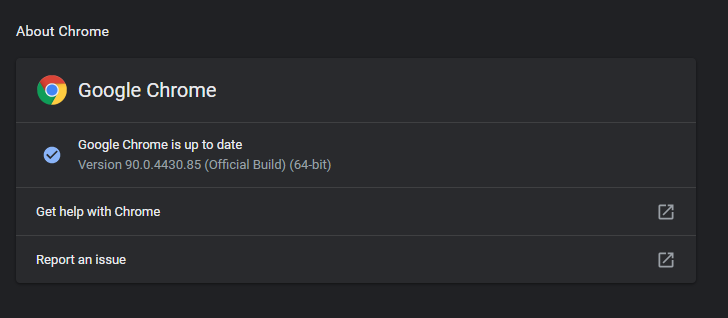
The new version of the Google Chrome browser (Chrome 90) essentially brings the developments and different changes on the security side, along with the priority opening of HTTPS pages.
Once the users are done with the automatic download and installation procedure, Chrome will eventually ask whether to restart the application to execute the update or not.
In case if any users have automatic updates enabled, then they don’t have to worry, as their Chrome will automatically update itself. Moreover, as we told earlier that one can easily update their browser by opening the About Google Chrome option from the menu bar.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity, and hacking news updates.







